Key Takeaways:
- Gives control over how users access Google apps and services on supported corporate-owned Android Enterprise devices
- Google Workspace Authentication generally available in Microsoft Intune
- Admins can provide a consistent organizational identity
- Users access to the Google Workspace resources and services assigned to that account
Let’s discuss about Requiring Google Workspace Authentication in Intune Ties Corporate Androids to Real User Identities. This policy in Microsoft Intune allows organizations that use Google Workspace to require users of corporate-owned Android Enterprise devices to authenticate using their managed Google Workspace organizational identity, rather than just a generic managed Google Play account.
Table of Contents
Table of Contents
Requiring Google Workspace Authentication in Intune Ties Corporate Androids to Real User Identities
Previously, setting up a corporate Android device through Microsoft Intune relied on an invisible, generic managed Google Play account solely to push apps and policies in the background. Because this dummy account was not connected to a real user identity, employees could not seamlessly access their Google Workspace apps without manually signing in separately.
With Microsoft Intune’s new authentication policy, IT administrators can now require users to sign in directly with their verified corporate Google Workspace account on corporate-owned Android Enterprise devices. This bridges the gap between device management and user identity, giving employees instant access to Google services while ensuring full organizational accountability.
- Microsoft Intune Adds 10 New Protected Apps for iOS and Android
- Evolution of Android Management for Enterprise Use | Deep Dive with Joy
- Understanding Android Management with Intune | Android Enterprise
Applicable Android Enterprise Enrollment Types
This policy need some requirements. This feature doesn‘t impact the Microsoft Entra account associated with the managed device. The following are the Android Enterprise enrollment types. Note that, Corporate-owned dedicated devices aren’t supported because they aren’t associated with an individual user.
| Requirements |
|---|
| Android Enterprise corporate-owned, fully managed devices |
| Android Enterprise corporate-owned devices with a work profile |
| Android Enterprise personally owned devices with a work profile managed through the Android Management API |
How to Google Workspace Authentication
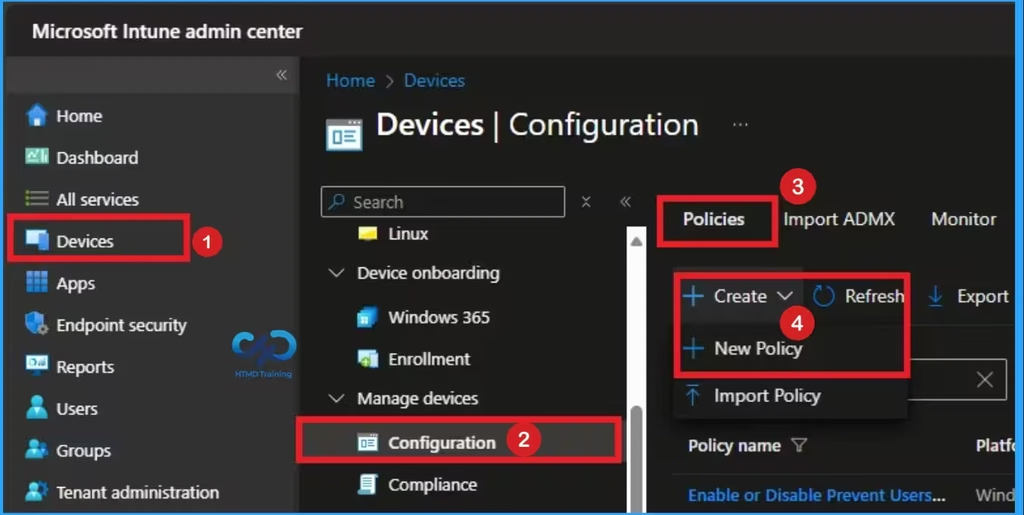
To configure this policy, Your organization’s domain must be verified in the Google Admin console. Your Intune tenant’s Managed Google Play enterprise must be upgraded to a managed Google domain enterprise (linking your Microsoft Entra account to Google). Sign in Intune Admin Center portal. Go to Manage devices > Configuration > Create > New policy.
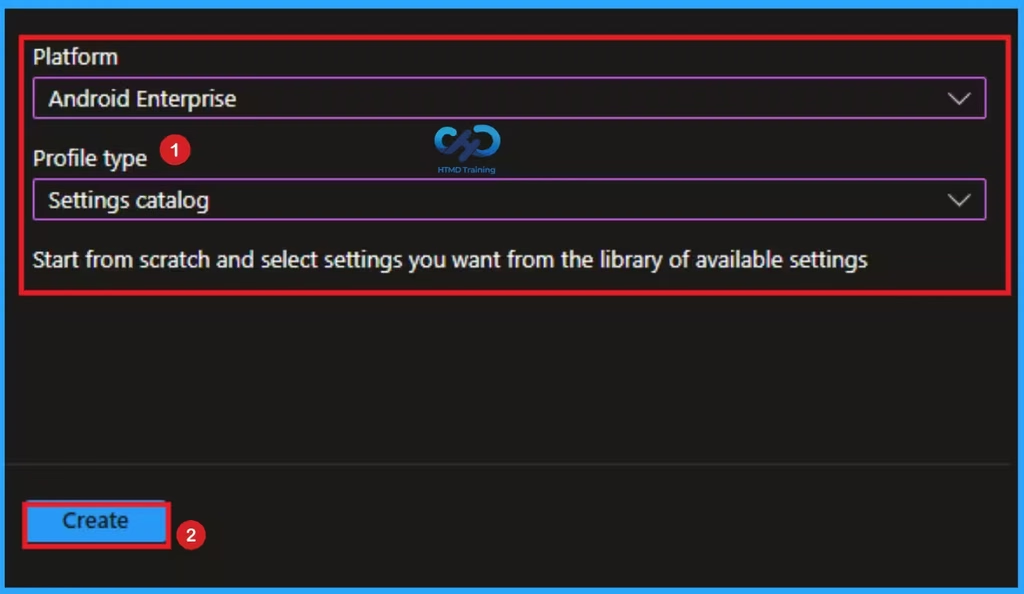
Choosing Profile and Platform
After that, you can Create a Profile for the policy which you want to configure. To create a profile you have to select platform and profile type. Here I selected Android Enterprise as the Platform and Settings catalog as the profile type. Then click on the Create button.
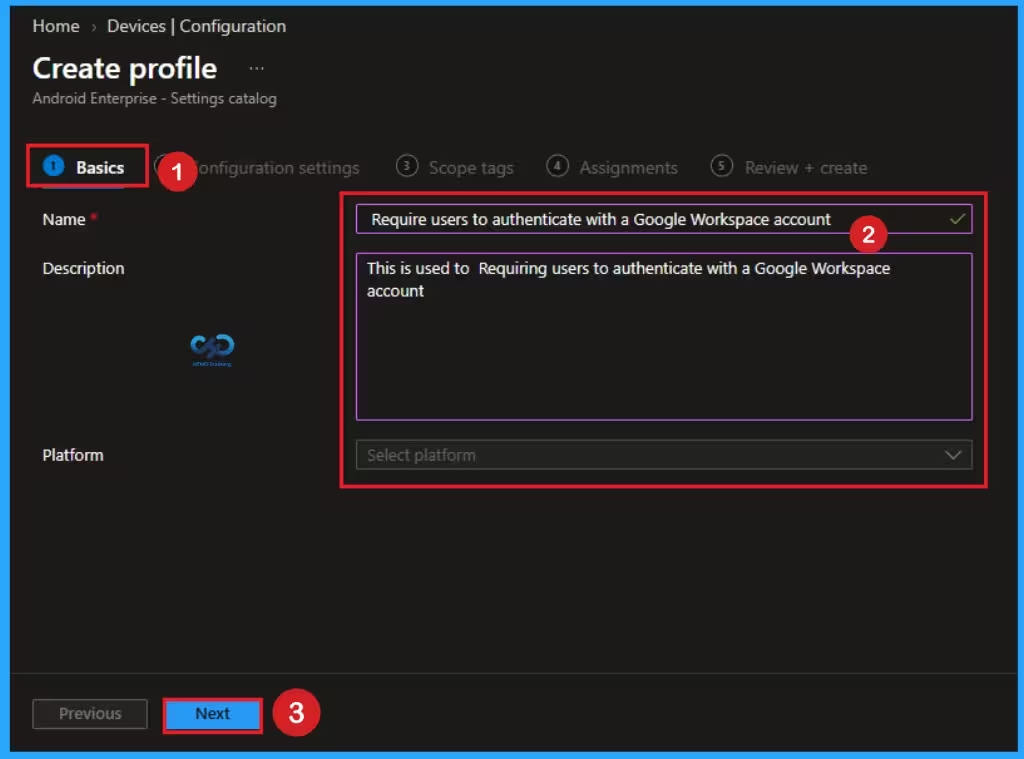
Naming Policy with Basic Tab
Basic Tab is used to give an identity for the policy by adding name and description. Here Name is Mandatory and Description is optional. After adding these details click on the Next button.
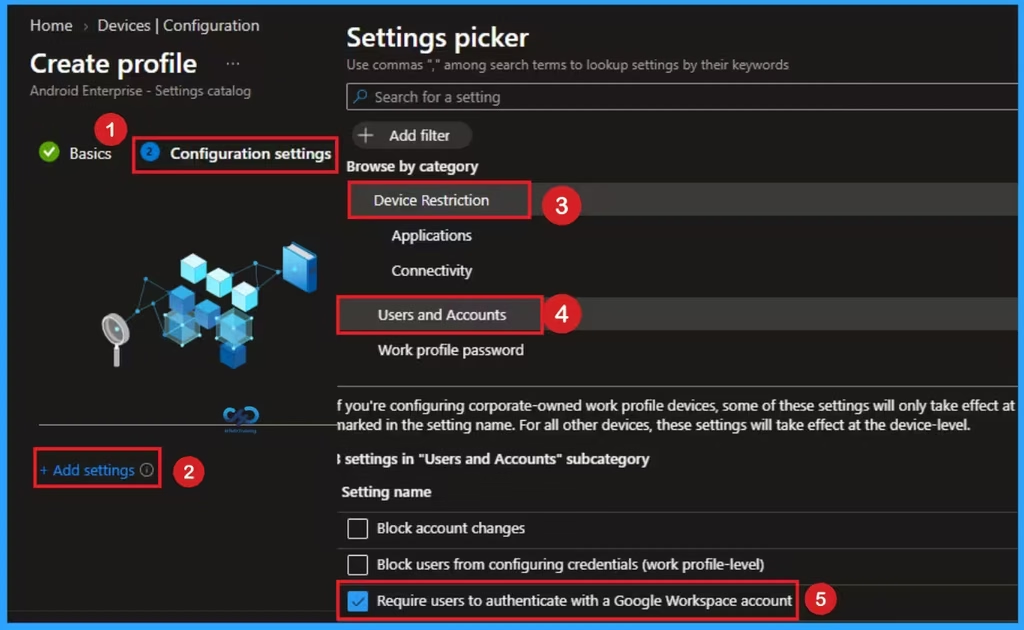
Configure Local Fonts Permission from Settings Picker
The Configuration settings page is helps to select specific settings to create the policy. The Settings Catalog provides a huge number of settings. To select a settings click on the +Add settings hyperlink. Then you will get Settings Picker. Choose Device restrictions > Users and Accounts > Require users to authenticate with a Google Workspace account setting. Then I close the Settings Picker.
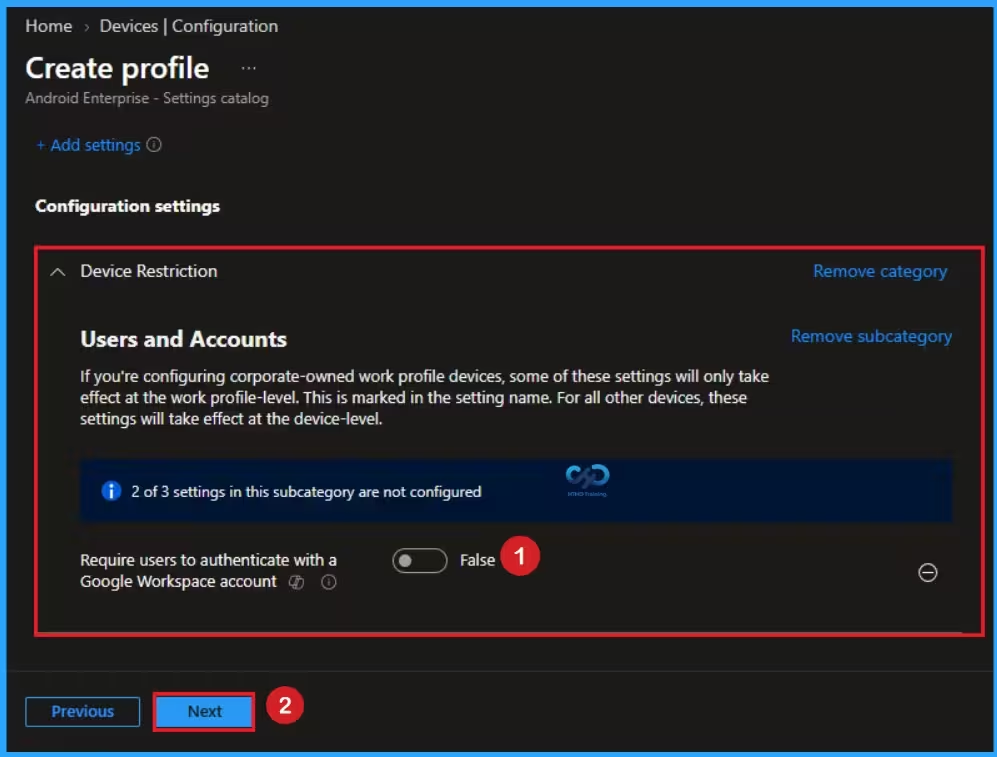
Disable Require Users to Authenticate with a Google Workspace Account
Even if the admin later marks the setting as ‘False’. If ‘False’, Intune doesn’t change or update this setting. Applies to fully managed, and corporate-owned work profile devices. Disable is the default value of this policy. Click on the Next button.
Enable Require Users to Authenticate with a Google Workspace Account
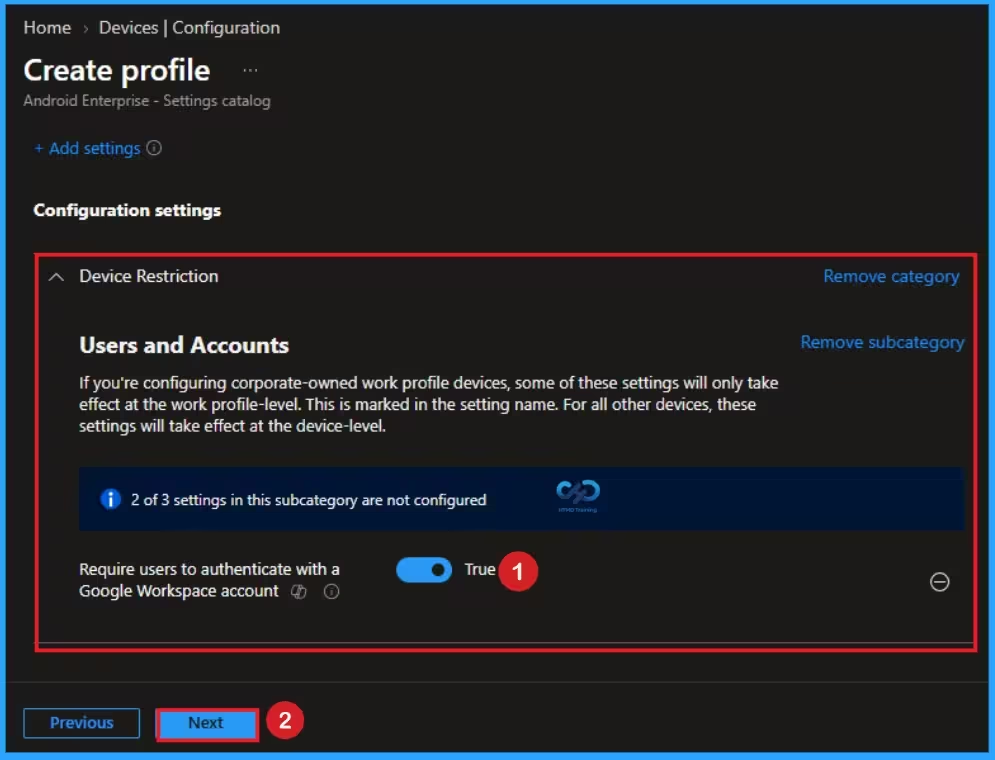
If ‘True’, users must authenticate with a managed Google Workspace account during setup on Android Enterprise devices. After authentication, the Google Workspace account can’t be changed or removed unless the device is unenrolled. Here I would like to Enable the policy. Then click on the Next button to continue.
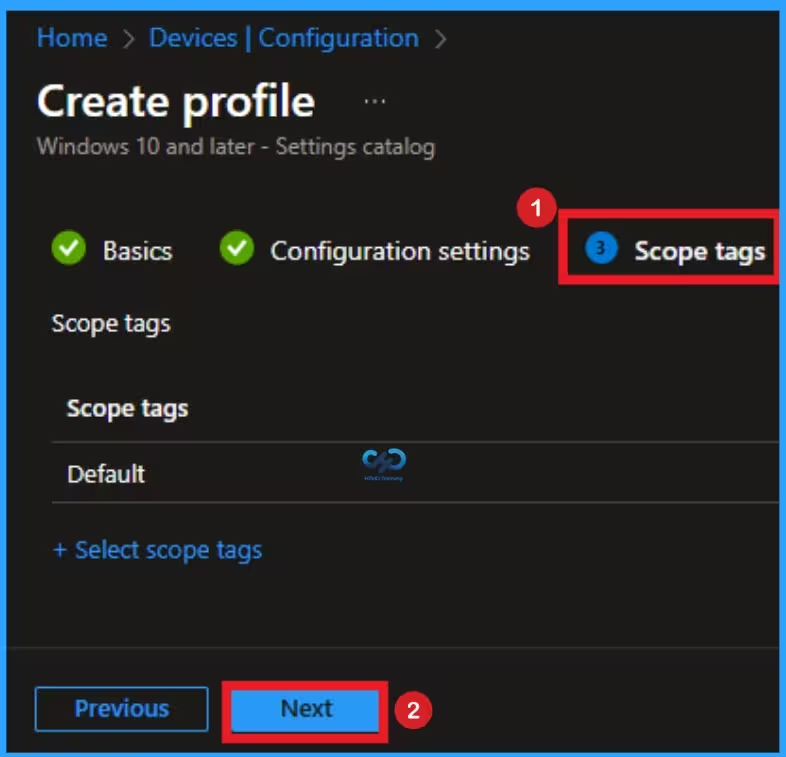
Scope Tags for Require Users to Authenticate with a Google Workspace Account
By using scope tags, you can restrict the visibility of the Require Users to Authenticate with a Google Workspace Account policy. It helps to organise resources as well. Here I would like to skip this section, because it is not mandatory. Click on the Next button.
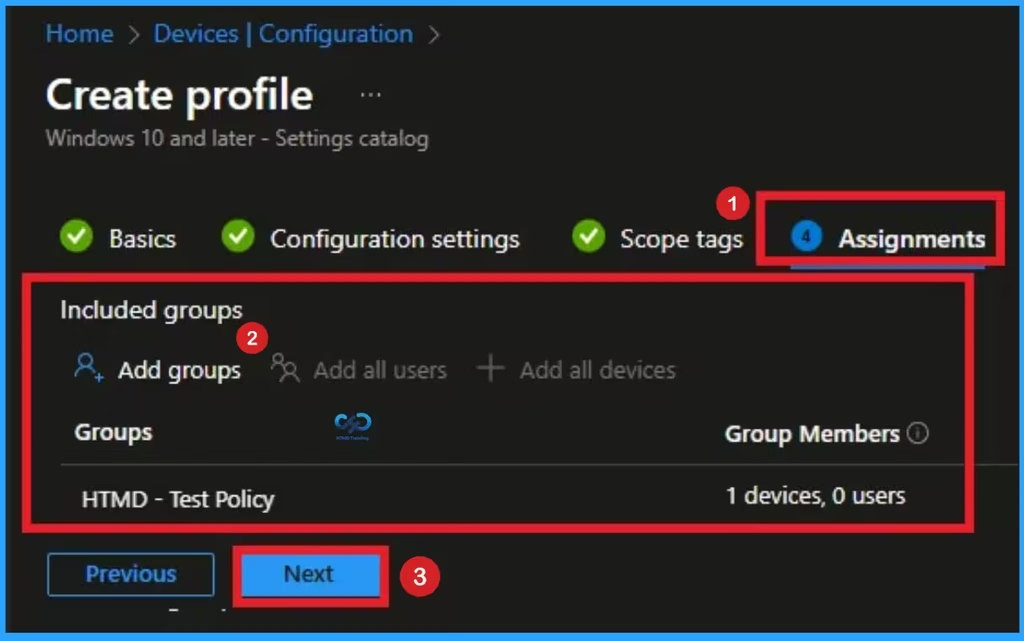
How to Assign Require Users to Authenticate with a Google Workspace Account
To assign the policy to specific groups, you can use the Assignment Tab. Here, I click the +Add groups option under Included groups. I choose a group from the list of groups and click on the Select button. Again, I click on the Select button to continue.
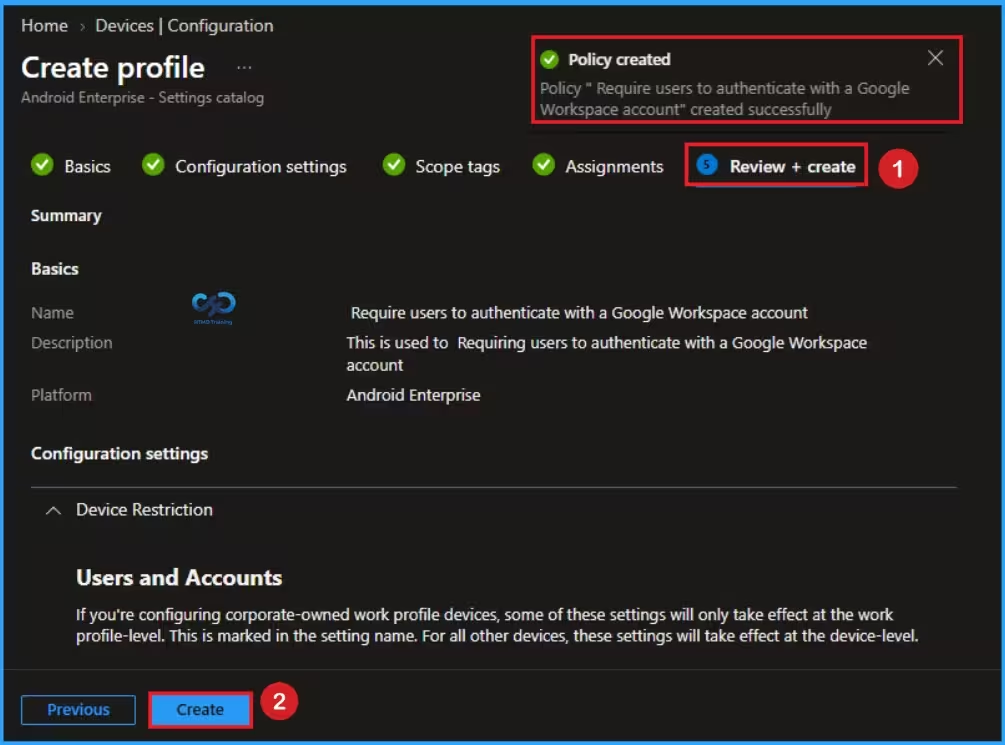
Review Require Users to Authenticate with a Google Workspace Account Policy
To complete the policy creation, you can review all the policy details on the Review + create tab. It helps to avoid mistakes and successfully configure the policy. After verifying all the details, click on the Create Button. After creating the policy, you will get a success message.
Monitoring Status
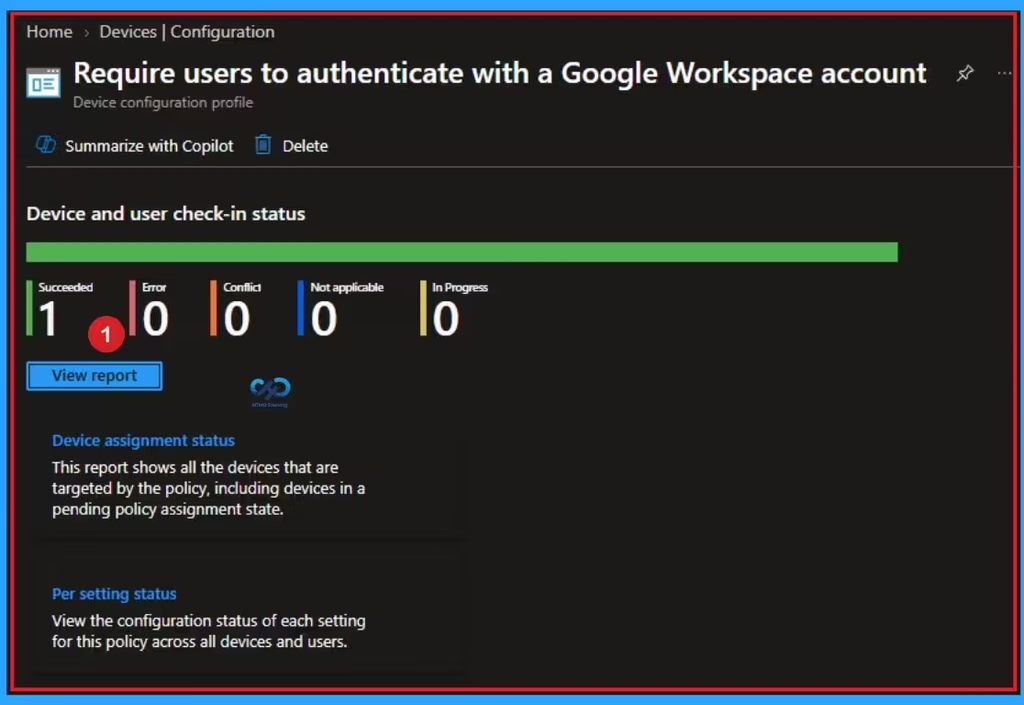
The Monitoring Status page shows whether the policy has succeeded or not. To quickly configure the policy and take advantage of the policy sync, open the Intune Portal on the device in the Company Portal. Go to Devices > Configuration > Search for the Policy. Here, the policy shows as successful.
How to Remove Assigned Group from Require Users to Authenticate with a Google Workspace Account Policy
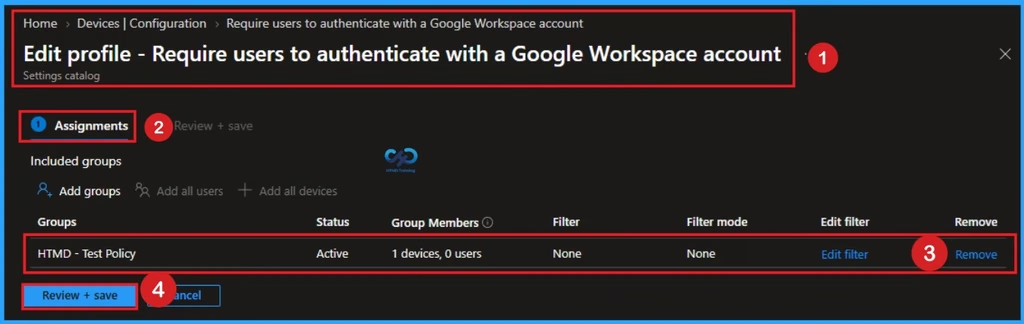
Removing the policy is necessary for some situations. If you want to remove the assigned group from the policy, it is possible from the Intune Portal. To do this, open the Policy on the Intune portal, edit the Assignments tab and remove the Policy.
How to Delete Require Users to Authenticate with a Google Workspace Account Policy
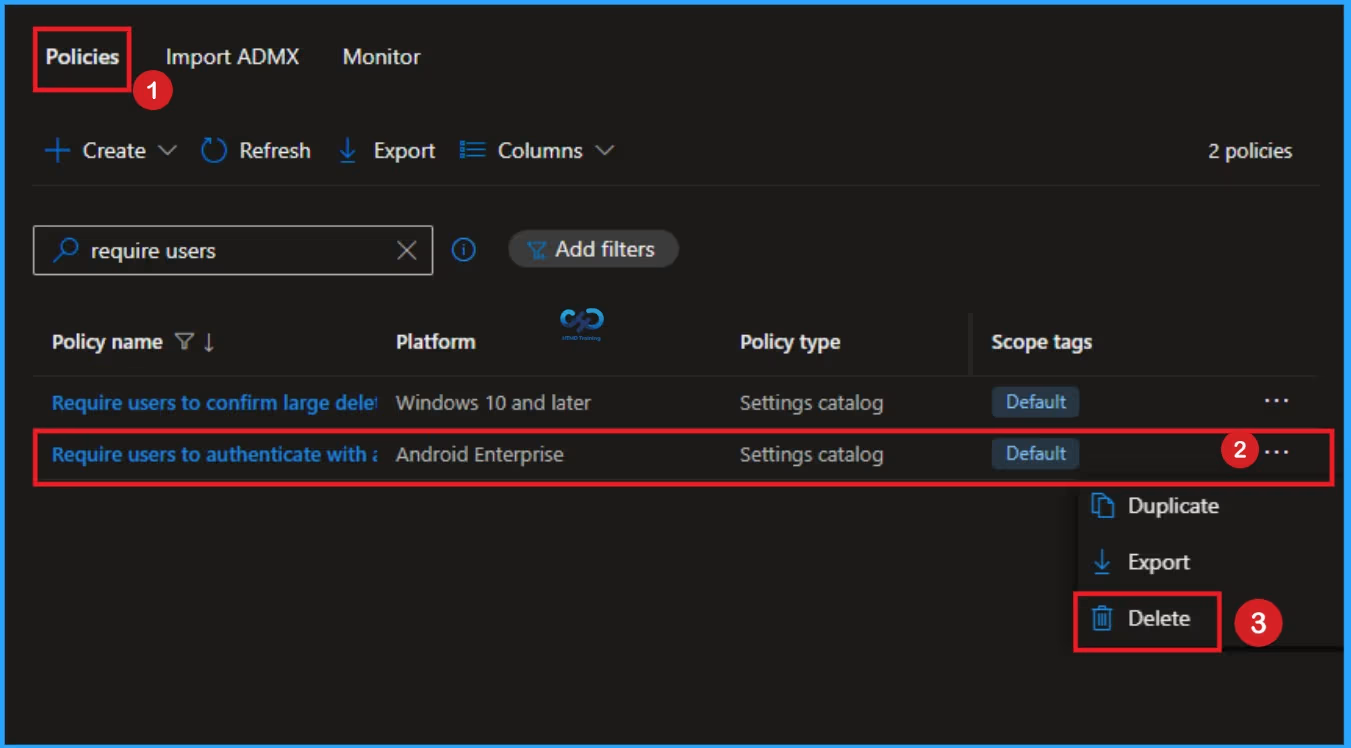
You can easily delete the Policy from the Intune Portal. From the Configuration section, you can delete the policy. It will be completely removed from the client devices.
End User Experience
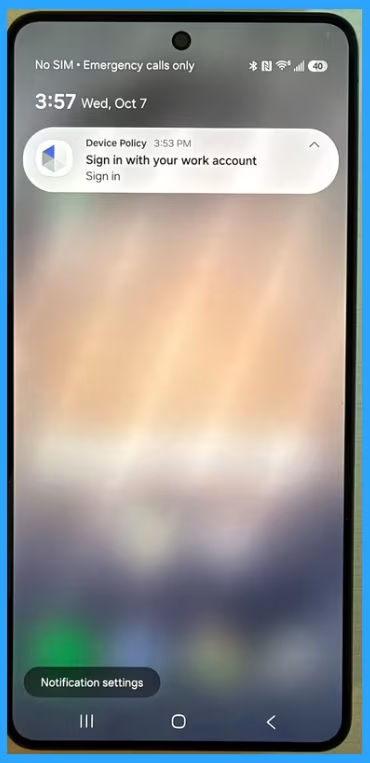
After the policy reaches the device, the user receives a Sign in with your work account prompt on the device. The user clicks on the prompt and adds a managed Google Account from the organization’s enterprise domain and completes authentication.
Until the user completes the prompt and authenticates with the Google Account, the policy setting reports an “Error” state, and the Gmail app, if present on the device, is disabled. This policy’s non-compliance doesn’t change the device’s overall compliance state. Once a Google Account is chosen the user completes authentication, the managed Google Play account is replaced on the device by the chosen Google Account.
Need Further Assistance or Have Technical Questions?
Join the LinkedIn Page and Telegram group to get the latest step-by-step guides and news updates. Join our Meetup Page to participate in User group meetings. Also, join the WhatsApp Community and the WhatsApp channel to get the latest news on Microsoft Technologies. We are there on Reddit as well.
Author
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC. He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.