Key Takeaways
- Microsoft Entra ID Ends SMS First-Factor Sign-In for Workforce Tenants
- Microsoft Entra ID will block phone number + SMS OTP as a primary sign-in method starting February 1, 2027.
- Organisations should find users who rely only on SMS first-factor authentication and check whether they have another registered sign-in method.
- Microsoft recommends alternatives such as Passkeys, Windows Hello for Business, and FIDO2 security keys.
- Pay special attention to shared devices, users without corporate smartphones, and recovery processes that depend on phone numbers.
- Update enrollment instructions, help-desk procedures, break-glass plans, and user communications, and use a staged migration before February 1, 2027.
Microsoft is introducing a security-focused change that will prevent employees from using a registered phone number and SMS one-time passcode (OTP) as their primary sign-in method. If organizations do not prepare in advance, this change could disrupt access to Microsoft 365 and other Microsoft Entra-protected services.
Table of Content
Table of Contents
Microsoft Entra ID Ends SMS First-Factor Sign-In for Workforce Tenants
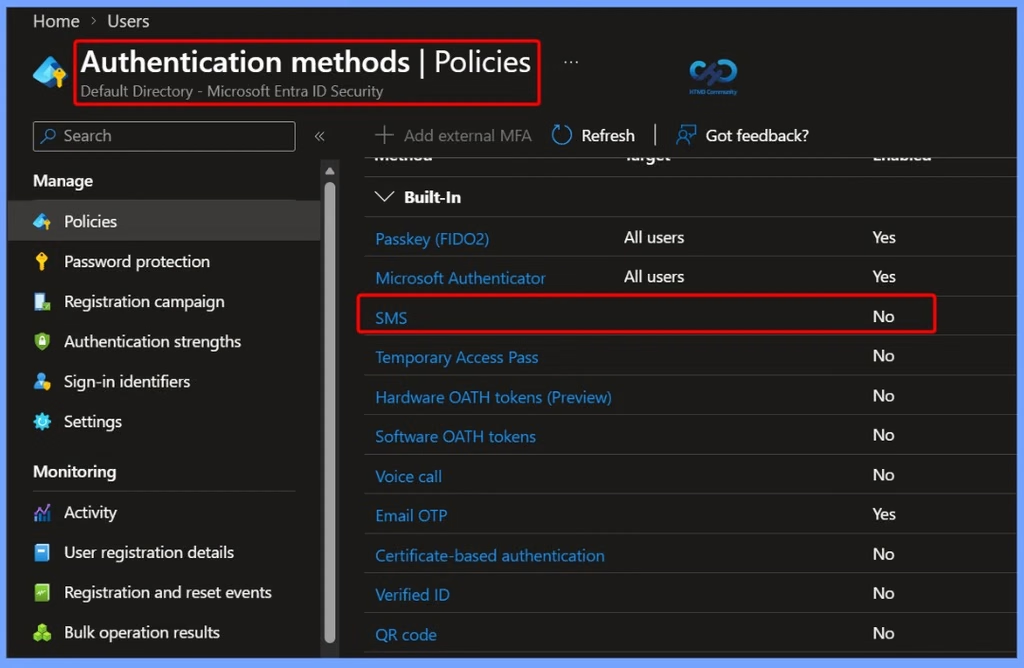
Microsoft Entra ID will stop allowing users to sign in with a phone number and SMS one-time passcode as their primary sign-in method starting February 1, 2027. Organizations need to prepare for this change to avoid sign-in disruptions.
Administrators should identify users who currently depend only on SMS first-factor authentication and check whether they have another registered authentication method. This will help organizations identify accounts that may be affected by the retirement.
- SMS will no longer be supported as a primary sign-in method.
- The change affects users relying on phone number + SMS OTP for first-factor authentication.
- Microsoft refers to this authentication method internally as SignInNoPassword.
- Organisations should identify affected users before the change takes effect.
- Users should register an alternative authentication method to avoid sign-in disruptions.
- What is Microsoft Entra ID?
- Free Entra Training Videos | Start Learning Entra ID Azure AD
- MFA Authentication now Added to WhatsApp
- Walkthrough of Mac Device Passwordless SSO with Entra
Preparing for the End of SMS First-Factor Authentication
Organisations should begin preparing users for the transition away from SMS-based first-factor authentication. Moving users to modern authentication methods, planning for frontline and shared-device scenarios, and updating support and recovery processes can help reduce sign-in disruptions before February 1, 2027.
| Area | Key Details | Action |
|---|---|---|
| Alternative Authentication | Affected users can register Passkeys, Windows Hello for Business, or FIDO2 security keys. | Move users to modern, phishing-resistant authentication methods. |
| Frontline & Shared Devices | QR code authentication can support frontline and shared-device scenarios. Entra represents this as a QR code + PIN combination. | Evaluate QR code authentication for applicable users and devices. |
| Pilot Testing | Authentication options may depend on the organization’s devices, browsers, and Conditional Access authentication strengths. | Pilot each option across the existing device estate before broad deployment. |
| Enrollment & Support | Enrollment instructions and help-desk procedures need to reflect the new authentication methods. | Update documentation and prepare support teams before migration. |
| Break-Glass Planning | Emergency access accounts and recovery processes should not depend on SMS first-factor authentication. | Review and update break-glass and recovery procedures. |
| Staged Migration | A monitored registration campaign can identify issues before enforcement. | Migrate users in stages and monitor registration and application compatibility. |
| Deadline | The operational deadline for the change is February 1, 2027. | Inventory SMS-dependent accounts and remove first-factor SMS dependencies before the deadline. |
Need Further Assistance or Have Technical Questions?
Join the LinkedIn Page and Telegram group to get the latest step-by-step guides and news updates. Join our Meetup Page to participate in User group meetings. Also, join the WhatsApp Community and the Whatsapp channel to get the latest news on Microsoft Technologies. We are there on Reddit as well.
Author
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC. He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.