Key Takeaways
- MS Entra ID Introduce CSP Protections to Block Unauthorized external script injection and Help Prevent XSS Attacks
- The change will begin rolling out worldwide in mid-October 2026 and is expected to complete by late October 2026.
- Browser extensions, monitoring tools, and custom solutions that inject scripts into login.microsoftonline.com may no longer function.
- Organizations that do not use script-injecting tools on Entra ID sign-in pages do not need to make any changes.
- The CSP change applies only to browser-based Entra ID sign-in experiences; MSAL and API-based authentication flows are not affected.
Microsoft Entra ID is strengthening the security of its authentication experience by introducing Content Security Policy (CSP) protections. Starting in mid-October 2026, external or unauthorized scripts injected into login.microsoftonline.com sign-in pages will be blocked, helping protect against threats such as cross-site scripting (XSS).
Table of Content
Table of Contents
MS Entra ID Introduce CSP Protections to Block Unauthorized external script injection and Help Prevent XSS Attacks
Organizations using browser extensions, monitoring tools, or custom solutions that inject scripts into the Entra sign-in page should review and test their authentication workflows before October 19, 2026. If no such tools are used, no action is required. MSAL and API-based authentication flows are not affected.
| Field | Details |
|---|---|
| Message ID | MC1481309 |
| Published | Sep 28, 2026 |
| Service | Microsoft Entra / Microsoft 365 suite |
| Tag | Feature update, User impact, Admin impact |
| Act by | Oct 19, 2026 |
- Microsoft Entra ID Ends SMS First-Factor Sign-In for Workforce Tenants
- What is Microsoft Entra ID?
- Free Entra Training Videos | Start Learning Entra ID Azure AD
- MFA Authentication now Added to WhatsApp
Improving the Security of the Microsoft Entra ID Sign-in Experience
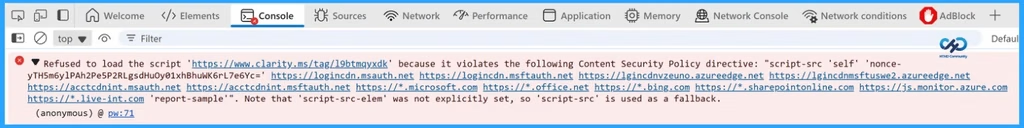
Microsoft is improving the security of the Microsoft Entra ID sign-in experience as part of its Secure Future Initiative. A new Content Security Policy (CSP) will help protect against threats such as cross-site scripting (XSS) by allowing only trusted Microsoft scripts to run and blocking unauthorized or externally injected scripts.
| Rollout Schedule |
|---|
| Starting: Mid-October 2026 Expected completion: Late October 2026 Scope: Worldwide |
Who Is Affected
Organizations using Microsoft Entra ID sign-in pages hosted on login.microsoftonline.com may be affected. This is especially relevant for organizations using browser extensions, monitoring tools, customization tools, or other solutions that inject scripts into the sign-in experience. Microsoft Entra External ID tenants are not affected.
- Platforms and Services
- The change applies to Microsoft Entra ID and web-based authentication experiences using login.microsoftonline.com.
- It also applies to browser-based sign-in experiences across supported browsers.
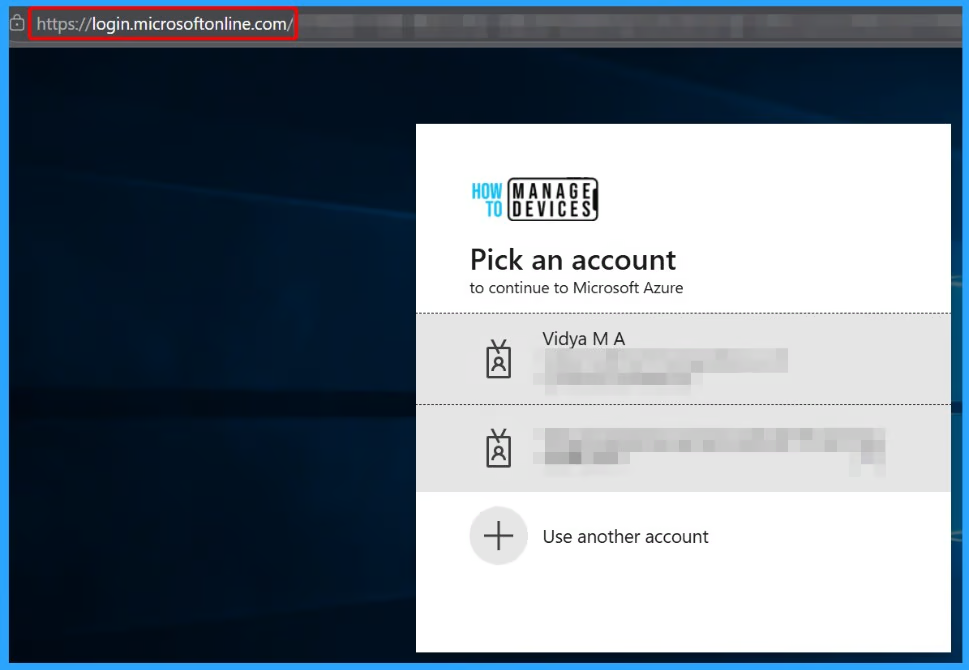
Microsoft Entra ID will add new security protections to its sign-in pages
These protections will allow only trusted Microsoft scripts to run and may affect tools or browser extensions that inject scripts into the sign-in page. The below list helps you to show more details.
- A new Content Security Policy (CSP) header will be added.
- Only scripts from trusted Microsoft CDN domains will be allowed.
- Unauthorized inline scripts will be restricted.
- Browser extensions or tools that inject scripts may stop working.
- Users will still be able to sign in normally even if unsupported tools stop working.
- The change is enabled by default and requires no tenant configuration.
- MSAL and API-based authentication are not affected because the change applies only to browser-based sign-in through login.microsoftonline.com.
| What Should the Admin Do? |
|---|
| If your organization does not use any tools or browser extensions that add scripts to Microsoft Entra ID sign-in pages, no action is required. If your organization does use such tools, administrators should check and test them before the rollout because they may stop working when Microsoft blocks external scripts. If needed, update or replace the affected tools and inform the Help Desk and identity teams about the change. |
Need Further Assistance or Have Technical Questions?
Join the LinkedIn Page and Telegram group to get the latest step-by-step guides and news updates. Join our Meetup Page to participate in User group meetings. Also, join the WhatsApp Community and the Whatsapp channel to get the latest news on Microsoft Technologies. We are there on Reddit as well.
Author
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC. He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.