Key Takeaways
- Complete List of Windows 11 Group Policy Settings for Device and User Management
- Windows 11 continues to receive new and updated Group Policy settings to support the latest features and security requirements.
- Administrators can use Group Policy and ADMX templates to manage Windows 11 devices and control user and device settings.
- Many policies are available for Windows 11 version 21H2 and later, depending on the specific policy and Windows edition.
- Group Policy settings can help organizations manage areas such as security, system behavior, user experience, and device configuration.
- IT administrators should keep their Windows ADMX templates updated so they can access the latest policy settings.
- For organizations using Microsoft Intune, many ADMX-backed policies can also be managed through Intune, providing a modern cloud-based management approach.
Microsoft continues to update Windows 11 Group Policy settings to support new features, security improvements, and device management requirements. With the latest Windows 11 25H2 Administrative Templates (ADMX/ADML), administrators can access updated policy settings for areas such as security, Windows Update, Microsoft Defender, device management, user experience, and system configuration. Microsoft also provides Administrative Templates for Windows 11 24H2 and 23H2, making it easier for IT administrators to manage different Windows 11 environments.
Table of content
Table of Contents
Complete List of Windows 11 Group Policy Settings for Device and User Management
How to get Windows 11? Microsoft released different editions of Windows 11 ISOs (Consumer and Business). You can download the Windows 11 ISO directly from the Microsoft Software Download website. You don’t have to log in to download the ISO. To get the details about the latest version of the Windows 11 ISO download (production version), the latest Windows 11 ISO is ready to download the production version.
The devices should meet the Windows 11 minimum requirements for Windows 11 upgrade. Using the PC Health Check app, you can check for compatibility to see if your current PC meets the minimum system requirements to run Windows 11. You have to download the Windows 11 PC Health Check App from the Microsoft site. Here let’s explore the Windows 11 Group Policy; if you are looking to get Group Policy settings added in Windows 10, version 21H1, and earlier.
The best way to find the list of policies from the blog post below –
- What’s New Group Policy Settings Available in Different Versions of Windows 10.
- List of New Group Policy Settings in Windows 10 21H1.
- Download – ADMX Templates for Windows 11 October 2021 Update [21H2].
- Download Windows 10 Administrative Templates for All Versions
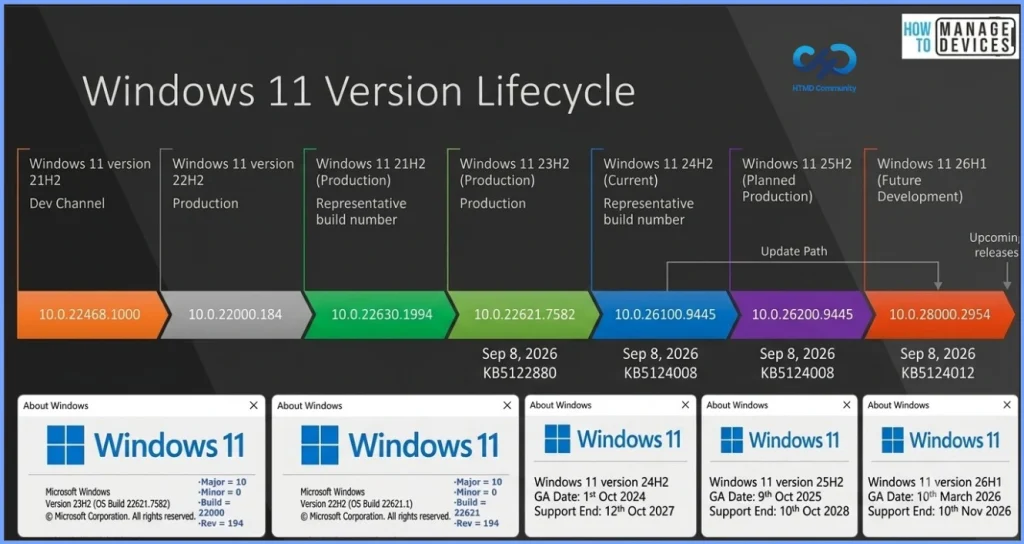
List of Windows 11 Group Policy Settings
The following Windows 11 Group Policy Settings lists for computer and user configurations are included in the Administrative template files (.admx and .adml) delivered with Windows 11. We will try to keep the list up to date with the latest Windows 11 Group Policy.
| Location | Policy Path | Policy Setting Name |
| Machine | System > Group Policy | Turn off background refresh of Group Policy |
| Machine | System > Group Policy | Configure user Group Policy loopback processing mode |
| Machine | System > Group Policy | Turn off automatic update of ADM files |
| Machine | System > Group | Always use local ADM files for Group Policy Object Editor |
| Machine | System > Group Policy | Enable Group Policy Caching for Servers |
| Machine | System > Mitigation Options | Process Mitigation Options |
| Machine | System > Group Policy | Phone-PC linking on this device |
| Machine | Network > DNS Client | Configure DNS over HTTPS (DoH) name resolution |
| Machine | System > Kerberos | Allow retrieving the cloud Kerberos ticket during logon |
| Machine | System > Device Installation > Device Installation Restrictions | Apply layered order of evaluation for Allow and Prevent device installation policies |
| Machine | Windows Components > Windows Hello for Business | Use cloud trust for on-premises authentication |
| Machine | Windows Components > Human Presence | Force Instant Lock |
| Machine | Windows Components > Human Presence | Force Instant Wake |
| Machine | Windows Components > Human Presence | Lock Timeout |
| Machine | Windows Components > Windows Sandbox | Allow audio input in Windows Sandbox |
| Machine | Windows Components > Windows Sandbox | Allow clipboard sharing with Windows Sandbox |
| Machine | Windows Components > Windows Sandbox | Allow networking in Windows Sandbox |
| Machine | Windows Components > Windows Sandbox | Allow printer sharing with Windows Sandbox |
| Machine | Windows Components > Windows Sandbox | Allow vGPU sharing for Windows Sandbox |
| Machine | Windows Components > Windows Sandbox | Allow video input in Windows Sandbox |
| Machine | Windows Components > Remote Desktop Services > Remote Desktop Session Host > Device and Resource Redirection | Allow UI Automation redirection |
| Machine | Windows Components > Remote Desktop Services > Remote Desktop Session Host > Device and Resource | Redirection Do not allow location redirection |
| Machine | Windows Components > Widgets | Allow widgets |
| Machine | Windows Components > Microsoft Defender Antivirus > Real-time Protection | Turn on script scanning |
| Machine | Windows Components > Microsoft Defender Antivirus > Device Control | Define device control policy groups |
| Machine | Windows Components > Microsoft Defender Antivirus > Device Control | Define device control policy rules |
| Machine | Windows Components > Microsoft Defender Antivirus > Security Intelligence Updates | Allow Microsoft Defender Antivirus to update over a metered connection |
| Machine | Windows Components > Microsoft Defender Antivirus | Configure scheduled task times randomization window |
| Machine | Windows Components > App Package Deployment | Archive infrequently used apps |
| Machine | Windows Components > App Package Deployment | Do not allow sideloaded apps to auto-update in the background |
| Machine | Windows Components > App Privacy | Let Windows apps take screenshots of various windows or displays |
| Machine | Windows Components > Cloud Content | Turn off cloud consumer account state content |
| Machine | Windows Components > Data Collection and Preview Builds | Limit Diagnostic Log Collection |
| Machine | Windows Components > Data Collection and Preview Builds | Limit Dump Collection |
| Machine | Windows Components > Windows Update > Manage updates offered from Windows Server Update Service | Specify source service for specific classes of Windows Updates |
| User | System > Group Policy | Turn off automatic update of ADM files |
| User Start Menu and Taskbar | Start Menu and Taskbar | Show or hide “Most used” list from Start menu |
| User | Windows Components > Cloud Content | Turn off Spotlight collection on Desktop |
| User | Windows Components > IME | Configure Korean IME version |
| Machine | Control Panel\Personalization | Prevent lock screen background motion |
| Machine | Control Panel\Regional and Language Options | Restrict Language Pack and Language Feature Installation |
| Machine | MS Security Guide | Limits print driver installation to Administrators. |
| Machine | Network\DNS Client | Configure DNS over HTTPS (DoH) name resolution |
| Machine | Printers | Enable Device Control Printing Restrictions |
| Machine | Printers | List of Approved USB-connected print devices |
| Machine | Start Menu and Taskbar | Show or hide “Most used” list from Start menu |
| Machine | Start Menu and Taskbar\Notifications | Enables group policy for the WNS FQDN |
| Machine | System\Device Installation\Device Installation Restrictions | Apply layered order of evaluation for Allow and Prevent device installation policies across all device match criteria |
| Machine | System\Filesystem\NTFS | Enable NTFS non-paged pool usage |
| Machine | System\Filesystem\NTFS | NTFS default tier |
| Machine | System\Filesystem\NTFS | NTFS parallel flush threshold |
| Machine | System\Filesystem\NTFS | NTFS parallel flush worker threads |
| Machine | System\Kerberos | Allow retrieving the cloud kerberos ticket during the logon |
| Machine | System\Net Logon\DC Locator DNS Records | Use lowercase DNS host names when registering domain controller SRV records |
| Machine | System\Security Account Manager | Configure validation of ROCA-vulnerable WHfB keys during authentication |
| Machine | Windows Components\App Package Deployment | Archive infrequently used apps |
| Machine | Windows Components\App Package Deployment | Not allow sideloaded apps to auto-update in the background |
| Machine | Windows Components\App Package Deployment | Not allow sideloaded apps to auto-update in the background on a metered network |
| Machine | Windows Components\App Privacy | Let Windows apps take screenshots of various windows or displays |
| Machine | Windows Components\App Privacy | Let Windows apps turn off the screenshot border |
| Machine | Windows Components\Chat | Configures the Chat icon on the taskbar |
| Machine | Windows Components\Cloud Content | Turn off cloud consumer account state content |
| Machine | Windows Components\Data Collection and Preview Builds | Disable OneSettings Downloads |
| Machine | Windows Components\Data Collection and Preview Builds | Enable OneSettings Auditing |
| Machine | Windows Components\Data Collection and Preview Builds | Limit Diagnostic Log Collection |
| Machine | Windows Components\Data Collection and Preview Builds | Limit Dump Collection |
| Machine | Windows Components\Human Presence | Force Instant Lock |
| Machine | Windows Components\Human Presence | Force Instant Wake |
| Machine | Windows Components\Human Presence | Lock Timeout |
| Machine | Windows Components\Internet Explorer | Replace JScript by loading JScript9Legacy in place of JScript via MSHTML/WebOC. |
| Machine | Windows Components\Microsoft Defender Antivirus | Configure scheduled task times randomization window |
| Machine | Windows Components\Microsoft Defender Antivirus | Define the directory path to copy support log files |
| Machine | Windows Components\Microsoft Defender Antivirus\Device Control | Define device control policy groups |
| Machine | Windows Components\Microsoft Defender Antivirus\Device Control | Define device control policy rules |
| Machine | Windows Components\Microsoft Defender Antivirus\Exclusions | Ip Address Exclusions |
| Machine | Windows Components\Microsoft Defender Antivirus\Microsoft Defender Exploit Guard\Network Protection | This settings controls whether Network Protection is allowed to be configured into block or audit mode on Windows Server. |
| Machine | Windows Components\Microsoft Defender Antivirus\Network Inspection System | This setting controls datagram processing for network protection. |
| Machine | Windows Components\Microsoft Defender Antivirus\Real-time Protection | Turn on script scanning |
| Machine | Windows Components\Microsoft Defender Antivirus\Security Intelligence Updates | Allows Microsoft Defender Antivirus to update and communicate over a metered connection. |
| Machine | Windows Components\Remote Desktop Services\Remote Desktop Session Host\Device and Resource Redirection | Allow UI Automation redirection |
| Machine | Windows Components\Remote Desktop Services\Remote Desktop Session Host\Device and Resource Redirection | Do not allow location redirection |
| Machine | Windows Components\Tenant Restrictions | Cloud Policy Details |
| Machine | Windows Components\Widgets | Allow widgets |
| Machine | Windows Components\Windows Hello for Business | Use cloud trust for on-premises authentication |
| Machine | Windows Components\Windows Sandbox | Allow audio input in Windows Sandbox |
| Machine | Windows Components\Windows Sandbox | Allow clipboard sharing with Windows Sandbox |
| Machine | Windows Components\Windows Sandbox | Allow networking in Windows Sandbox |
| Machine | Windows Components\Windows Sandbox | Allow printer sharing with Windows Sandbox |
| Machine | Windows Components\Windows Sandbox | Allow vGPU sharing for Windows Sandbox |
| Machine | Windows Components\Windows Sandbox | Allow video input in Windows Sandbox |
| Machine | Windows Components\Windows Update\Manage updates offered from Windows Server Update Service | Specify source service for specific classes of Windows Updates |
| User | AutoSubscription | Enable auto-subscription |
| User | Control Panel\Printers | Enable Device Control Printing Restrictions |
| User | Control Panel\Printers | List of Approved USB-connected print devices |
| User | Control Panel\Regional and Language Options | Restrict Language Pack and Language Feature Installation |
| User | Start Menu and Taskbar | Show or hide “Most used” list from Start menu |
| User | Windows Components\Cloud Content | Turn off Spotlight collection on Desktop |
| User | Windows Components\IME | Configure Korean IME version |
| User | Windows Components\Internet Explorer | Replace JScript by loading JScript9Legacy in place of JScript via MSHTML/WebOC. |
Need Further Assistance or Have Technical Questions?
Join the LinkedIn Page and Telegram group to get the latest step-by-step guides and news updates. Join our Meetup Page to participate in User group meetings. Also, join the WhatsApp Community and the Whatsapp channel to get the latest news on Microsoft Technologies. We are there on Reddit as well.
Author
Jitesh, Microsoft MVP, has over six years of working experience in the IT Industry. He writes and shares his experiences related to Microsoft device management technologies and IT Infrastructure management. His primary focus is Windows 10/11 Deployment solution with Configuration Manager, Microsoft Deployment Toolkit (MDT), and Microsoft Intune.
“Configure the Chat icon” appears to not work when set to “Enabled: Hide” as of OS build 22000.258.
Have you tried this policy MDM https://www.anoopcnair.com/remove-microsoft-teams-chat-icon-using-intune/
No, we use the Pro OS version. If I’m reading this right, that setting doesn’t apply to Pro – https://docs.microsoft.com/en-us/windows/client-management/mdm/policy-csp-Experience?WT.mc_id=Portal-fx#experience-configurechaticonvisibilityonthetaskbar
Maybe the same OS version limitation applies to the Group Policy.
Good catch. Indeed removal of the Teams chat icon is not supported for Windows 11 pro version. This is a bit weird
How do i activate this last setting that is off Windows Defender Application Contol ?!?!?!?!?!
OS Name Microsoft Windows 11 Pro
Version 10.0.22581 Build 22581
Other OS Description Not Available
OS Manufacturer Microsoft Corporation
System Name ERIC
System Manufacturer System manufacturer
System Model System Product Name
System Type x64-based PC
System SKU SKU
Processor AMD Ryzen 9 5950X 16-Core Processor, 4001 Mhz, 16 Core(s), 32 Logical Processor(s)
BIOS Version/Date American Megatrends Inc. 4204, 2/24/2022
SMBIOS Version 3.3
Embedded Controller Version 255.255
BIOS Mode UEFI
BaseBoard Manufacturer ASUSTeK COMPUTER INC.
BaseBoard Product ROG STRIX X570-E GAMING
BaseBoard Version Rev X.0x
Platform Role Desktop
Secure Boot State On
PCR7 Configuration Bound
Windows Directory C:\WINDOWS
System Directory C:\WINDOWS\system32
Boot Device \Device\HarddiskVolume1
Locale United States
Hardware Abstraction Layer Version = “10.0.22581.1”
User Name Eric\Administrator
Time Zone Mountain Daylight Time
Installed Physical Memory (RAM) 32.0 GB
Total Physical Memory 31.9 GB
Available Physical Memory 24.1 GB
Total Virtual Memory 36.9 GB
Available Virtual Memory 26.3 GB
Page File Space 5.00 GB
Page File C:\pagefile.sys
Kernel DMA Protection On
Virtualization-based security Running
Virtualization-based security Required Security Properties Base Virtualization Support, Secure Boot
Virtualization-based security Available Security Properties Base Virtualization Support, Secure Boot, DMA Protection, Secure Memory Overwrite, UEFI Code Readonly, Mode Based Execution Control
Virtualization-based security Services Configured Credential Guard, Hypervisor enforced Code Integrity, Secure Launch
Virtualization-based security Services Running Credential Guard, Hypervisor enforced Code Integrity, Hardware-enforced Stack Protection (Kernel-mode)
Windows Defender Application Control policy Enforced
Windows Defender Application Control user mode policy Off <<——————– This one !!
Device Encryption Support Reasons for failed automatic device encryption: Un-allowed DMA capable bus/device(s) detected
A hypervisor has been detected. Features required for Hyper-V will not be displayed.
Hi Anoop,
Is there any setting to manage date formats?
I want to use below format for short-date.
22-Aug-2022