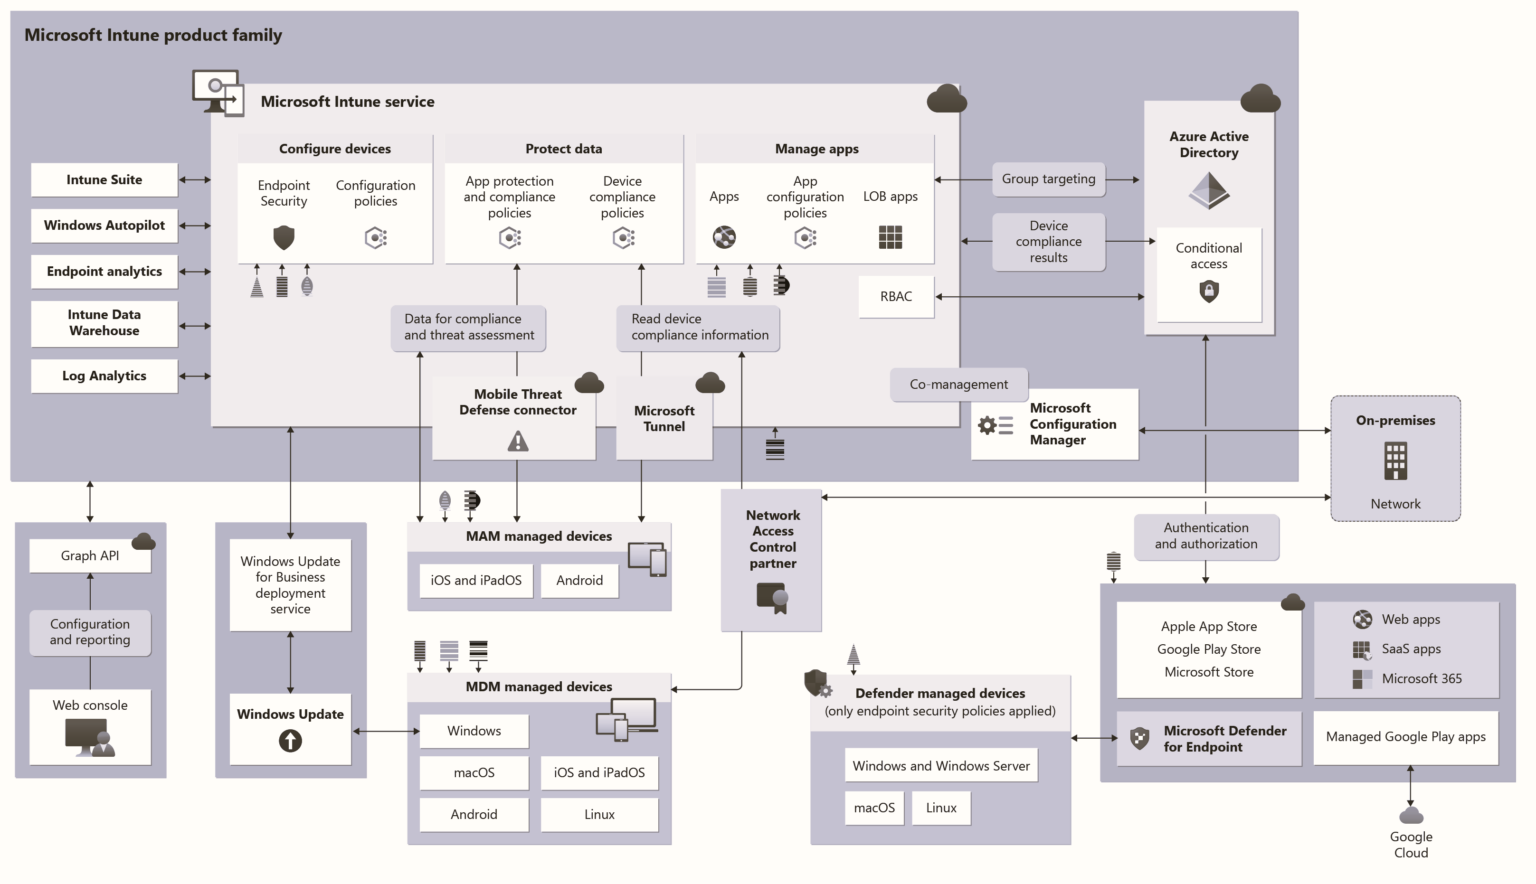
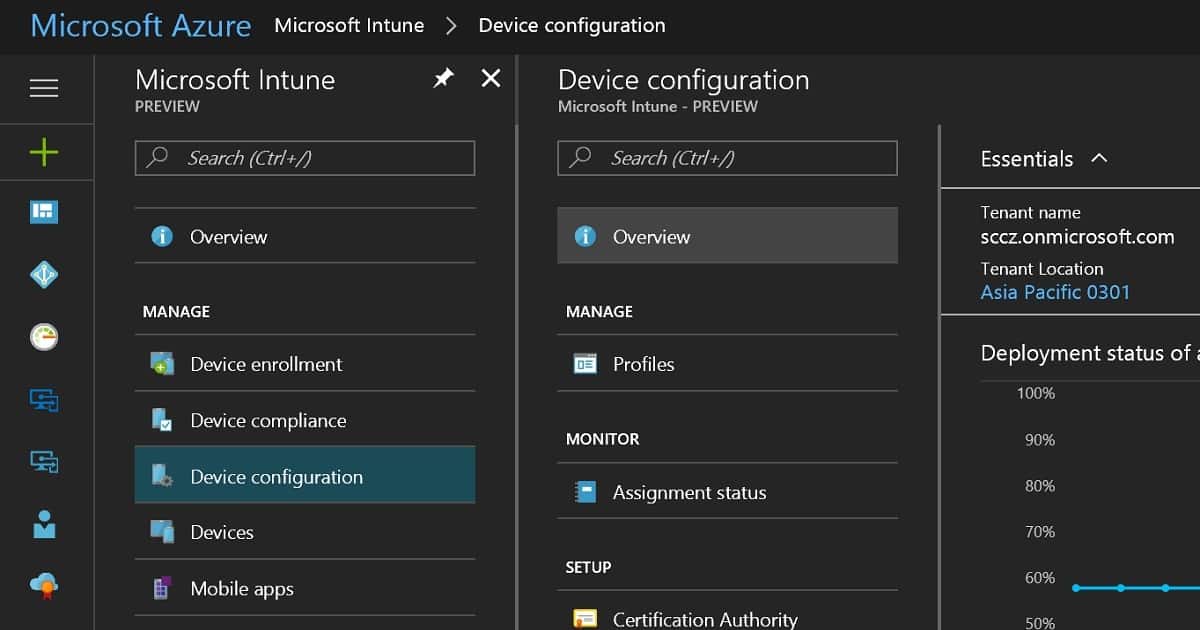
Microsoft Intune is the SaaS solution provided by Microsoft. Microsoft Intune is a cloud-based desktop and mobile device management tool. This supports Mac OS, iOS, Android, and Windows 10. This cloud solution is used as a modern management tool.
This MDM solution can be integrated with SCCM, Azure AD, and Active Directory. This place gives you a great opportunity Learn Microsoft Intune and become an expert with Intune.
This solution can be used to deploy UWP applications, Security policies, Configuration policies, WiFi profiles, PKI certificates, and so on.
This solution is future-proof When you take a look at the Desktop (43.29%) Vs. Mobile (52.29%) Vs. Tablet (4.42%) Market Share Worldwide for the last year, you could see that mobile devices are leaders. So, Mobile Device Management is very critical, and this is a new world of opportunities for IT Pros like us. From my perspective, learning this solution is very important for SCCM admins.
Intune is an enterprise mobility management (EMM) solution from Microsoft. The EMM provider helps to manage mobile devices, network settings, and other mobile services and settings. This solution is nothing but a combination of Device, Application, Information Protection, Endpoint Protection (antivirus software), and Security/Configuration policy management solution (SaaS) facilitated by Microsoft in the Cloud.
Additionally, this solution has a feature called compliance policy, which can be integrated with the Azure AD “Conditional Access” policy to restrict access to company resources.
Let’s discuss Windows 10 Quality Feature Update Policies for Intune Step-by-Step Guide. Microsoft released Windows 10 1709, the fall Creators update. Devices in the current branch (Semi-Annual Targeted) should be updated in Settings—Update and Security—Windows Update.
Intune Windows 10 Quality Update Policies. Microsoft Intune manages this Windows 10 device. This post will see “Windows 10 1709 Fall Creators Update Upgrade with Intune Update Rings.”
Many methods exist to upgrade the Windows 10 version to the latest version, 1709. You can upgrade to Windows 10 with an ISO file available in Visual Studio Subscriptions (previously known as MSDN) or VLSC (Volume Licensing Service Center).
If Microsoft Intune manages your devices, a software update policy ring will manage Windows 10 feature updates.
Table of Contents
Windows 10 Quality Feature Update Policies for Intune Step by Step Guide
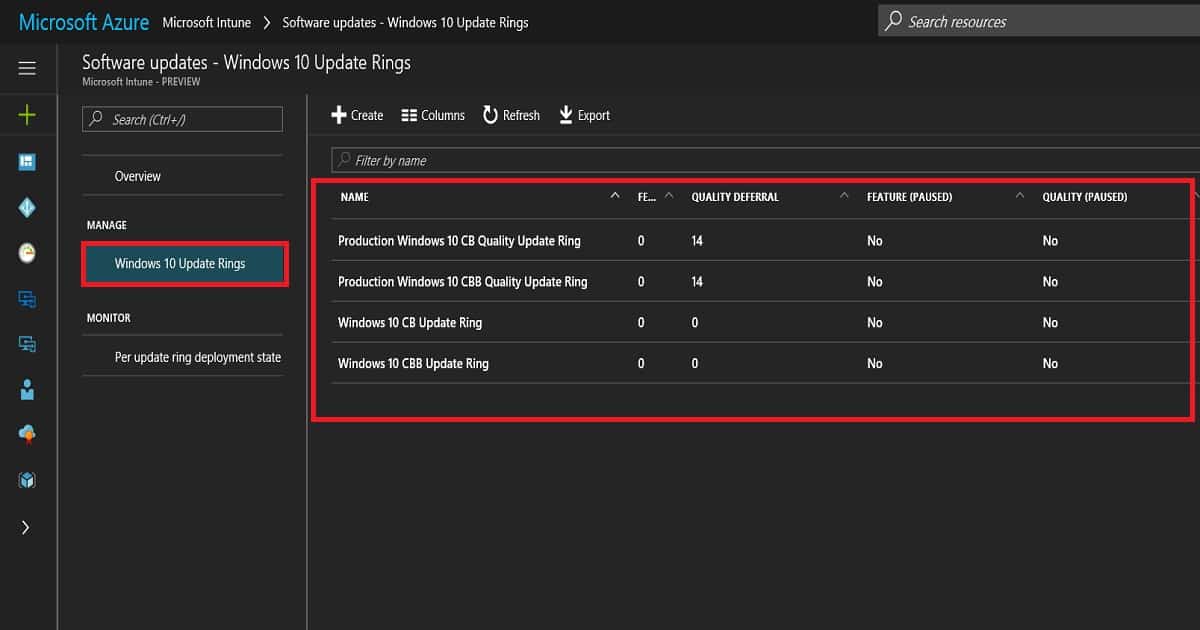
Navigate via Microsoft Azure—Microsoft Intune—Software Updates to “Windows 10 Update Rings.” Here, you can create Windows 10 Semi-Annual Targeted and Semi-Annual update rings.
These two update rings in Intune can control your organization’s Windows 10 upgrade behavior. Intune Windows 10 Quality Update Policies.
Windows 10 Semi-Annual Targeted Update Ring – All the devices in the Current Branch.
Windows 10 Semi-Annual Update Ring – All the devices in the Current Branch for Business
FIX CBB Ring Devices are Getting CB Updates Intune Windows 10 Update Rings
Windows 10 1709 Fall Creators Update Upgrade with Intune Update Rings
Windows 10 Quality Feature Update Policies for Intune Step by Step Guide – Fig.1
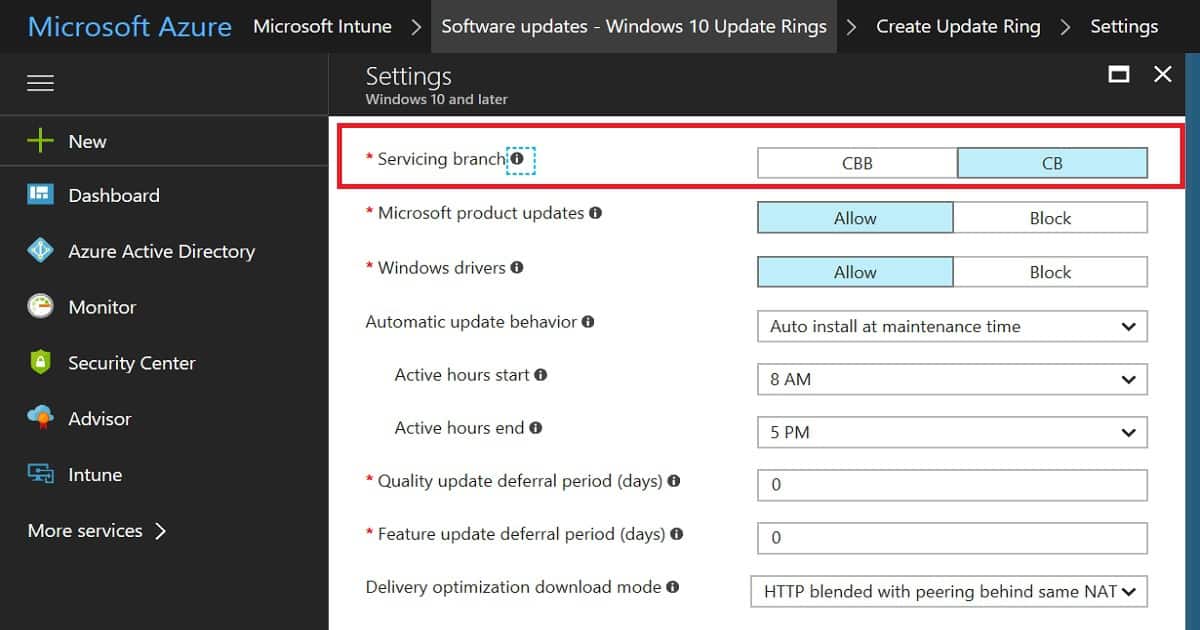
Navigate via the Intune console to access Windows 10 Update Rings – Create Update Ring – Settings. We must select the “Servicing Branch” options according to your requirements. Feature update deferral period (days) is another set we want to set up as part of the Create Update Ring policy.
For example:- If we set Service Branch = CB and Feature update deferral period (days) = 0 days, then the device will get the Windows 10 1709 updates on the 0 days of the release.
As I mentioned in the above paragraph, there are two types of Servicing Branches for Windows 10: Semi-Annual Targeted and Semi-Annual.
Select the CB servicing branch (Semi-Annual Targeted) to set the devices for the first wave of deployment of Windows 10 feature upgrades. The latest Windows 10 1709 Fall Creators update is released only for the Semi-Annual Targeted branch.
How Do Windows 10 Update Rings Work?
Windows 10 update rings work flawlessly under the hood. I have not uploaded Windows 10 1709 ISO or files to Intune to deliver the updates to the devices. Intune helps to set up 2 MDM policies in Windows 10 1607 or later devices.
So, Devices, are you getting the Windows 10 feature update binaries from any other Microsoft cloud service? Windows 10 devices are getting these feature update content/binaries from Windows Update for Business (WUfB).
Another essential feature of Windows 10 is Delivery Optimization. Delivery optimization helps to find the binaries from the peer devices. These peer devices could be either from the same network or the internet.
Windows 10 Update Ring MDM Policies?
The following are the two MDM policies that Intune sets on Windows 10 devices. Intune Windows 10 Quality Update Policies.
CB/CBB Options:- MDM for version 1607 and above: MDM for version 1607 and above: ../Vendor/MSFT/Policy/Config/Update/BranchReadinessLevel \Microsoft\PolicyManager\default\Update\BranchReadinessLevel
Deferral Period Days:- MDM for version 1607 and above: ../Vendor/MSFT/Policy/Config/Update/DeferFeatureUpdatesPeriodInDays \Microsoft\PolicyManager\default\Update\DeferFeatureUpdatesPeriodInDays
Windows 10 Upgrade End User Experience
The following video delivers the Windows 10 1709 fall creator update through Windows Update for Business. The next video will give you an end-to-end experience for the Windows 10 1709 fall creators’ upgrade process via Software Update for Business (WUfB).
As you can see in the video, the Windows 10 device is in the CB (Semi-Annual Target) channel and the differed period policy is set to zero days—Intune Windows 10 Quality Update Policies.
Windows 10 Quality Feature Update Policies for Intune Step by Step Guide
We are on WhatsApp now. To get the latest step-by-step guides, news, and updates, Join our Channel. Click here. HTMD WhatsApp.
Author
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC, He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.
Start troubleshooting from the Help and Support page in Microsoft Intune.
Use the Microsoft Azure portal for built-in diagnostics and guided troubleshooting.
Identify whether the issue is user-based or device-based before proceeding.
Check policy assignments, deployment status, and error codes first.
Verify device check-in and manual sync status if policies are not applying.
Follow a structured troubleshooting approach to quickly resolve the root cause of issues in Microsoft Intune. Start with diagnostics, verify assignments and deployment status, and review error details before moving to advanced analysis. Getting guidance available through the Microsoft Azure portal helps ensure consistent and effective troubleshooting.
Table of Content
Table of Contents
Latest Intune Troubleshooting Strategies for App and Policy Deployment
In this video, you will learn the latest troubleshooting strategies in Microsoft Intune to simplify app and policy deployment issues. The session covers practical techniques to identify deployment failures, analyze logs, re view device and user status, and use built-in reporting tools effectively.
How to Start Troubleshooting Intune Issues and Fix them with Easy Steps – Video 1
How to Start Troubleshooting Intune Policy Deployment Issues
Let’s discuss how to start troubleshooting Intune Policy Deployment Issues. In this video, you will learn the step-by-step approach to start troubleshooting policy deployment issues in Microsoft Intune.
How to Start Troubleshooting Intune Issues and Fix them with Easy Steps – Video 2
Checking Tenant Status and Service Health in Microsoft Intune
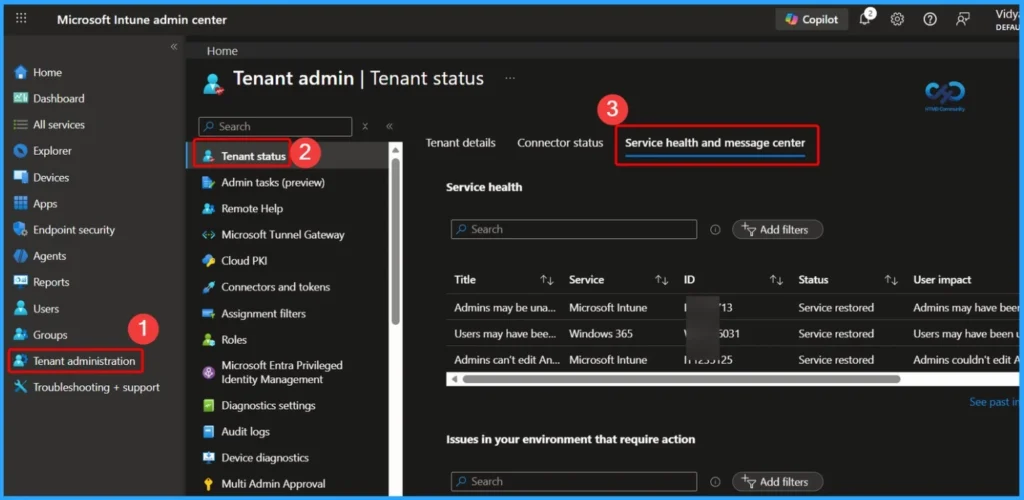
Go to Tenant administration > Tenant status > Service health and message center to review current service incidents, advisories, and recently resolved issues. This section provides visibility into service disruptions, user impact, and restoration updates related to Intune and connected services. Regularly checking the Service health and message center helps IT admins quickly determine whether an issue is tenant-related or service-related before starting detailed troubleshooting steps.
Go to Microsoft Intune admin center > Tenant Administration > Tenant Status > Service health and message center.
How to Start Troubleshooting Intune Issues and Fix them with Easy Steps – Fig.1
User Level Troubleshooting in Microsoft Intune Admin Center
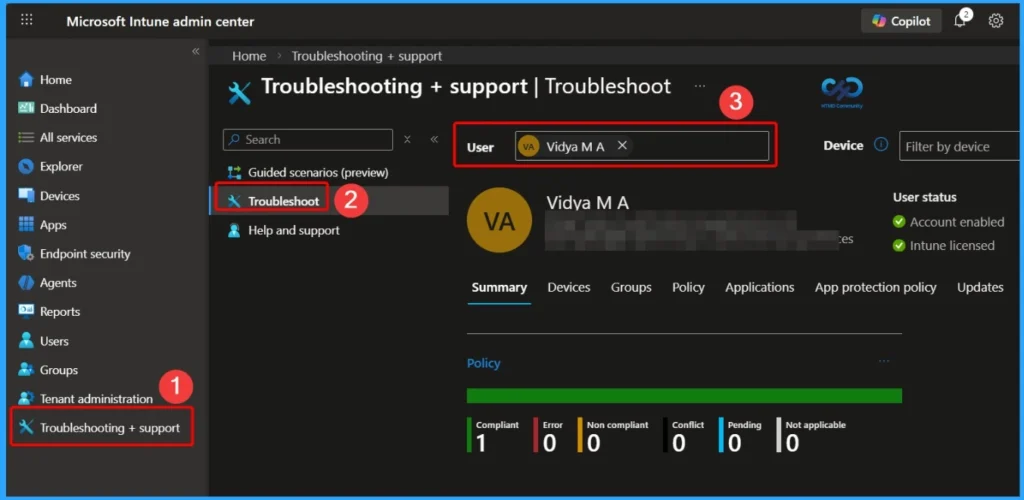
In the Microsoft Intune admin center, you can perform detailed user level troubleshooting from the Troubleshooting + support section. Go to Troubleshooting + support > Troubleshoot, then search and select the affected user. This view provides a comprehensive summary of the user’s device compliance status, assigned policies, applications, group memberships, and app protection policies.
How to Start Troubleshooting Intune Issues and Fix them with Easy Steps – Fig.2
Using Help and Support in Microsoft Intune for Troubleshooting
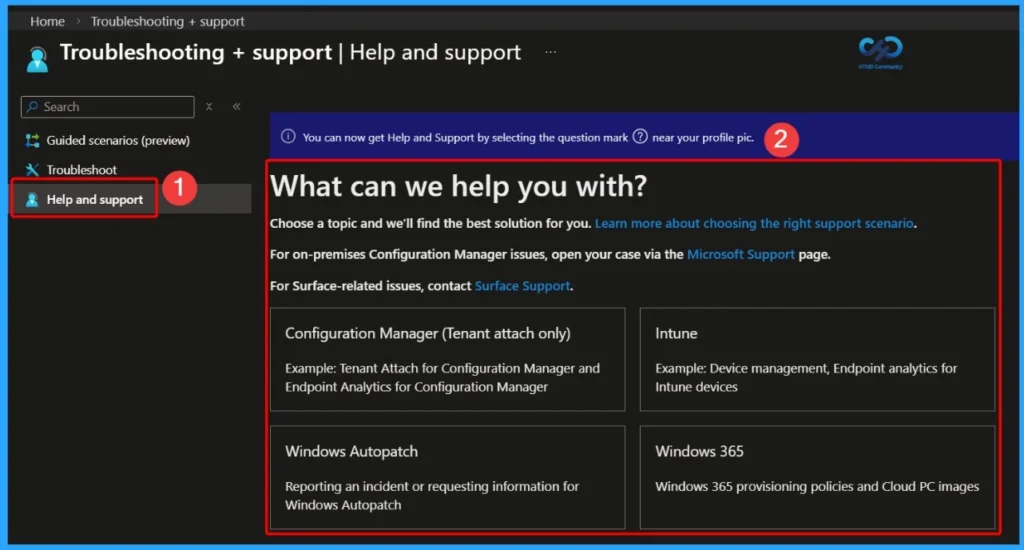
In the Microsoft Intune admin center, the Help and support section under Troubleshooting + support is the recommended starting point when you face any issue. From this page, you can select the relevant support scenario such as Intune, SCCM, Windows Autopatch, or Windows 365. The portal guides you to the most appropriate diagnostics, documentation, or support options based on your selection.
How to Start Troubleshooting Intune Issues and Fix them with Easy Steps – Fig.3
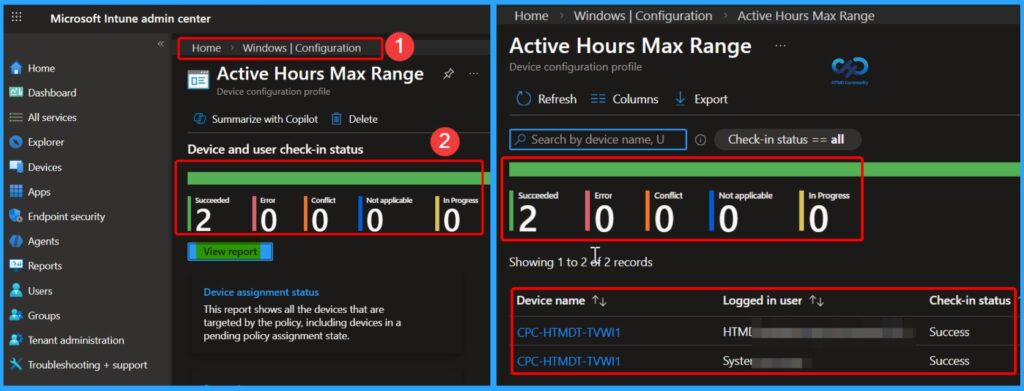
You can easily check configuration profile issues in Microsoft Intune. Go to the Intune admin center and navigate to Devices > Configuration profiles. Select the specific profile you want to review, then open the Per-settings status or Device status tab. This view shows whether the policy deployment status is Succeeded, Error, Conflict, or Not applicable for each device or user.
How to Start Troubleshooting Intune Issues and Fix them with Easy Steps – Fig.4
Monitoring Service Health in Microsoft 365 Admin Center
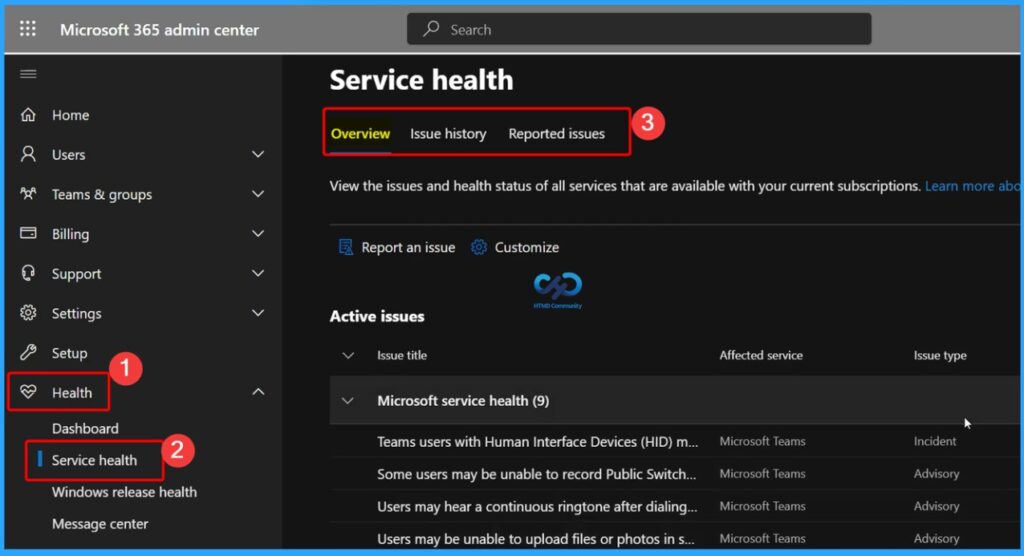
Checking the Service health dashboard helps IT admins quickly determine whether an issue is caused by a Microsoft service outage or an internal configuration problem, allowing faster and more accurate troubleshooting decisions.
In the Microsoft 365 admin center, you can monitor overall service status by navigating to Health > Service health.
How to Start Troubleshooting Intune Issues and Fix them with Easy Steps – Fig.5
Reviewing User Details in the Intune Troubleshooting Tab
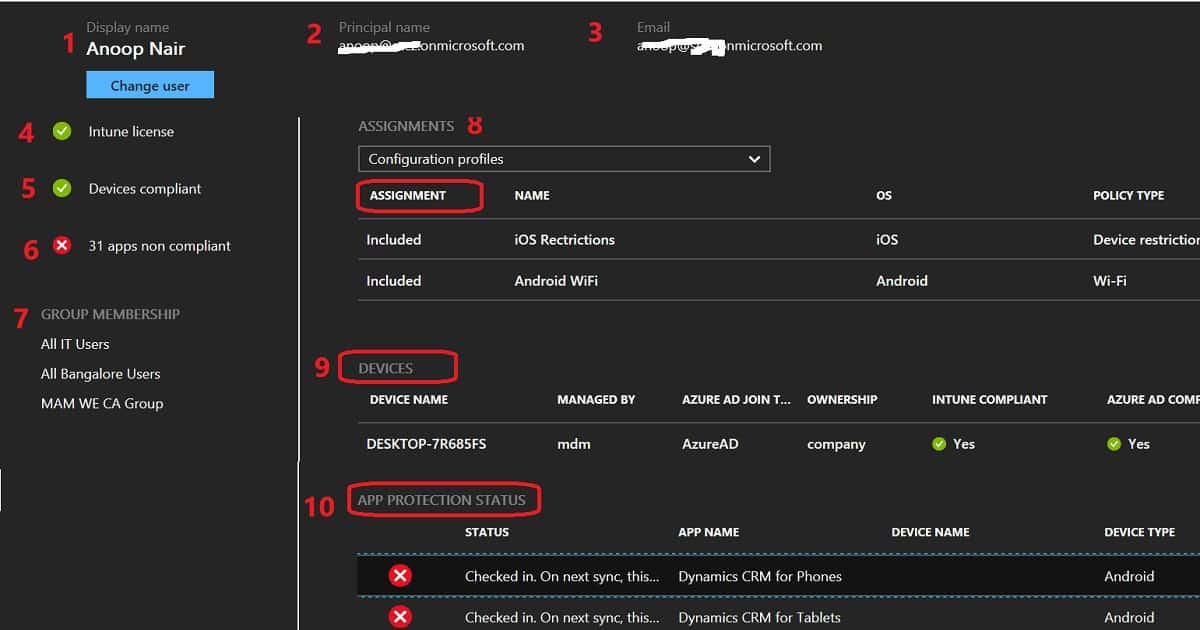
I selected Anoop Nair as the user. All the details of this user will be available in the troubleshooting tab. This will help the Intune admin to confirm whether we have targeted all the applications and policies to correct AAD groups. You can check and confirm whether the user.
You can check and confirm whether the user
Does the user have a valid Intune license or not
Is the user part of the correct AAD group or not
Is the Device compliant or not
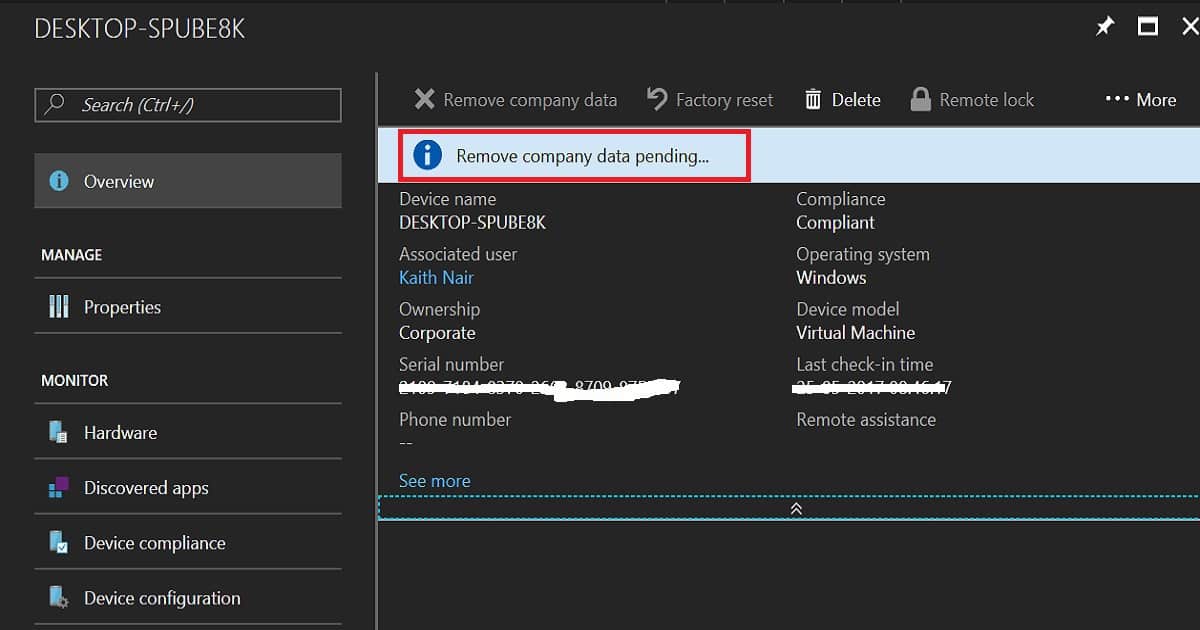
Status of Company Data Removal/wipe from a device
How to Start Troubleshooting Intune Issues and Fix them with Easy Steps – Table 1
Another set of user details you can check in the troubleshooting tab of Intune Blade is the Principal name of the selected user and Email ID. All the other information available in the Intune troubleshooting blade are
Intune license assigned to a user or not
Whether Devices compliant status
Whether apps are in a compliant state or not
Azure AD Group membership for the user
Mobile Apps Assignment to the user
Compliance policies deployed or assigned to users
App protection status for the devices
Configuration profile deployment status for the user
List of the devices for that user and status of devices
There are some red icons, as seen in the video tutorial and the screenshot below. Those red icons could indicate potential issues with application or policy deployments. I could see problems with Anoop’s Android device. The app protection status does not look suitable for Android devices. The Intune troubleshooting blade provides a valuable report that “31 apps non-compliant“.
Intune Troubleshooting Blades has six (6) Assignment categories. Each type provides details about the user assignments. If some terms are missing, we need to examine the targeting AAD groups of those policies.
Mobile Apps
Compliance Policies
Configuration Profiles
App Protection Policies
Windows 10 Update Rings
Enrollment Restrictions
How to Start Troubleshooting Intune Issues and Fix them with Easy Steps – Fig.6
The above information is essential to start Intune troubleshooting from the Azure portal. From the troubleshooting tab, we can directly access details of each assigned policy for that user. We can also look at the device properties and hardware information for more detailed troubleshooting.
For example, you have started a company data wipe action for a device, but the device or user can still access the corporate mail from the device. Intune admin can directly search for the user from the Intune troubleshooting session and get all the user’s device details. Once the device is identified, you can check the following information about it.
Device name, Managed by, Azure AD join type, Ownership, Intune compliant, Azure AD compliant, OS, OS version, and Last check-in.
How to Start Troubleshooting Intune Issues and Fix them with Easy Steps – Fig.7
Anoop C Nair has been Microsoft MVP for 10 consecutive years from 2015 onwards. He is a Workplace Solution Architect with more than 22+ years of experience in Workplace technologies. He is a Blogger, Speaker, and Local User Group Community leader. His primary focus is on Device Management technologies like SCCM and Intune. He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security, Career, etc.
Let’s discuss how to Schedule iOS Automatic Updates Using Intune Policies. Do you have supervised iOS devices managed through Intune?
If so, you may know that iOS software updates will force installation updates on supervised mode iOS devices. Intune has a new policy to prevent/delay these force updates.
This option will also give more granular control over iOS software updates. This post will discuss how to Prevent iOS Automatic Updates Using Intune Policies.
New options have been added to the automatic iOS and iPad OS updates. The following are the exciting options available for this update.
How to Create iOS Software Update Policies in Intune? iOS Automatic Updates Using Intune
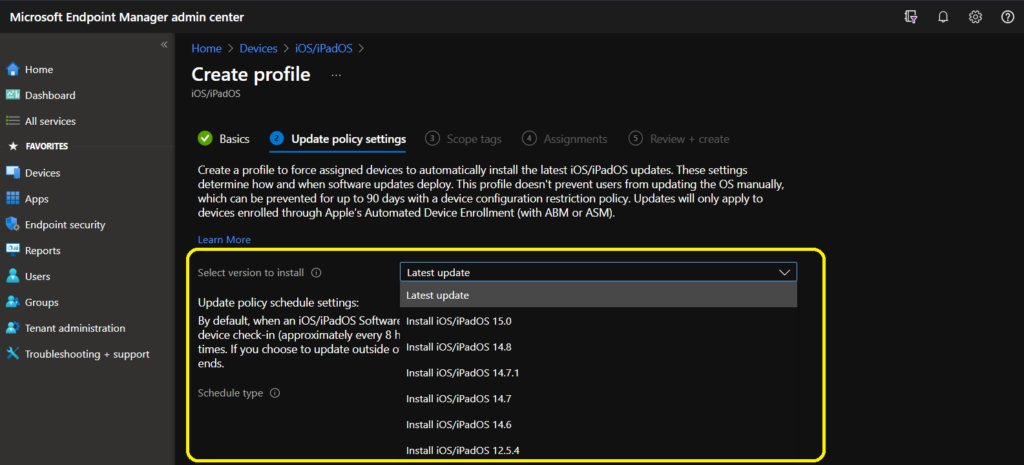
This Intune policy will help delay iOS automatic updates. iOS devices should be part of the Apple DEP program and managed through supervised mode. Create a profile to force assigned devices to automatically install the latest iOS/iPadOS updates.
These settings determine how and when software updates deploy. This profile doesn’t prevent users from updating the OS manually, which can be controlled for up to 90 days with a device configuration restriction policy. Updates will only apply to devices enrolled through Apple’s Automated Device Enrollment (ABM or ASM).
How to Create iOS Software Update Policies in Intune
Login to the MEM Admin Center portal
Navigate via the Devices – iOS/iPad Update Policies (Update policies for iOS/iPadOS)
Click on + Create update policy
From the Update Policy Settings page for iOS/iPad OS update – The version of iOS/iPadOS to install on devices at the time of update
How to Schedule iOS Automatic Updates Using Intune Policies – Table 1
You can create a new policy with a proper name and description of the policy. This policy will prevent iOS Automatic Updates from forcefully getting installed on supervised iOS devices.
How to Schedule iOS Automatic Updates Using Intune Policies – Fig.1
Update Policy Schedule Settingsfor iOS/iPad OS Devices
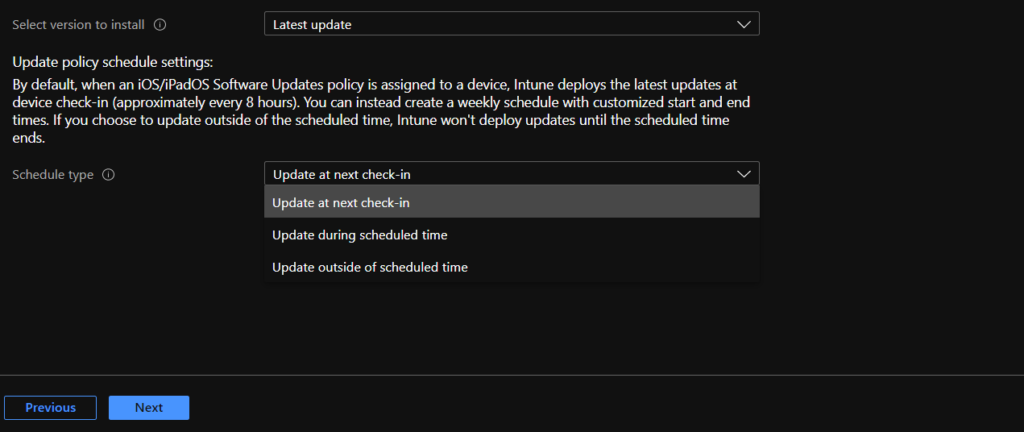
Update policy schedule settings: By default, when an iOS/iPadOS Software Updates policy is assigned to a device, Intune deploys the latest updates at device check-in (approximately every 8 hours).
You can instead create a weekly schedule with customized start and end times. If you choose to update outside the scheduled time, Intune won’t deploy updates until the scheduled time ends.
Select Type and Schedule for iOS update (When the updates will occur. Additional input is required to schedule updates during or outside of scheduled times)
Update at next check-in
Update During the scheduled time
Update Outside of the scheduled time
How to Schedule iOS Automatic Updates Using Intune Policies – Fig.2
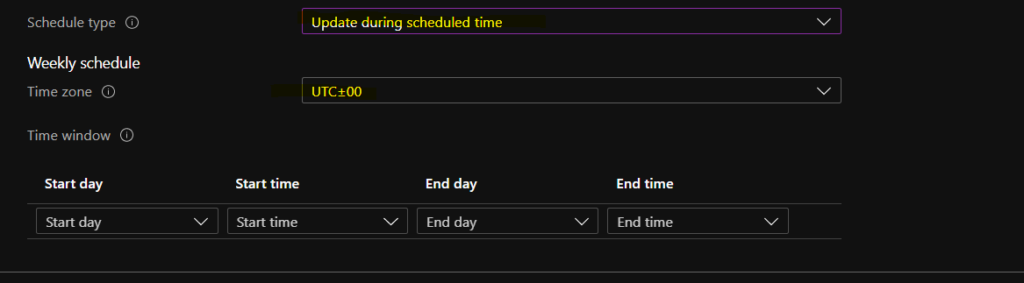
Update During the scheduled time, stop updates from being installed at any random time. By configuring this policy, you can delay the software update (automatic update) of iOS on the device.
Weekly Schedule-> TimeZone, Start Day, Start Time, End Day, End Time
You can select the Time zone, Date, and time for iOS/iPad OS updates. Select the time zone of the targeted devices – In this section, you must select the Time Zone of the devices you want to target for this policy. For the India Time Zone, I selected UTC+5:30.
Start Time—Select the beginning of the interval to stop iOS software updates from Installing on supervised iOS devices. You usually don’t want to install software updates on iOS devices during business hours. This will help you schedule iOS phone updates via Intune policies.
End Time – Select the end of the interval to stop iOS software updates from installing on supervised iOS devices.
Start Day of the update: You can select any day of the week from the start and end day options, from Sunday to Saturday. End the Day of the iOs/iPad OS update by selecting any day between Sunday and Saturday.
How to Schedule iOS Automatic Updates Using Intune Policies – Fig.3
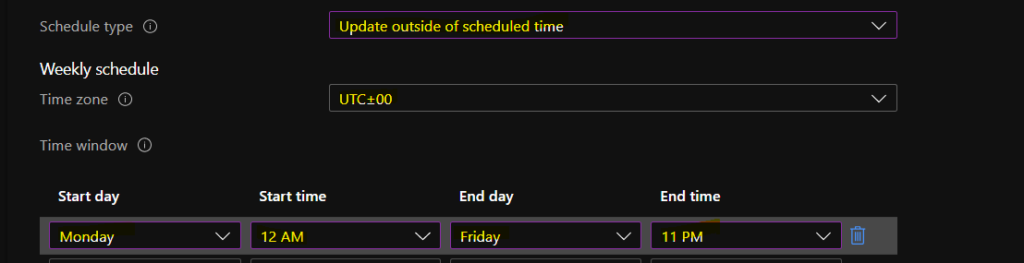
You can select the iOS/iPad updates outside the scheduled time. You must set a scheduled time when you don’t want this update to happen on iOS devices. The update will be initiated outside the scheduled time configured below.
How to Schedule iOS Automatic Updates Using Intune Policies – Fig.4
How to Deploy or Assign Intune iOS Software Update Prevention Policy?
Once the Intune iOS Automatic Updates prevention Intune Policy is created, you can start assigning this policy to Azure AD Device groups. Deploy Updates Prevention Policy to iOS Devices.
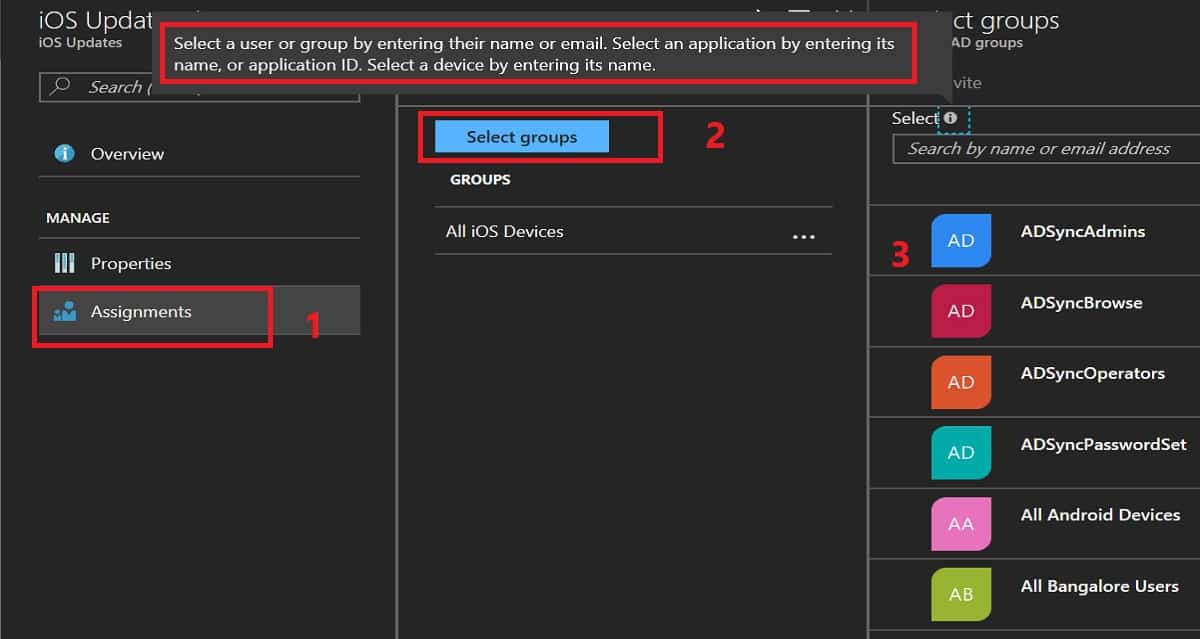
Select Assignments—Click on Select Groups to find the appropriate Azure AD group to target the iOS update prevention policy. Once the policy is deployed to devices, the iOS software update will be postponed.
It would help to be careful about the policy settings while targeting the AAD device groups. In the policy configuration, there is an option to configure the devices’ time zones. Time zone configuration in this policy is a bit tricky.
Reporting options for iOS update policies in Intune are coming soon.
How to Schedule iOS Automatic Updates Using Intune Policies – Video 1
We are on WhatsApp now. To get the latest step-by-step guides, news, and updates, Join our Channel. Click here. HTMD WhatsApp.
Author
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC, He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC. He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.
Let’s discuss how to block How to Block Windows Devices from Enrolling to Intune. I have seen a scenario where Intune exclusively manages iOS and Android devices.
Windows devices are managed through SCCM and must be disabled or prevented from enrolling in Intune. We can achieve this with new Intune Enrollment restriction policies. I have a blog post explaining “How to Use Intune Enrollment Restriction Rules“.
This post covers everything you need to know about stopping Windows devices from enrolling in Intune. It explains each step clearly so you can understand it easily. Whether you’re just starting out or want to improve your setup, this post will guide you through keeping your devices out of Intune’s management system.
I tested Windows 10 enrollment to Intune via “Add Work or School Account.” This was tested successfully before restricting Windows 10 devices from the Intune console. Check out the following message after the Windows 10 device is successfully enrolled. More details are in the video below.
How to Restrict Windows 10 Devices from Intune Management
This video provides a step-by-step guide on restricting Windows 10 devices from being managed through Intune. It covers all the necessary details, including the settings and configurations required to ensure proper restriction.
How to Block Windows Devices from Enrolling to Intune – Video 1
Add Work or School Account
“We’ve added your account successfully, and you can now access your organization’s apps and Services. The last step is setting up your new PIN to unlock this device.”
How to Block Windows Devices from Enrolling to Intune – Fig.1
Change the Intune Device Enrollment Policy to Restrict Windows Device
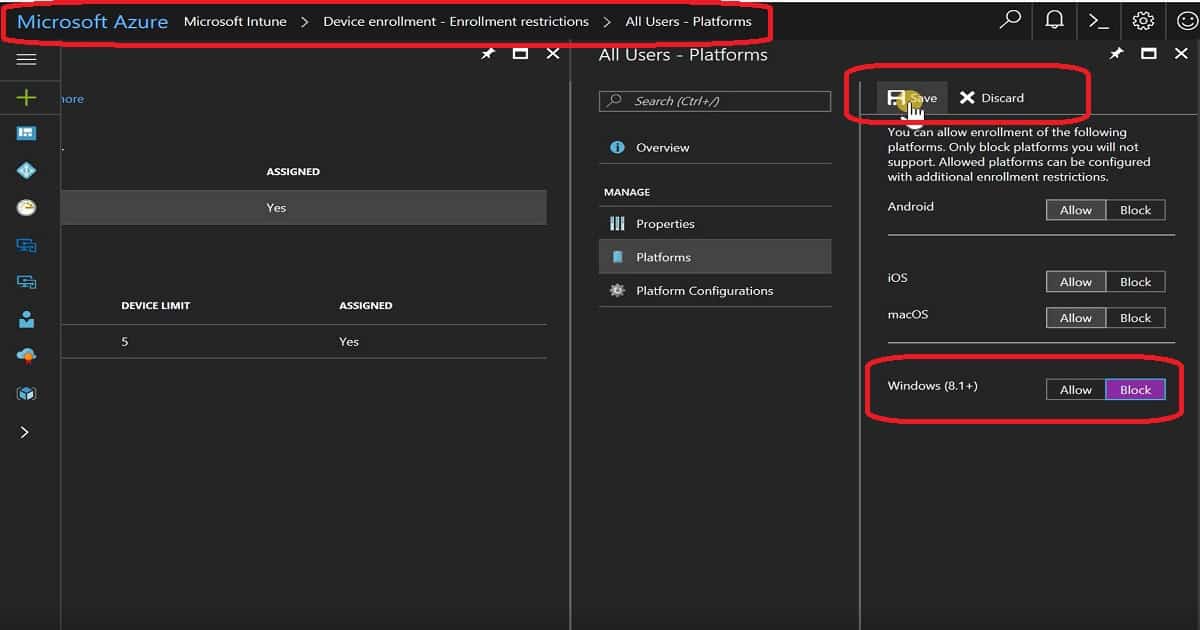
Navigate through the New Azure portal – Microsoft Intune – Device Enrollment – Enrollment restrictions. You will be able to see two Intune enrollment restriction policies: 1.
Device Type Restrictions and 2. Device Limit Restrictions. Device Type restriction is where we can restrict Windows (8.1 +) devices from enrolling on Intune.
This policy will prevent Windows 8.1 and later devices from Intune management and restrict Windows 10 device enrollment. Windows 10 mobile devices will also be blocked when we configure this policy.
How to Block Windows Devices from Enrolling to Intune – Fig.2
End-User Experience of Windows 10 Device Restriction
I successfully added a Work or School account to a Windows 10 1703 device. The one change I noticed through the enrollment process is that it didn’t prompt for MFA. After this enrollment, the message I received differed from the one I got above.
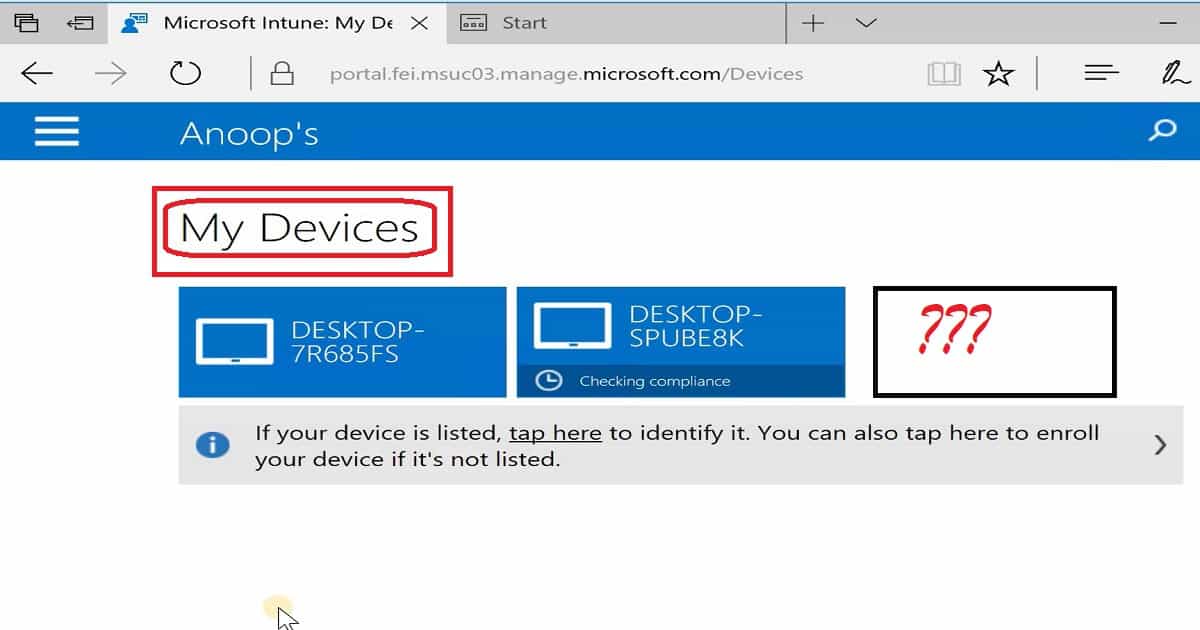
We’ve successfully added your account, and you can access your organization’s apps and Services. Moreover, the machine was NOT available in the company portal application under the “My Devices” list. So, the device enrollment never failed as I expected. The device was enrolled without any error.
However, the main question is whether this device would be managed via Intune. Did the device receive Intune policies? The answer is in the paragraph below.
How to Block Windows Devices from Enrolling to Intune – Fig.3
Experience on Azure – Intune Portal for Windows 10 Restriction
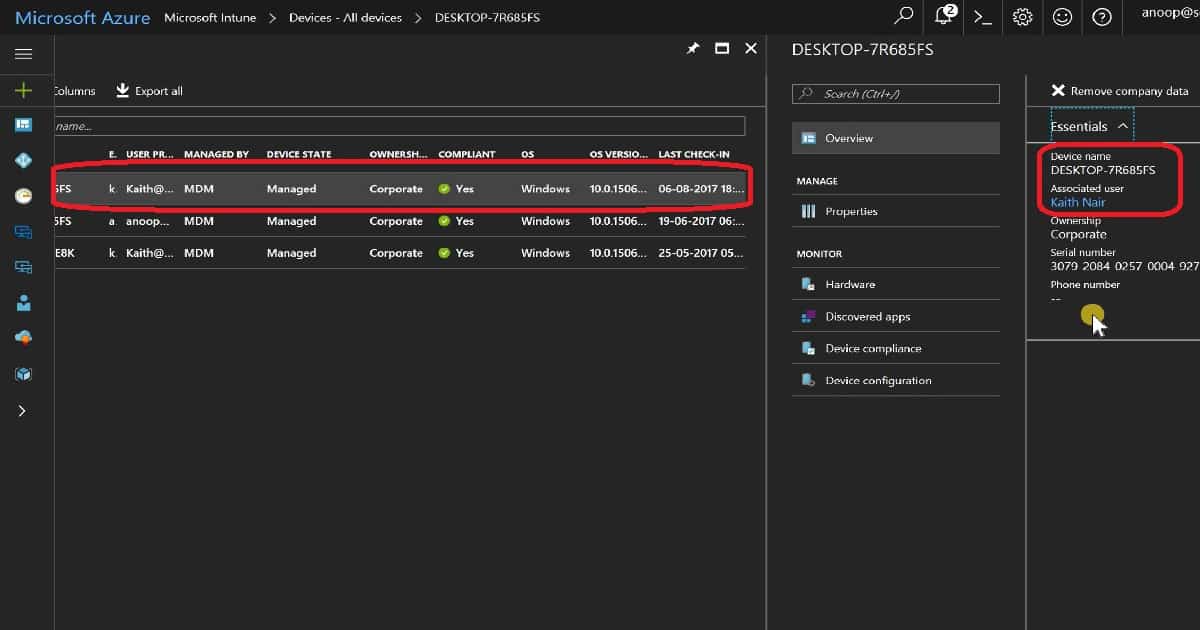
The Windows 10 enrolled device was NOT listed in Intune – All Devices (Microsoft Azure – Microsoft Intune – Devices – All Devices). However, the device was listed in Azure AD, as shown in the video tutorial.
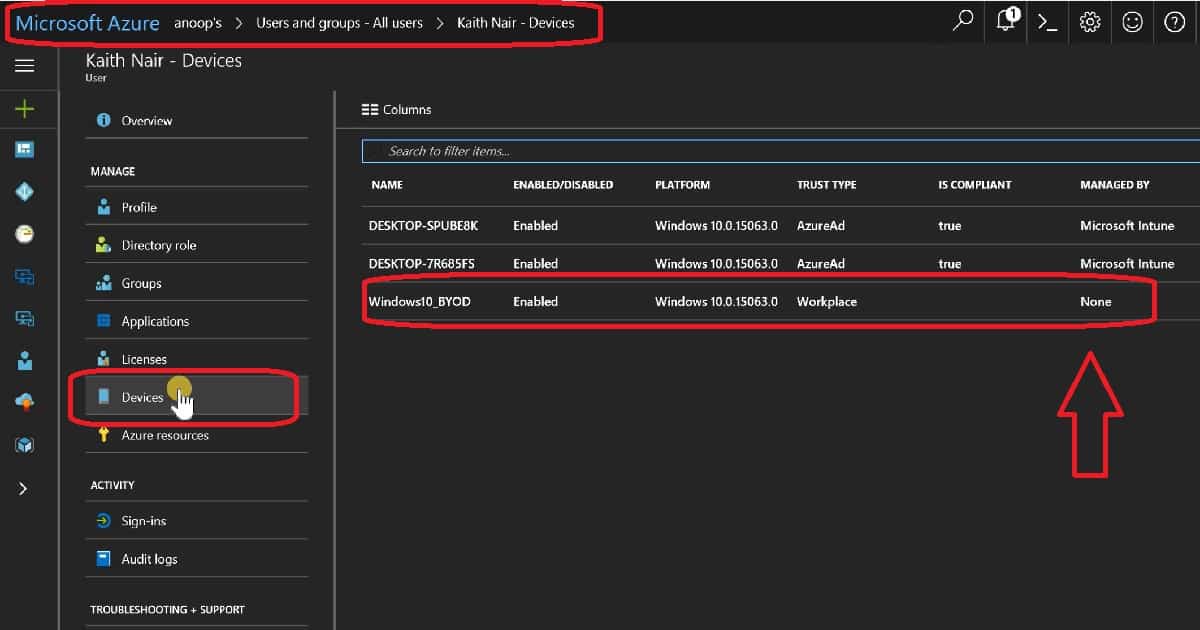
The Windows 10 device was listed under Azure AD against the user’s devices (Microsoft Azure—Users and groups—All users > Kaith Nair). But, as you can see in the screenshot below, the Windows device is NOT MANAGED by INTUNE.
Hence, the device won’t receive any Intune policies or be managed through Intune. It also won’t have access to corporate mail, SharePoint, OneDrive, and Skype for Business.
NAME
ENABLED/DISABLED
PLATFORM
TRUST TYPE
IS COMPLIANT
MANAGED BY
Windows10_BYOD
Enabled
Windows 10.0.15063.0
Workplace
None
None
How to Block Windows Devices from Enrolling to Intune – Table 1
How to Block Windows Devices from Enrolling to Intune – Fig.4
References
Set Intune enrollment restrictions policies – here
How to configure device restriction settings in Microsoft Intune – here
We are on WhatsApp now. To get the latest step-by-step guides, news, and updates, Join our Channel. Click here. HTMD WhatsApp.
Author
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC, He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.
Let’s discuss the Intune MSI Application Deployment Video Guide Microsoft Endpoint Manager Step-by-Step Guide. How to upload and deploy MSI applications to Windows 10 machines with Intune via Azure console? MSI application deployment could be one of the most used features in Intune (at least for a couple of years).
This video post will show the step-by-step process of MSI application deployment (Intune LOB application deployment).
NOTE! – Do not include the msiexec command or arguments, such as /i or /x, as they are automatically used. For more information, see Command-Line Options. If the .MSI file needs additional command-line options, consider using Win32 app management.
This post is also an end-to-end guide to creating MSI applications in Intune via the Azure portal. In the following post, “How to Deploy MSI App to Intune MDM Using SCCM CB and Intune“, I already blogged about MSI MDM deployment via the MDM channel. This will include:-
Uploading the MSI LOB app to Intune
Deployment or Assignment options
End-User Experience on Windows 10 machine
How to Troubleshooting with event logs and Pending Sync
How to get application installation status messages back to the Intune console
How to Deploy MSI LOB App from Intune Azure Console End-to-End Guide
In this video, you will learn how to deploy an MSI Line-of-Business (LOB) application using the Intune Azure Console from start to finish. The guide provides a detailed, step-by-step process covering everything you need.
Intune MSI Application Deployment Video Guide Microsoft Endpoint Manager Step-by-Step Guide – Video 1
Intune MSI Application Deployment Video Guide Microsoft Endpoint Manager Step-by-Step Guide –Upload MSI LOB Application to Intune
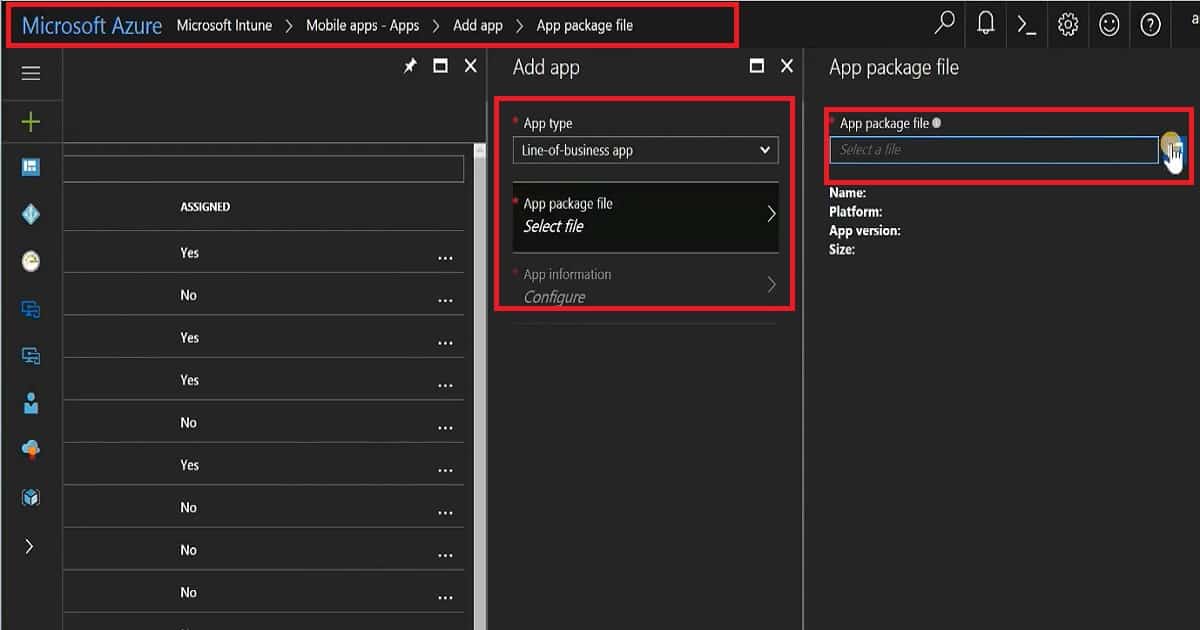
Uploading the MSI LOB app to Intune is a very straightforward process. Log in to the Azure portal, navigate via Microsoft Intune -> Mobile Apps -> Apps -> + Add button, and select the app type as “Line-of-Business app.” Click on “App package file,” browse to the MSI source file location, and click on the OK button, as you can see in the video here.
Intune MSI Application Deployment Video Guide Microsoft Endpoint Manager Step-by-Step Guide – Fig.1
You must complete the “App information” section before you can proceed with uploading the MSI to Intune. There are a couple of mandatory fields. Command-line options are also available in this section. However, as I have experienced, you can also see in the video.
I have not used any silent switch for MSI, but by default, Intune/MDM on Windows 10 will install the app as silent (without any user interaction or input). Click on the ADD button to complete the MSI app creation process in Intune on the Azure portal.
Deployment or Assignment options of MSI Intune LOB application deployment
It would be best to wait until the application is successfully uploaded to Intune before you can create an assignment (or deployment). An assignment is a method that we use to deploy MSI applications to Windows 10 devices. You can deploy applications to Azure AD dynamic user groups or device groups. In this video/scenario, I used the AAD dynamic user group to target the MSI LOB apps.
More details are available in the video here. There are different deployment types available in Intune.
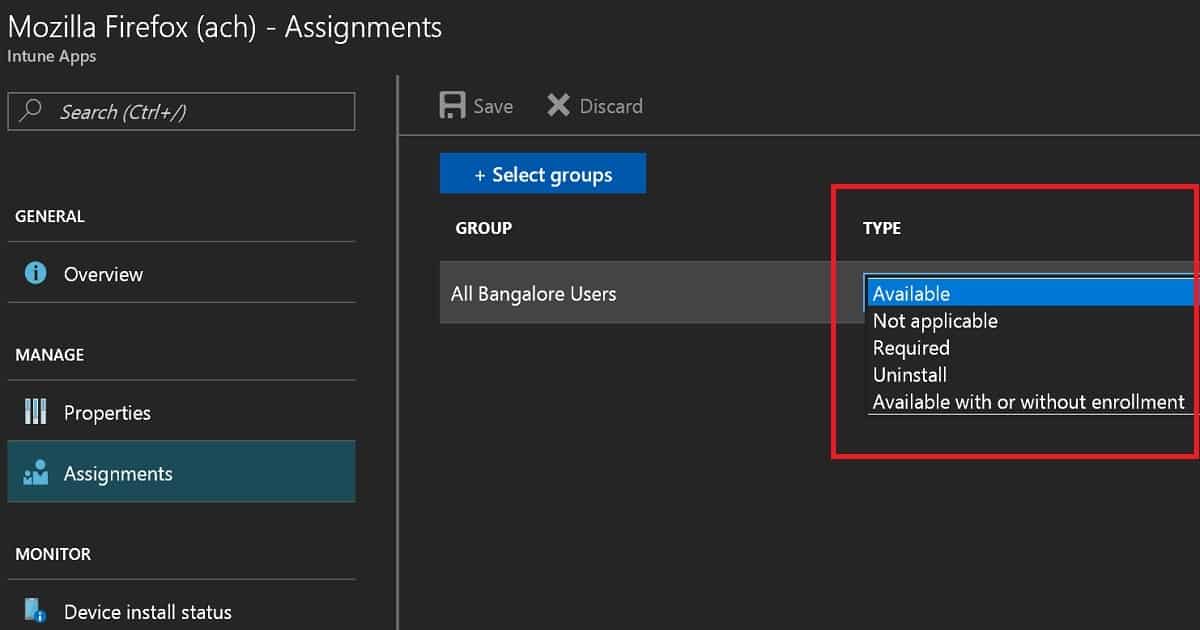
Available – The user needs to go into the company portal and trigger the installation. Not applicable – Won’t get installed Required – Forcefully get installed without any user interaction Uninstall – Remove the application from the device Available with or Without enrollment – Mobile Application Management (MAM) without MDM enrollment scenarios.
Intune MSI Application Deployment Video Guide Microsoft Endpoint Manager Step-by-Step Guide – Fig.2
End-User Experience on Windows 10 machine
Windows 10 machines will get the new application deployment policy once the assigned user is logged into that machine. What is the option to speed up the application deployment to the machines? You need to sync with Intune services using the following method (manually).
You can go to “Settings—Access Work or School—Work or School Account—Info (click on this button)” and click on Sync. This will initiate a Windows 10 machine sync with Intune services, and after a successful sync, the machine will get the latest application policies.
How to Troubleshooting with Event Logs and Pending Sync
Unlike SCCM/ConfigMgr deployments, we don’t have log files to look at the application installation status via the MDM channel on Windows 10 machines. So, it would be best if you relied on the Company portal for troubleshooting the MSI application troubleshooting.
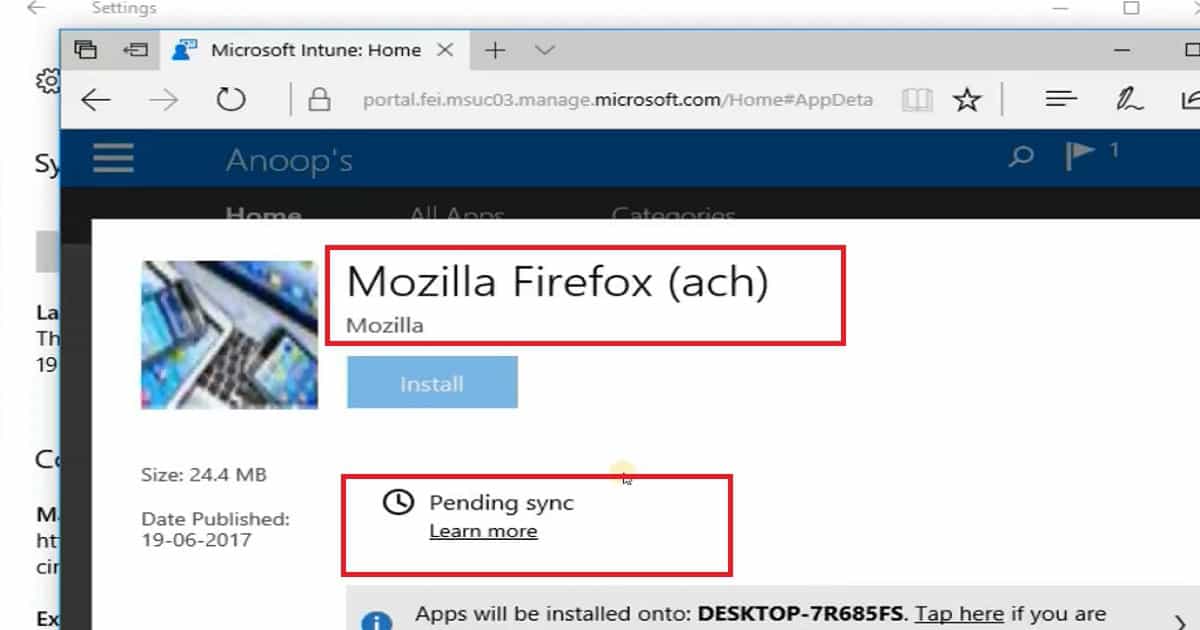
As you can see in the following picture, the installation is waiting for “Pending Sync.”
As mentioned above, you can immediately initiate a manual sync to kick-start the installation process.
Event logs – Windows Logs – Applications are where you can get the status of MSI application installation via MDM or Intune channel on to Windows 10 machine.
Intune MSI Application Deployment Video Guide Microsoft Endpoint Manager Step-by-Step Guide – Fig.3
How to get application installation status messages back to the Intune console
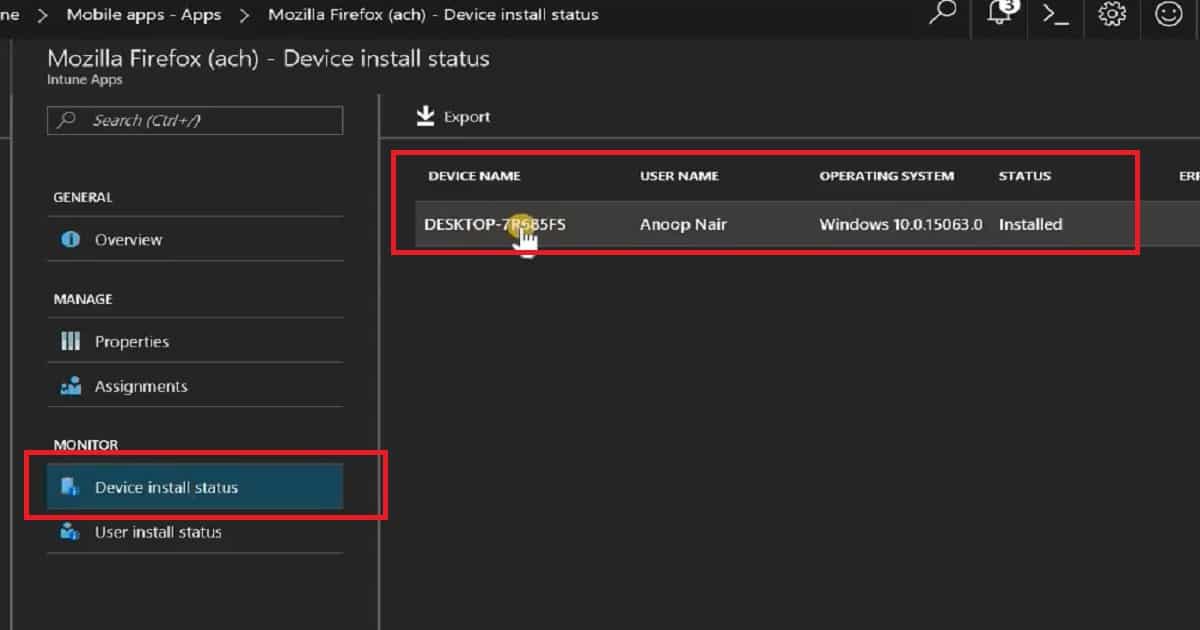
To get the installation status of the MSI LOB apps to Intune on the Azure portal, you need to sync your work or school accounts with Intune services. The installation status will be blank in the Intune blade unless the device is synced with Intune after the application is installed on the Windows 10 machine.
Initiate thSyncnc via “Settings – Access Work or School – Work or School Account – Info (click on this button)” and click on Sync. Once thSyncnc is completed successfully, you can try to check the Intune Device Install Status in Intune to check the status.
Intune MSI Application Deployment Video Guide Microsoft Endpoint Manager Step-by-Step Guide – Fig.4
We are on WhatsApp now. To get the latest step-by-step guides, news, and updates, Join our Channel. Click here. HTMD WhatsApp.
Author
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC, He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC. He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.
Enrollment Restrictions control whether a device can enroll into Intune.
Device Restriction Profiles manage settings on devices after enrollment.
Enrollment Restrictions help control device platforms, ownership types, OS versions, and device limits.
Device Restriction Profiles configure security, hardware, browser, privacy, and user experience settings.
Let’s discuss the Differences Between the Intune Enrollment Restriction and Device Restriction. These policies manage device settings and user experiences by enabling, disabling, or configuring features such as browsers, security settings, data sharing, and system functionality. Understanding the differences between these policy types helps administrators implement effective device management and security controls. Enrollment Restrictions control whether a device is allowed to enroll into Intune.
Table of Contents
Table of Contents
Differences Between Intune Enrollment Restriction Device Restriction
If a device does not meet the enrollment requirements, it is prevented from joining the Intune management environment. Device Restriction Profiles, on the other hand, are configuration policies applied after enrollment. How to Restrict Personal Android Devicesfrom Enrolling into Intunepost helps you to provide detailed instructions on restricting personal Android devices from enrolling into Intune using Endpoint Manager (MEM).
It covers the steps necessary to configure enrollment restrictions, ensuring that only corporate-owned devices can be enrolled and managed through Intune. Device restrictions are entirely different from Enrollment restrictions. Both options have different use cases, which will be explained in this post.
Intune Device restriction profiles (Enrollment Device Platform Restrictions) are policies similar to GPO from the traditional device management world. Most enterprise organizations use GPO to restrict corporate-owned devices. These are security policies that need to be applied to devices. Intune Device restriction policies control various mobile device settings and features (iOS, Android, macOS, and Windows 10).
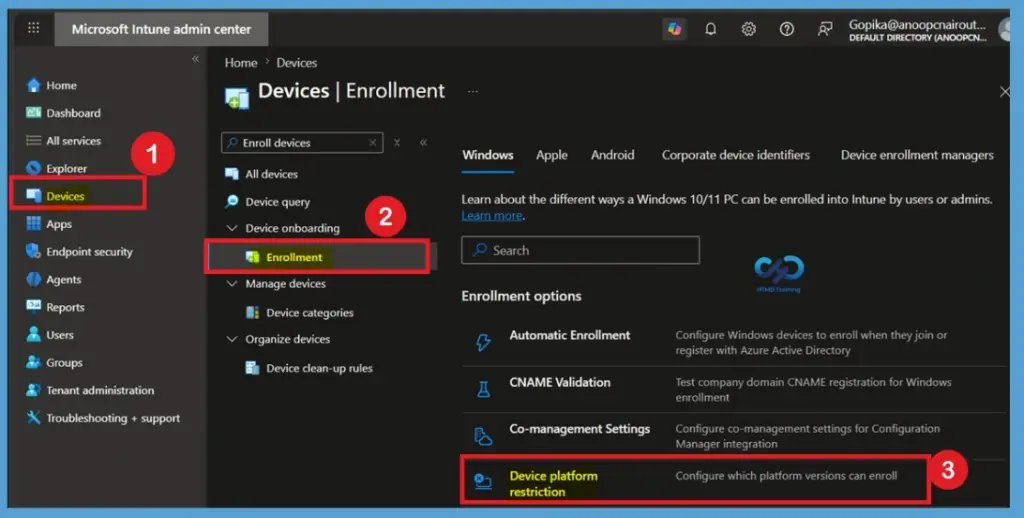
Enrollment device platform restrictions make more sense. Navigate to Devices – Enrollment – Device Platform Restrictions.
Differences Between Intune Enrollment Restriction Device Restriction – Fig.1
This type of policy could apply to different categories, including security, browser, hardware, and data-sharing settings. For example, you could create a device restriction profile policy that prevents Windows users from sharing the internet or using Cortana, etc. Intune Device Restriction profiles can be deployed to specific users/devices in AAD groups, whereas Intune Enrolment restriction policies can’t be deployed to specific user/device groups in Azure AD. The following section of this post provides more details.
From the Enrollment page, select Device platform restriction to configure which platforms, ownership types, and operating system versions are allowed to enroll into Intune.
These restrictions are evaluated during the enrollment process and can help organizations block unsupported devices or restrict enrollment to corporate-owned devices only.
The Device Platform Restrictions policy allows administrators to
Allow or block specific device platforms.
Restrict personal device enrollment.
Configure minimum and maximum OS versions.
Control enrollment based on device ownership.
Differences Between Intune Enrollment Restriction Device Restriction – Table.1
Differences Between Intune Enrollment Restriction Device Restriction -Fig.2
Intune Device Limit Restrictions
Enrollment is the first part of Mobile Device Management. Why do we need to enroll a mobile device into Intune? Enrollment is the first step for management. When a device is enrolled in Intune, they have issued an MDM certificate, which that device then uses to communicate with the Intune service.
In several scenarios, we need to block employees from enrolling their devices in the corporate management platform. You want to block devices not secured enough to enroll in Intune, such as personal devices. Also, we could block devices with lower OS versions. How is this possible from Intune? Difference Between Intune Enrollment Restriction Device Restriction Profile | Configuration Manager ConfigMgr.
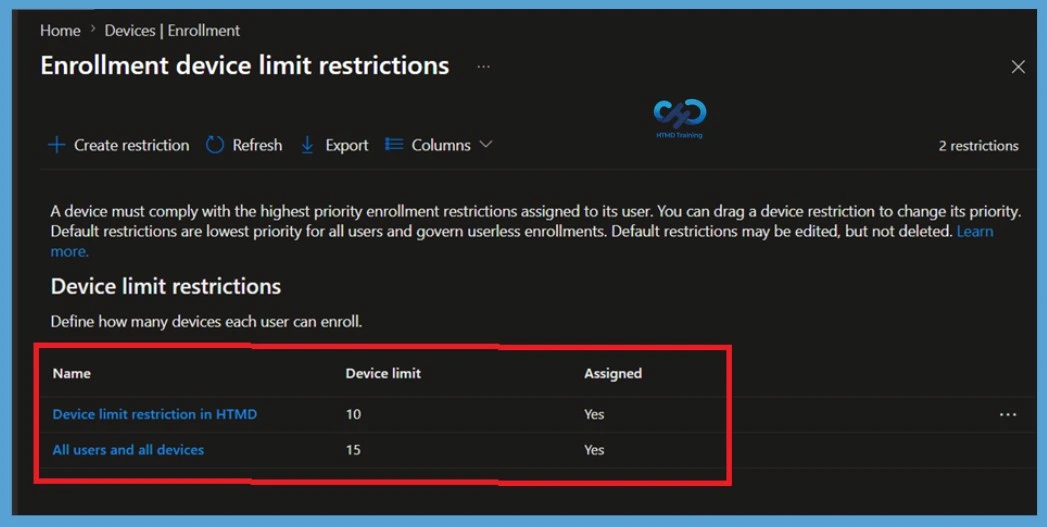
Navigate to Microsoft Intune >Enroll Devices>Enrollment device limit restrictions. You will see two Intune enrollment restriction policies.
Differences Between Intune Enrollment Restriction Device Restriction- Fig.3
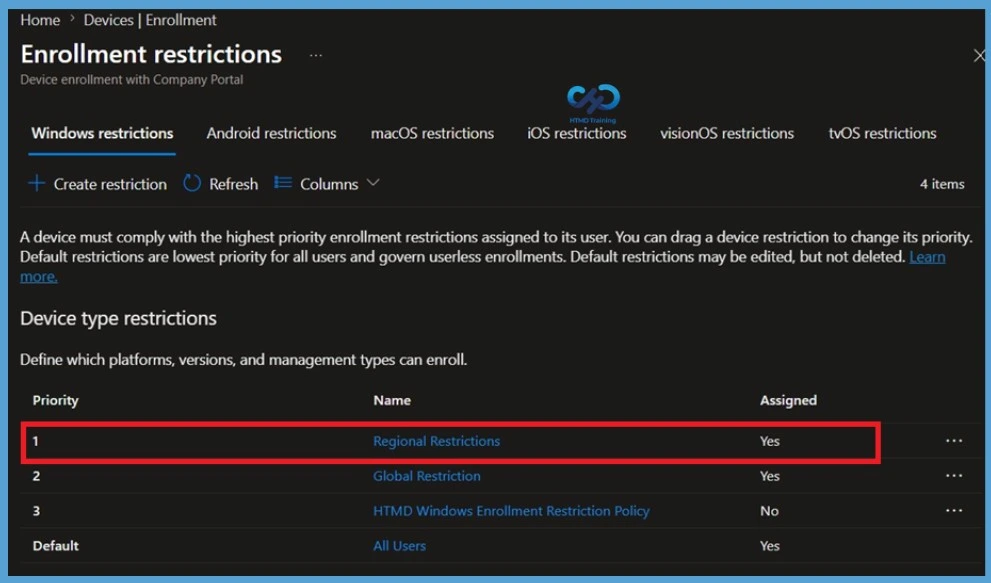
Device Type restriction is where we can define which platforms, versions, and management types can enroll. So, all other devices are blocked from Intune enrollment. The only problem with Intune enrollment restrictions I can think of is that device type restrictions in Intune are deployed to “All Users, ” we can’t deploy or assign Intune enrollment restriction policies to “specific user group.” At the moment, the device type restrictions policies are tenant-wide configurations.
This policy is useful for preventing excessive device enrollments and maintaining better control over managed devices within the organization.
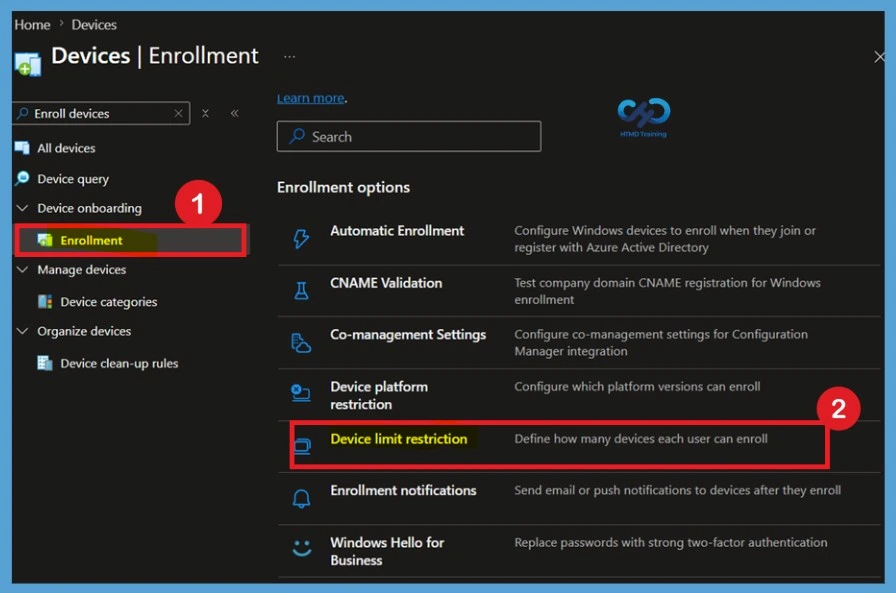
From the Enrollment page, select Device limit restriction to view or create enrollment limit policies.
The Device Limit Restrictions page displays all configured policies along with their assigned device limits. Administrators can create multiple policies and assign them to different user groups based on organizational requirements.
Differences Between Intune Enrollment Restriction Device Restriction – Fig.4
Need Further Assistance or Have Technical Questions?
Anoop C Nair is a Workplace Technology solution architect with 25+ years of experience. Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11+ years! He is a blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His main focus is on Device Management technologies like Intune, Windows, and Cloud PC. He writes about technologies like Intune, SCCM, Windows, Cloud PC, Entra, and Microsoft Security.
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC. He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.
Let’s learn how to Setup Android Work Support Step by Step Guide Microsoft Intune. Google’s strategic approach is to support management only via the Android Work channel, and Microsoft Intune’s strategy is to help Android work. This post will show how to set up Android work support in Intune portal.
As you can see in the embedded video guide attached to this post, we will learn how to unbind or change the Gmail/Google account we used to set up Android work support in the Intune Azure portal. Once the existing Gmail account has been removed, we can use a different Gmail account to configure or set up Android Work support in the Intune Azure console.
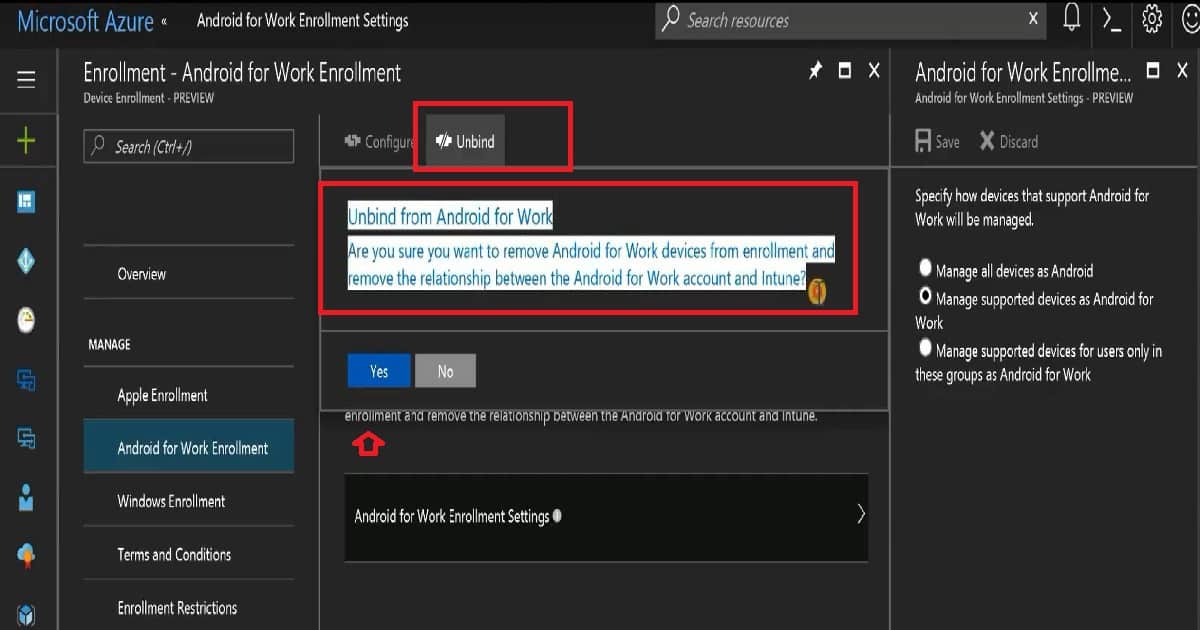
How to Unbind Android Work Account from Intune Azure Portal
We must unbind the account from the Intune Azure console to change the Setup Android Work Google account. The Unbind button in Intune Azure removes support for Android Work enrollment and eliminates the relationship between the Android work account Gmail and Intune.
I have seen some delay in unbinding the Gmail account from the Intune blade in the Azure portal. As you can see in the video here, I removed the Gmail account from the Android work setting in the Intune blade in the Azure portal, but it took 2 minutes for these changes to reflect. However, the removal of Android Work was immediately reflected on the Intune Silverlight portal.
How to Setup Android Work Support Step by Step Guide Microsoft Intune – Fig.1
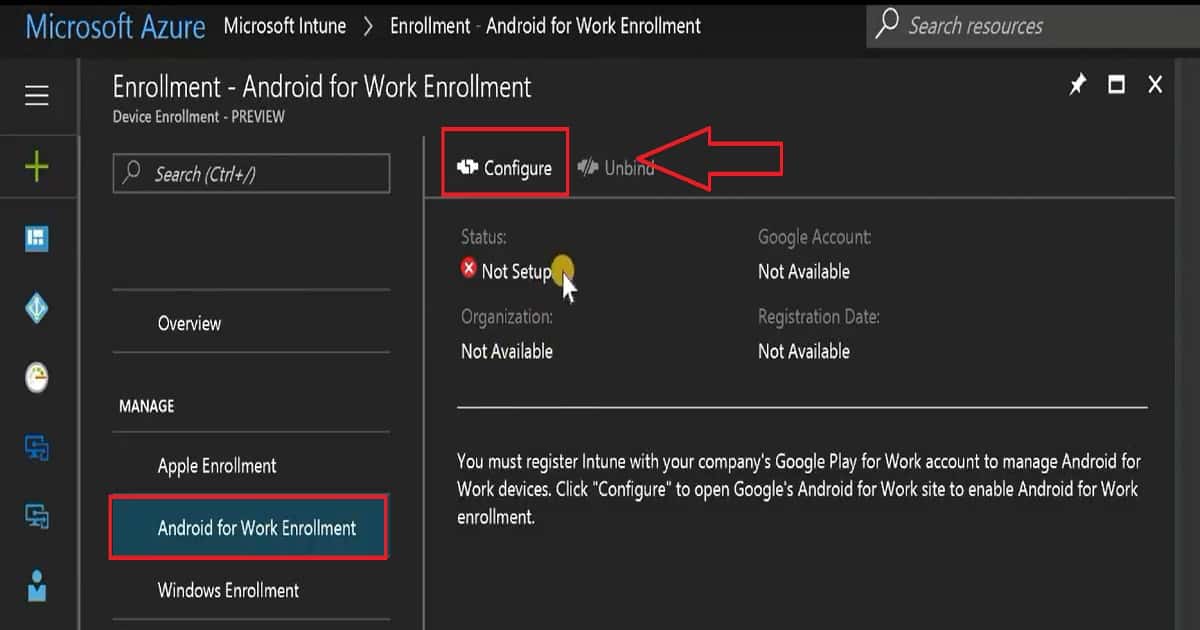
Setup Android Work Support in Intune Azure Portal
The configuration or setup of Android Work support in the Intune Azure portal is very similar to that in the Silverlight portal. You need to click the Configure button to open a pop-up where you can log in with a new Gmail or Android Work account. The Google configuration wizard will help you set up the connection between Intune and Google APIs like Google Play for Work, Android Work management, etc.
Microsoft Intune
Enrollment
Android for Work Enrollment
How to Setup Android Work Support Step by Step Guide Microsoft Intune – Table 1
How to Setup Android Work Support Step by Step Guide Microsoft Intune – Fig.2
Setting up Android Work Enrollment & Management via Intune
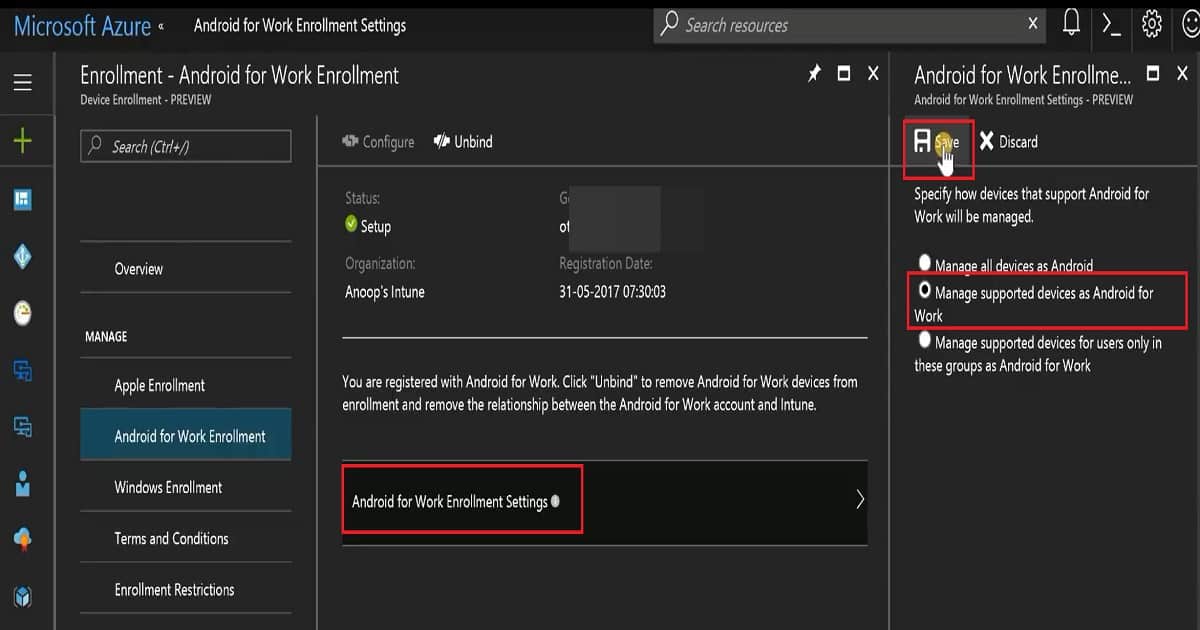
Android for Work enrollment settings are the same as those in the Intune Silverlight console. In the Intune Azure portal, we have three options for setting up Android work enrollment.
1.Manage all devices as Android – This is opposite to Google’s strategic approach regarding managing the Android devices 2. Manage supported devices as Android for Work—As per my testing, all Android 6.0 and above devices are supported for Android work enrollment and management via Intune. I have a blog post that explains A4W supportability, “Intune Entry Level Low-Cost Device Support for Android for Work Enrollment.” Hence, this is my best bet option for enrollment. 3. Manage supported devices for users only in these groups, such as Android Work. This could be used in the testing or pilot process if your organization doesn’t have a test Intune environment.
How to Setup Android Work Support Step by Step Guide Microsoft Intune – Fig.3
We are on WhatsApp now. To get the latest step-by-step guides, news, and updates, Join our Channel. Click here. HTMD WhatsApp.
Author
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC, He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC. He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.
Let’s discuss how to Create SCEP Certificate Profiles in Intune and Deploy them to Windows 10 Devices. In this post, we will create and deploy an SCEP Certificate to Windows 10 Devices (How to Deploy an SCEP Certificate to Windows Devices).
NDES setup for SCEP – The NDES connector should be installed on your data center, and the NDES connector should be able to talk to the CA serverand use the Azure AD App proxy connector if you are using the Azure app proxy.
I won’t cover the setup of NDEs and the Azure AD App proxy connector. Those two configurations are very complex and well explained in other blogs.
Intune SCEP Certificate Deployment for Windows 10 Devices – SCEP Certificates to Users Devices
Before creating a Windows 10 SCEP Certificate in Intune, you need to create and deploy a certificate chain. The certificate chain includes the Root CA certificate and the Intermediate /Issuing CA certificate. Intune offers three certificate profiles: TRUSTED Certificate, SCEP Certificate, and PKCS Certificate. We are not going to use the PKCS certificate for SCEP profile deployment.
Create SCEP Certificate Profiles in Intune Deploy SCEP Profiles to Windows 10 Devices – Video 1
Create SCEP Certificate Profiles in Intune Deploy SCEP Profiles to Windows 10 Devices
Deploying SCEP Certificates to Windows 10 Devices will help connect corporate resources like Wi-Fi and VPN profiles. Before making a Windows 10 SCEP Certificate in Intune, you must create and deploy a certificate chain. The certificate chain includes the Root CA and Intermediate /Issuing CA certificates.
Intune offers 3 certificate profiles: TRUSTED Certificate, SCEP Certificate, and PKCS Certificate. We will not use the PKCS certificate for SCEP profile deployment.
Create SCEP Certificate Profiles in Intune Deploy SCEP Profiles to Windows 10 Devices – Fig.1
Intune Create SCEP Certificate Profiles in Endpoint Manager Deploy SCEP profiles to Windows 10 Devices. Following are the high-level tasks for deploying the SCEP Certificate to Windows10 Devices via Intune:-
Create and Deploy iOS Root CA certificate using Intune Azure Portal Create and Deploy iOS Intermediate/Issuing CA Certificate using Intune Azure Portal Create and Deploy SCEP Certificate to iOS Devices using Intune Azure Portal.
Create and Deploy Windows 10 Root CA, Windows 10 Intermediate/Issuing CA Certificate Profiles
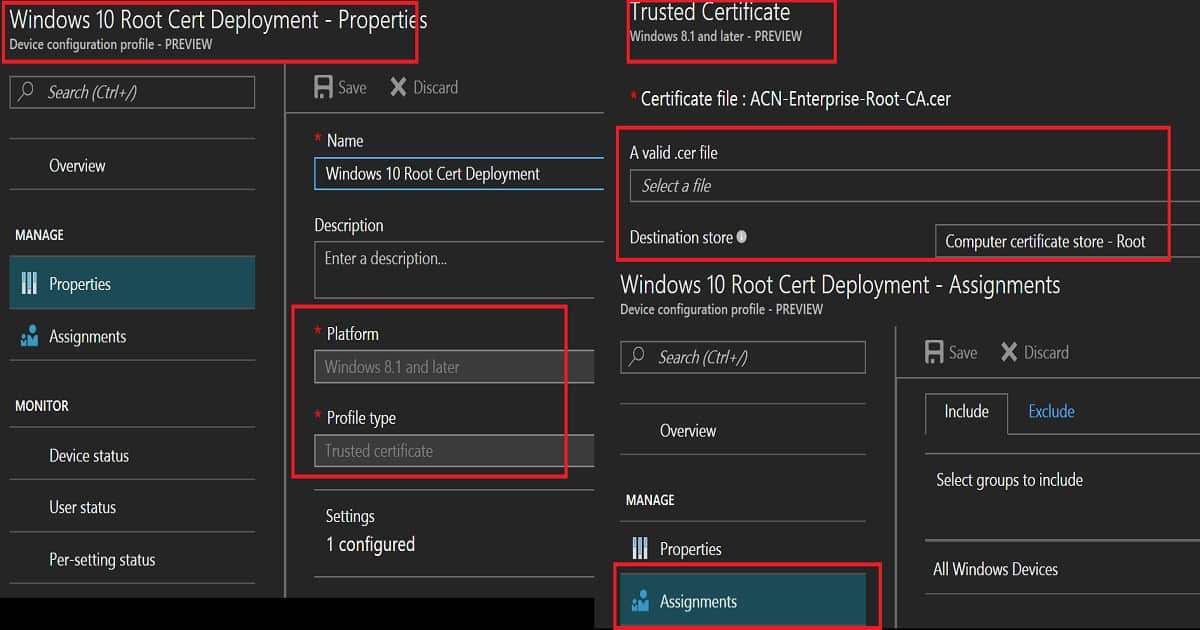
As the first step, we need to create a Root CA cert profile. To create a Root CA cert, navigate through Microsoft Intune—Device Configuration—Profiles—Create a profile. Select the platform as Windows 10 and the profile type as Trusted Certificate. You must then browse and upload your ROOT CA cert (the Name of the cert = ACN-Enterprise-Root-CA.CER)from your CA server.
We need to select a destination store in the Windows 10 Trusted certificate profile. For the root certificate profile, we must select Computer Certificate store—root. Once the settings are saved, you must deploy the root certificate profile to the required Windows 10 devices.
Platform
Profile type
Windows 8.1 and later
Trusted Certificate
Create SCEP Certificate Profiles in Intune Deploy SCEP Profiles to Windows 10 Devices – Table 1
Create SCEP Certificate Profiles in Intune Deploy SCEP Profiles to Windows 10 Devices – Fig.2
We must follow the same process for deploying the Intermediate/Issuing CA certificate profile via Intune. Make sure that you upload the issuing CA cert (Name of cert = ACN-Issuing-CA-PR1.CER) from your CA server.
Another point we need to take care of is the destination store. We need to select the destination store as Computer Certificate Store—Intermediate. Click OK—Create to finish creating the Issuing cert profile.
Deploy Windows 10 Root CA and Intermediate/IssuingCA Certificate Profiles to the same group of Windows 10 devices. We can deploy these profiles using either an AAD user or device group. However, I would prefer to use AAD dynamic device groups wherever possible.
Create and Deploy Windows 10 SCEP Profile via Intune – Intune Create SCEP Certificate Profiles
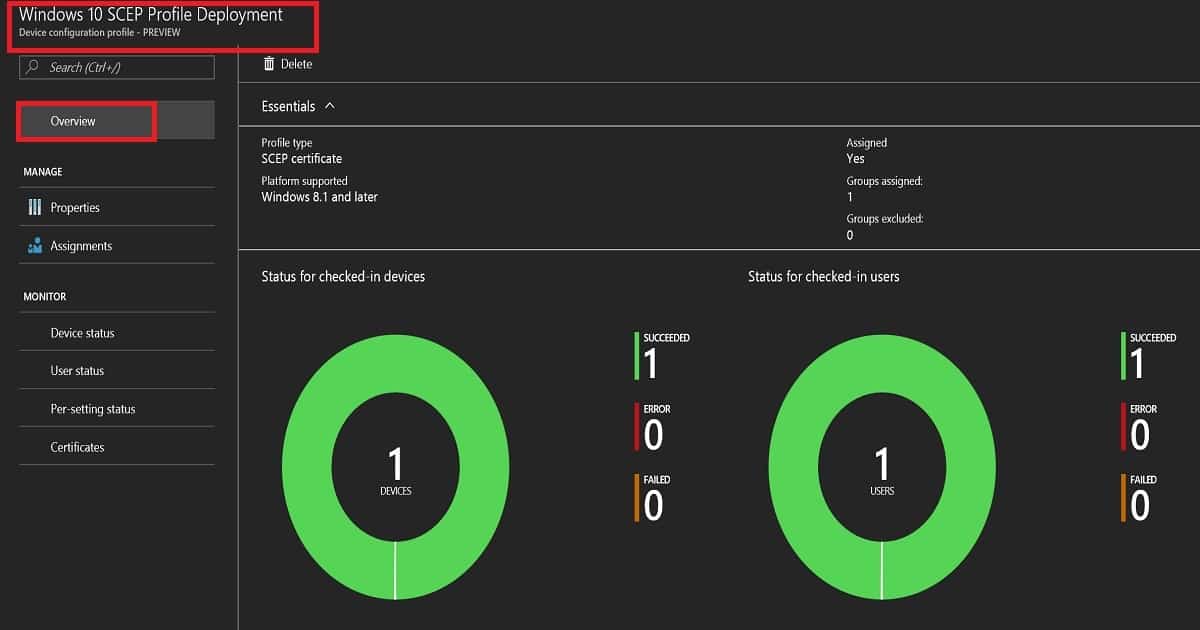
To create and deploy a SCEP profile on Windows 10 devices, navigate to Microsoft Intune—Device Configuration—Profiles—”Create a profile.” Select the platform as Windows 10 and the profile type as SCEP Certificate.
When you create a SCEP profile for a Windows 10 device, you need to make some specific settings. The load of these configurations can differ between the CA server setup and another on-prem component setup.
Create SCEP Certificate Profiles in Intune Deploy SCEP Profiles to Windows 10 Devices – Fig.3
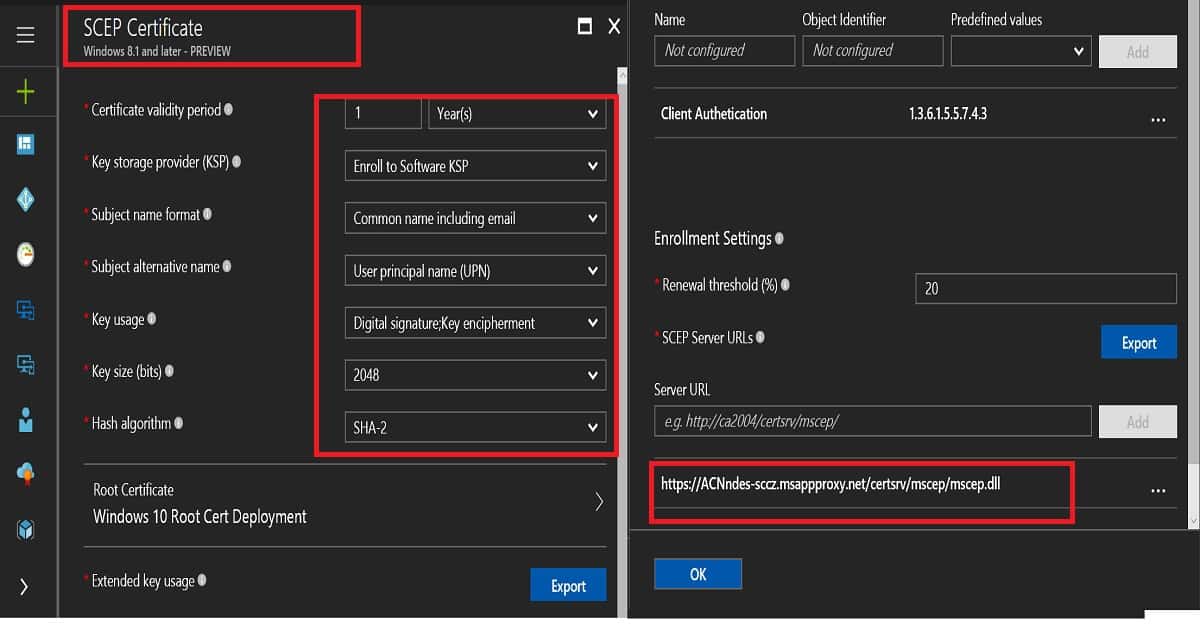
The certificate validity period is 1 year, which is the industry standard. There are four options for the Key storage provider (KSP): Enrol to trusted platform Module(TPM) KSP if present Software KSP, Enrol to Trusted platform module(TPM), otherwise fail, Enrol to passport, otherwise fail, and Enrol to Software KSP.
In this scenario, I have selected Enrol to Trusted Platform Module(TPM) KSP if the Software KSP is present. We must choose the subject name format value depending on your organizational requirement. In this scenario, I selected a familiar name as an email. The subject alternative name is UPN. Key usage is a digital signature and key encipherment. The key Size value is 2048. If your CA supports the same, the hash algorithm value (SHA-2) should be the latest one.
Another critical point is linking the SCEP profile with the ROOT cert profile you created. If you have not created any ROOT cert and intermediate/issuing CA cert profiles in Intune, it won’t allow you to create an SCEP profile. Extended key usage is another setting, and it should automatically get populated. One example here is “Client Authentication—1.3.6.1.5.5.7.4.3.”
Create SCEP Certificate Profiles in Intune Deploy SCEP Profiles to Windows 10 Devices – Fig.4
Enrollment Settings is the last set of settings for Windows 10 SCEP profiles in Intune. I recommend keeping the certificate renewal threshold at the default value of 20%. SCEP server URLs (e.g., https://acnndes-sccz.msappproxy.net/certsrv/mscep/mscep.dll) are very important. These are the URLs to which Windows 10 devices will go and request SCEP certs.
This should be reachable from the Internet. As I mentioned above, you can use Azure AD app proxy URLs. In this scenario, I will use Azure AD app proxy settings.
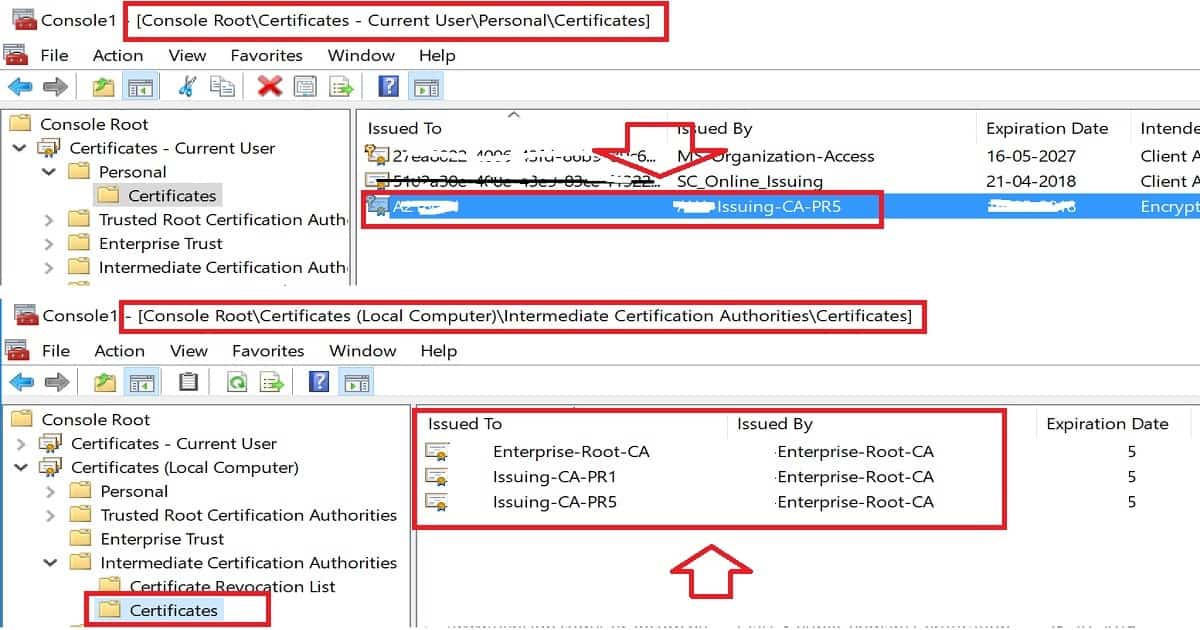
SCEP profile cert will be deployed to users’ stores in the format “ACN-Issuing-CA-PR5“.
End-User Windows 10 Certificate Store Experience – Intune Create SCEP Certificate Profiles
SCEP profile will be deployed to Current User\Personal\Certificates = “ACN-Issuing-CA-PR5“
Root and Intermediate CA cert will be deployed to Local Computer\Intermediate Certification Authorities\Certificates = ACN-Enterprise-Root-CA.CER and ACN-Issuing-CA-PR1.CER
Create SCEP Certificate Profiles in Intune Deploy SCEP Profiles to Windows 10 Devices – Fig.5
We are on WhatsApp now. To get the latest step-by-step guides, news, and updates, Join our Channel. Click here. HTMD WhatsApp.
Author
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC, He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC. He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.
Let’s discuss creating SCEP Certificate Profiles and Deploying them to iOS Devices using Intune. Before obtaining an SCEP certificate in Intune, we must consider some prerequisites.
It would be best if you also had on-prem infrastructure components available. NDES connector is supposed to be installed on your Data Center, and the NDES connector should be able to talk to the CA server and Azure AD App proxy connector if you are using the Azure app proxy.
In “Intune SCEP HTTP Errors Troubleshooting Made Easy With Joy – #5,” Joymalya Basu Roy provides a comprehensive guide on diagnosing and resolving HTTP errors encountered during SCEP (Simple Certificate Enrollment Protocol) certificate deployments using Microsoft Intune. The post focuses on various HTTP errors, particularly the HTTP 500 Internal Server Error, and offers detailed steps to effectively identify and troubleshoot these issues.
I won’t cover the setup of NDEs and Azure AD App proxyconnectors. Those two configurations are complex and well explained in loads of other blogs. This post will cover how to create and deploy a SCEP Profile for iOS Devices via Intune Blade in the Azure portal.
How to Create and Deploy SCEP Certificate with Intune for iOS Devices
Deployment of SCEP Certificates to iOS devices will help them connect to corporate Wi-Fi and VPN profiles, etc.… You must create and deploy the certificate chain before creating an iOS SCEP Certificate in Intune.
The certificate chain includes the Root CA and Intermediate/Issuing CA certificates. There are 3 certificate profiles available in Intune: the TRUSTED Certificate, the SCEP Certificate, and the PKCS certificate. We are not going to use the PKCS certificate for SCEP profile deployment.
Create SCEP Certificate Profiles Deploy SCEP Profiles to iOS Devices using Intune – Video 1
Introduction – Create SCEP Certificate Profiles Deploy SCEP Profiles to iOS Devices using Intune
Deploying a SCEP Certificate to iOS devices will help them connect to corporate Wi-Fi, VPN profiles, etc. Before creating an iOS SCEP Certificate in Intune, you need to develop and deploy a certificate chain. The certificate chain includes the Root CA and Intermediate/Issuing CA certificates.
There are 3 certificate profiles available in Intune: TRUSTED Certificate, SCEP Certificate, and PKCS certificate. We are not going to use the PKCS certificate for SCEP profile deployment. The following is the high-level task list for deploying SCEP Profile to iOS Devices (Deploy SCEP profiles to iOS Devices).
Create SCEP Certificate Profiles Deploy SCEP Profiles to iOS Devices using Intune
Create and Deploy iOS Root CA certificate using Intune Azure Portal
Or Create and Deploy an iOS Intermediate CA certificate using Intune Azure Portal
Create and Deploy SCEP Certificate to iOS Devices using Intune Azure Portal
Create SCEP Certificate Profiles Deploy SCEP Profiles to iOS Devices using Intune – Table 1
Create SCEP Certificate Profiles Deploy SCEP Profiles to iOS Devices using Intune – Fig.1
Create and Deploy iOS Root CA, iOS Intermediate/Issuing CA Certificate Profiles
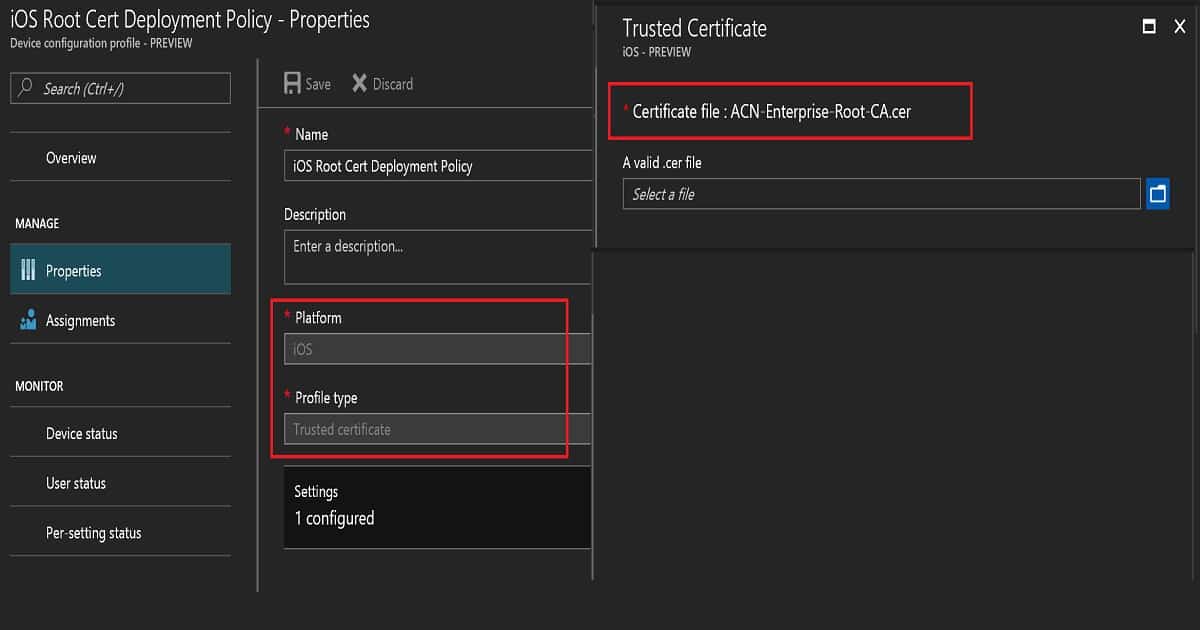
As the first step, we need to create a Root CA cert profile. To create a Root CA cert, navigate through Microsoft Intune—Device Configuration—Profiles—Create a profile (Deploy SCEP profiles to iOS Devices). Select the platform iOS and profile type Trusted Certificate. You must browse and upload your ROOT CA cert (Name of the cert = ACN-Enterprise-Root-CA.CER) from your CA server.
Once settings are saved, you must deploy the root cert profile to the required iOS devices. The exact process must follow for Intermediate/Issuing CA certificate profile deployment via Intune. Intune Create SCEP Certificate Profiles Deploy SCEP profiles to iOS Devices using Intune.
Make sure that you are uploading the issuing CA cert (Name of cert = ACN-Issuing-CA-PR1.CER) from your CA server. The video above explains all these configurations; you can watch them here.
Create and Deploy iOS SCEP Certificate Profile for iOS Devices
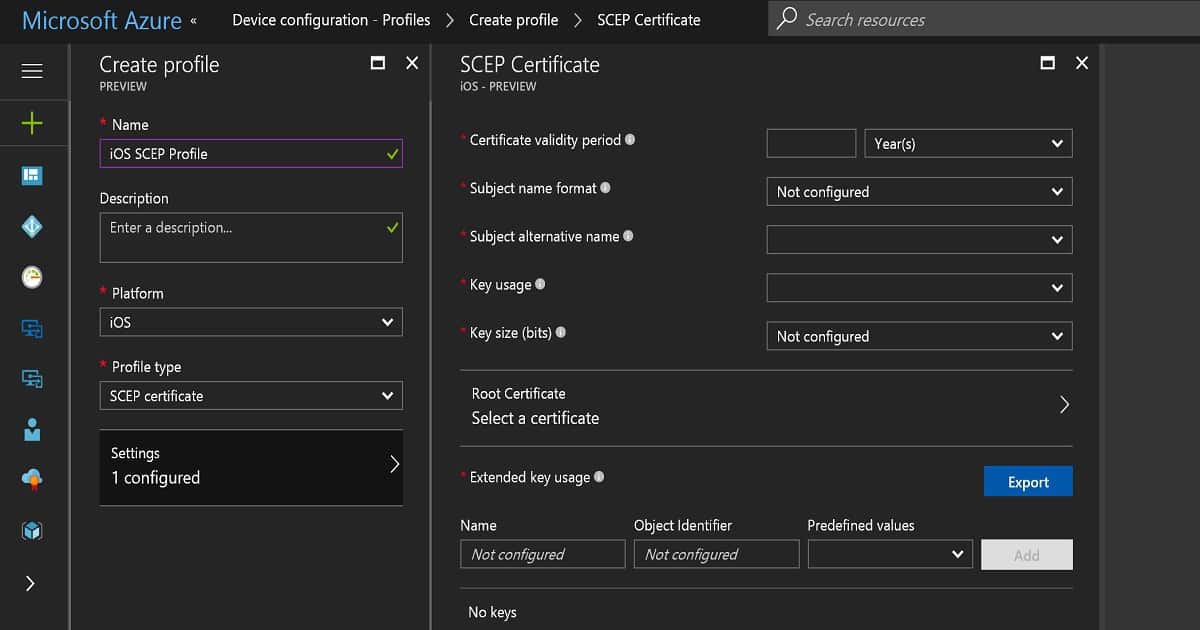
To create a SCEP certificate profile, navigate to Microsoft Intune – Device Configuration – Profiles – Create a profile. While making an iOS SCEP Certificate, we must select the Profile type as “SCEP certificate” and the platform as iOS.
The next step is configuring the settings. These settings are critical, and we need to consult with your CA team when you create a SCEP Certificate. Loads of these configurations can differ between the CA server setup and another on-prem component setup (Deploy SCEP profiles to iOS Devices).
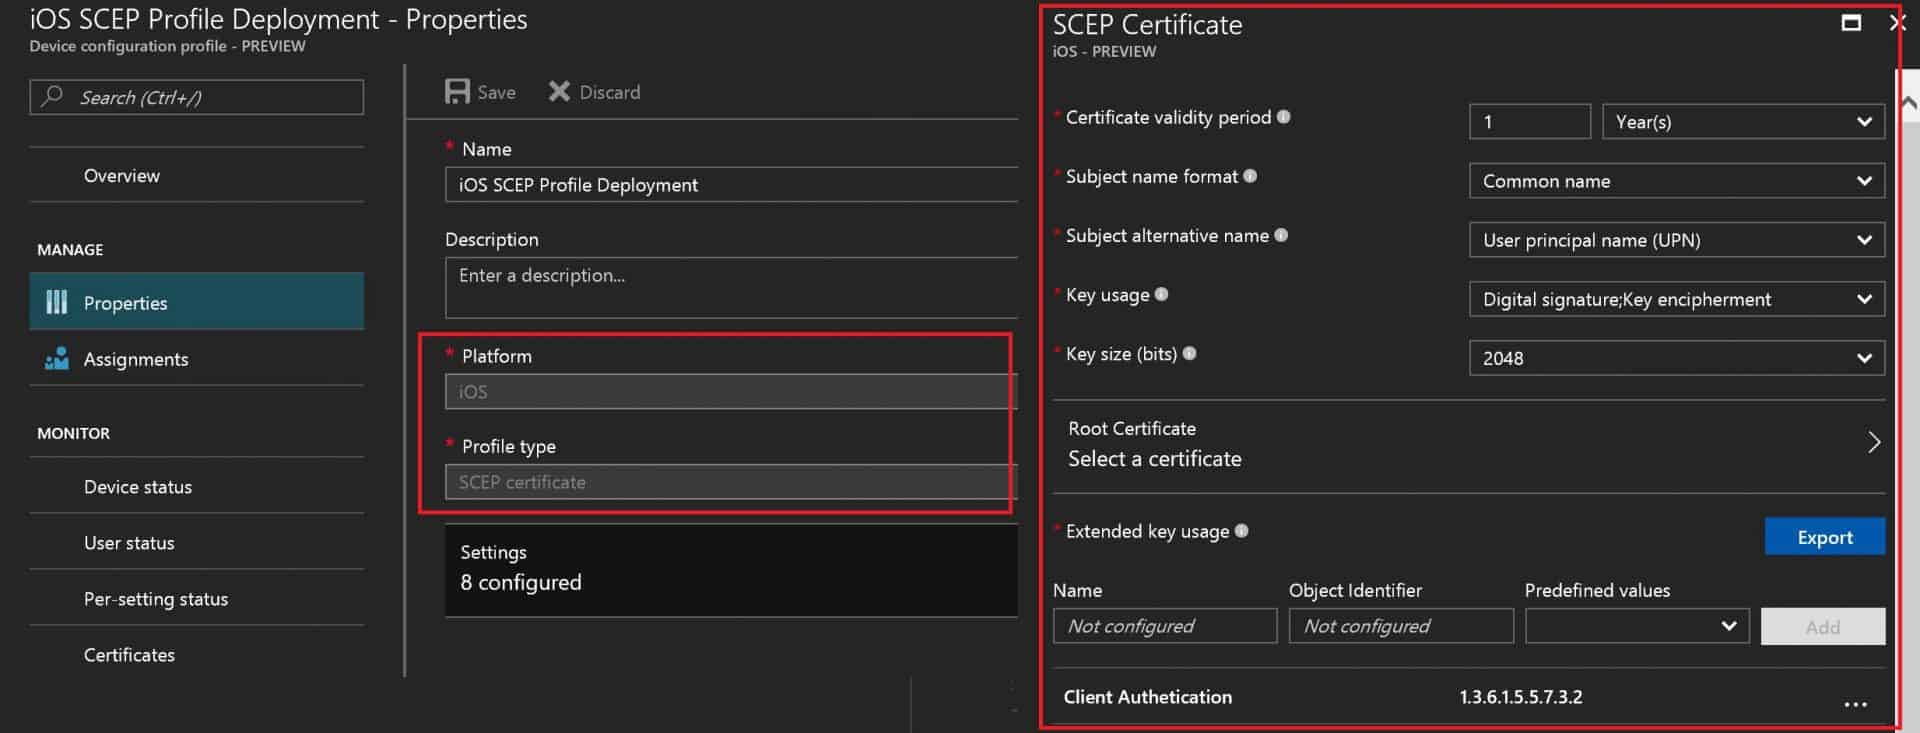
The certificate validity period is 1 year, which is the industry standard. The subject name format also depends on your organization’s preference. In this scenario, I selected a familiar name as email and a subject alternative name as UPN. The key usage is a digital signature and critical decipherment. The key Size is 2048.
Another critical point is linking the SCEP Certificate with the ROOT cert profile you created. If you have not earned any ROOT certification in Intune, you won’t be able to develop an SCEP Certificate. Extended key usage is another setting, and it should automatically get populated.
One example here is Client Authentication – 1.3.6.1.5.5.7.4.3. Intune Create SCEP Certificate Profiles Deploy SCEP profiles to iOS Devices using Intune.
Create SCEP Certificate Profiles Deploy SCEP Profiles to iOS Devices using Intune – Fig.2
Enrollment Settings is the last set of settings for iOS SCEP profiles in Intune. I recommend keeping the renewal threshold of certificates as the default value of 20%. SCEP server URLs are critical. These are the URLs to which iOS devices will request SCEP certifications.
So, this should be reachable from the Internet. As mentioned above, you can use Azure AD App proxy URLs here (e.g., https://acnndes-sccz.msappproxy.net/certsrv/mscep/mscep.dll ). In this scenario, I will use Azure AD App proxy settings. All these configuration details are explained in the video here.
SCEP certificate will be in the following format: “ACN-Issuing-CA-PR5“.
We are on WhatsApp now. To get the latest step-by-step guides, news, and updates, Join our Channel. Click here. HTMD WhatsApp.
Author
Anoop C Nair is Microsoft MVP! He is a Device Management Admin with more than 20 years of experience (calculation done in 2021) in IT. He is a Blogger, Speaker, and Local User Group HTMD Community leader. His primary focus is Device Management technologies like SCCM 2012, Current Branch, and Intune. He writes about ConfigMgr, Windows 11, Windows 10, Azure AD, Microsoft Intune, Windows 365, AVD, etc.
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC. He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.
Secure Android Enterprise devices with Device Restrictions policies.
Protect corporate data by controlling device features and settings.
Restrict data sharing between work and personal profiles.
Manage work profile behavior to improve security.
Let’s learn Configure Password Policies for Android Enterprise Work Profile using Intune. Android for Work Device Restriction Policies Deployment is the Security Policy for Android Devices. Security policies are important to secure the corporate data and applications on those devices. Microsoft Intune provides Device Restrictions policies to help organizations secure Android Enterprisedevices by controlling device features and restricting user actions.
Table of Contents
Table of Contents
Configure Password Policies for Android Enterprise Work Profile using Intune
In this guide, you’ll learn how to create and deploy an Android Enterprise Device Restrictions policy using the Microsoft Intune admin center. We’ll walk through the policy creation process, configure the available restriction settings, and assign the policy to Microsoft Entra ID groups.
By implementing Device Restrictions policies, administrators can control work profile behavior, limit data sharing, manage hardware features, and enhance the overall security of Android Enterprise devices. Following these best practices helps organizations maintain a secure and compliant mobile environment.
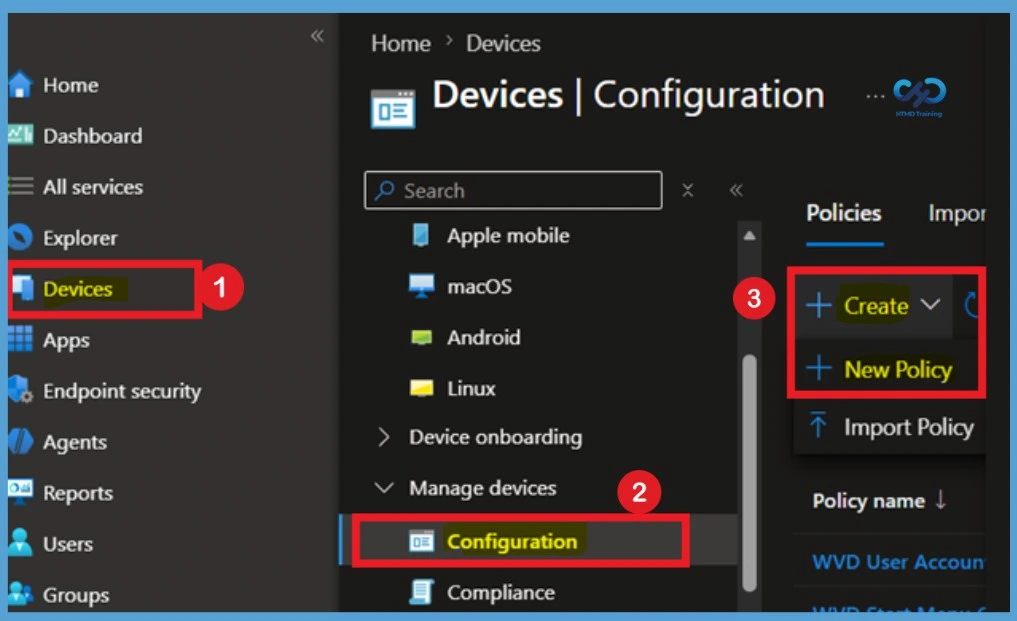
To begin, sign in to theMicrosoft Intune admin centerwith an account that has the required administrative permissions. From the left navigation pane, select Devices, and then click Configuration to access the list of device configuration policies.
On the Configuration page, click + Create, and then select + New policy.
Configure Password Policies for Android Enterprise Work Profile using Intune – Fig.1
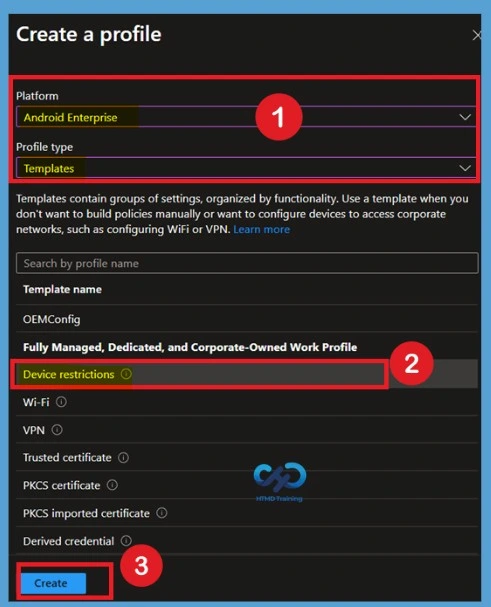
When you select + New policy, the Create a profile window opens. Here, choose Android Enterprise as the Platform, Templates as the Profile type, and then select Device restrictions from the list of available templates. Templates provide a preconfigured collection of settings organized by functionality, making it easier to create policies without manually selecting individual settings.
They help administrators quickly configure common device management and security settings for managed devices. After selecting Device restrictions, click Create to begin configuring the policy.
Platform
Profile Type
Android Enterprise
Device Restrictions
Configure Password Policies for Android Enterprise Work Profile using Intune – Table 1
Configure Password Policies for Android Enterprise Work Profile using Intune – Fig.2
Basic Tab
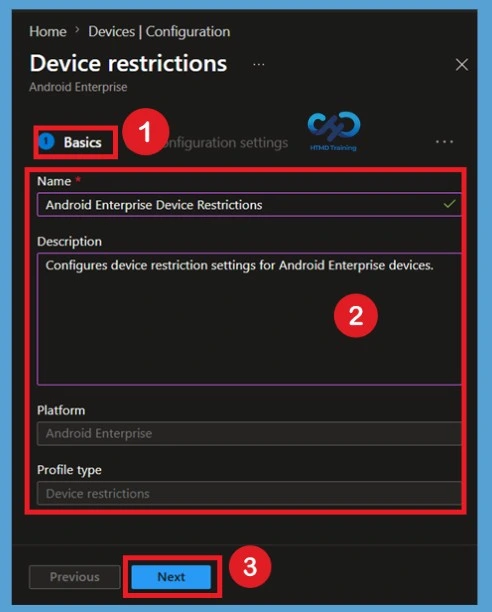
On the Basics page, provide a meaningful Name and an optional Description for the Device Restrictions policy. Using a descriptive policy name makes it easier to identify and manage the policy in the Microsoft Intune admin center, especially when multiple configuration profiles are deployed.
For this example, enter Android Enterprise Device Restrictions as the policy name and Configures device restriction settings for Android Enterprise devices as the description. Verify that the Platform is set to Android Enterprise and the Profile type is Device restrictions, then click Next to continue.
Configure Password Policies for Android Enterprise Work Profile using Intune – Fig.3
Configuration Settings
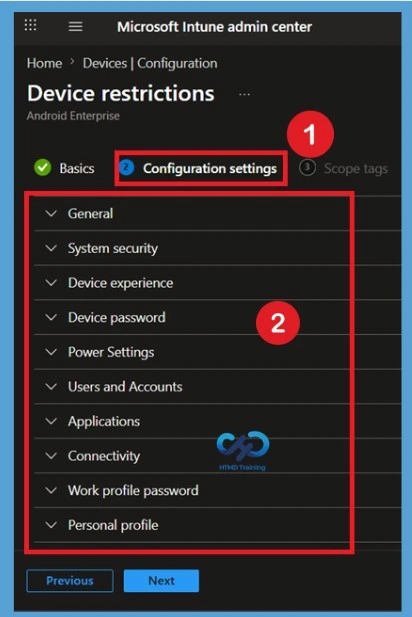
On the Configuration settings page, you’ll find several categories of device restriction settings, including General, System security, Device experience, Device password, Power Settings, Users and Accounts, Applications, Connectivity, Work profile password, and Personal profile. These categories allow you to configure security and device management settings based on your organization’s requirements.
Category
Purpose
General
Controls core device behaviors such as screen capture, camera access, date or time changes, and roaming data
System security
Defines encryption, certificate, and security patch requirements. Strengthens device integrity and compliance.
Device experience
Manages user interface and experience settings like status bar visibility, notifications, and accessibility features. Ideal for kiosk or frontline devices.
Power Settings
Controls power menu access, sleep behavior, and battery optimization. Prevents unauthorized shutdowns or tampering.
Users and Accounts
Restricts account additions, sync settings, and user management.
Applications
Manages app installation permissions, updates, and restrictions. Supports app whitelisting or blacklisting for compliance.
Connectivity
Controls Bluetooth, Wi‑Fi, USB, and hotspot access. Prevents data leakage and enforces secure network usage.
Work profile password
Enforces password rules specifically for corporate‑owned work profiles, expiry, and wipe thresholds. Protects enterprise data within work containers.
Personal profile
Control camera, screen capture, and app installation from unknown sources. Balances privacy and control.
Custom support information
Displays IT helpdesk contact or support portal details on the device. Improves user self‑service and compliance.
Configure Password Policies for Android Enterprise Work Profile using Intune – Table.2
Configure Password Policies for Android Enterprise Work Profile using Intune – Fig.4
Configure Work Profile Device Restriction Settings
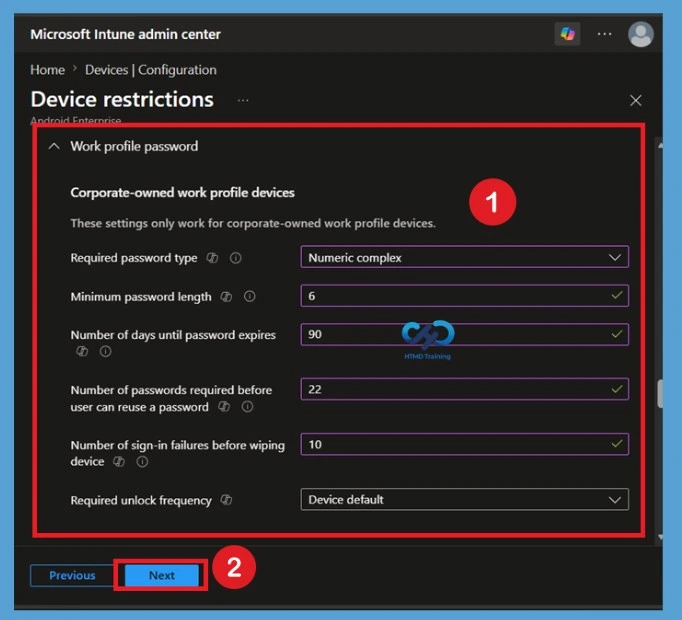
Expand the required category to configure its available settings. In this example, the Work profile password section is used to define password requirements for corporate-owned work profile devices, including the required password type, minimum password length, password expiration period, password history, sign-in failure threshold, and unlock frequency.
Expand each category and configure the appropriate settings for your Android Enterprise devices.
Review the configured options carefully before proceeding. After completing the required configurations, click Next to continue to the next step.
Setting
Info
Required password type
Numeric complex
Minimum password length
6
Number of days until password expires
90
Number of passwords required before reuse
22
Number of sign‑in failures before wiping device
10
Required unlock frequency
Device default
Configure Password Policies for Android Enterprise Work Profile using Intune – Table 3
Configure Password Policies for Android Enterprise Work Profile using Intune – Fig.5
Scope Tags Settings
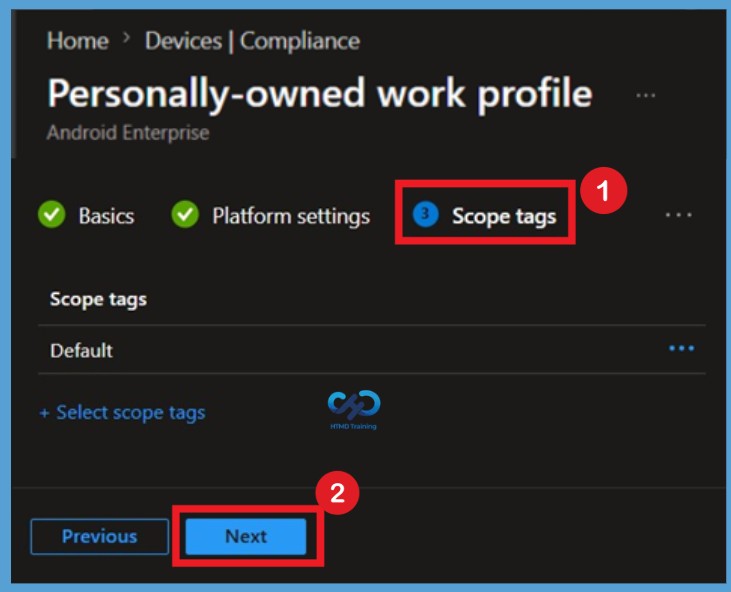
Scope tags help limit which administrators can view and manage this Device Restrictions policy based on their assigned roles. Click Select scope tags to choose one or more scope tags, or leave the default configuration if your organization doesn’t use RBAC. After completing this step, click Next to continue.
Configure Password Policies for Android Enterprise Work Profile using Intune – Fig.6
Importance of Assignments
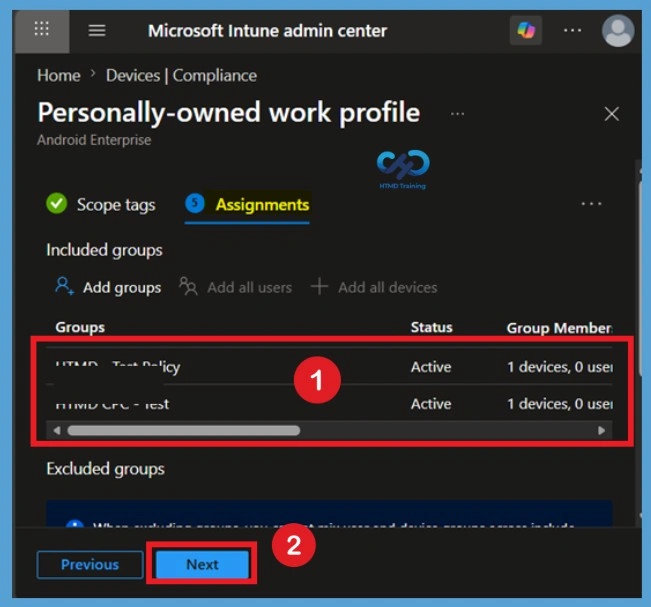
The Assignments page determines which users or devices receive the Android Enterprise Device Restrictions policy. Under Included groups, click Add groups and select the Microsoft Entra ID user or device groups that should receive the policy. If necessary, you can also configure Excluded groups to prevent the policy from applying to specific users or devices.
After selecting the appropriate groups, review the assignment configuration and click Next.
Configure Password Policies for Android Enterprise Work Profile using Intune – Fig.7
Review + Create Options
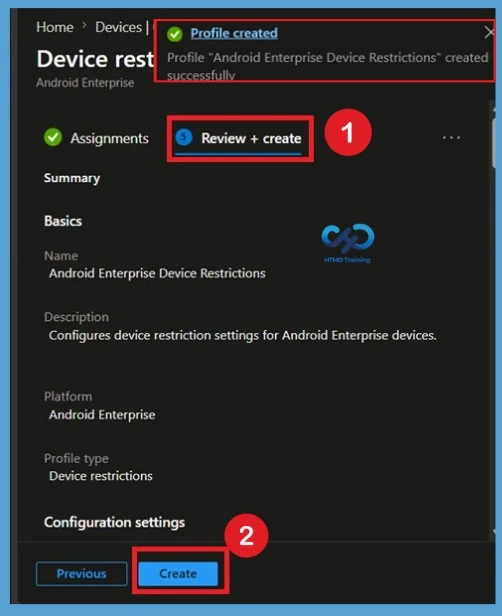
The Review + create page displays a summary of the policy configuration, including the platform, profile template, configured device restriction settings, scope tags, and assignments. Carefully review all settings to ensure they match your organization’s security requirements before creating the policy.
If you need to make any changes, click Previous to return to the relevant step. When you’re satisfied with the configuration, click Create to deploy the Android Enterprise Device Restrictions policy.
Configure Password Policies for Android Enterprise Work Profile using Intune – Fig.8
Monitor Device Restrictions Policy Deployment Status
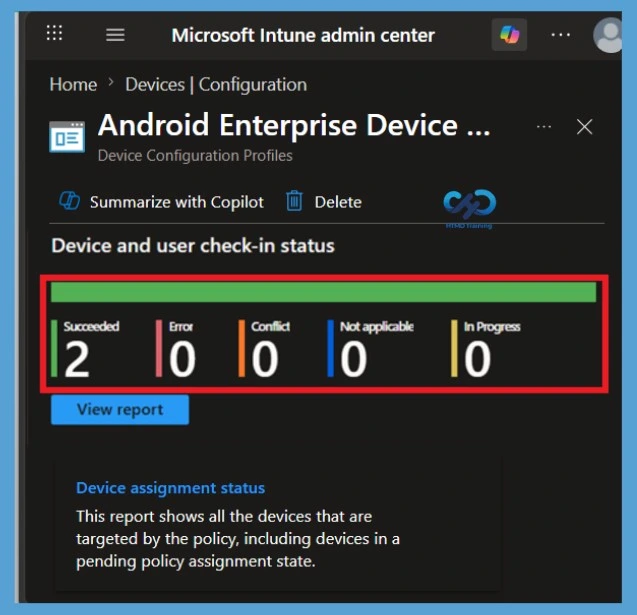
After creating the Android Enterprise Device Restrictions policy, you can monitor its deployment status from the Microsoft Intune admin center. Navigate to Devices > Configuration, and then select the Android Enterprise Device Restrictions policy you created.
Open the Device and user check-in status or Overview page to review the deployment results. Here, you can verify whether the policy was successfully applied to the targeted devices and identify any devices with Pending, Error, Conflict, or Not applicable statuses. This information helps troubleshoot deployment issues and confirm that the policy is being enforced correctly.
Configure Password Policies for Android Enterprise Work Profile using Intune – Fig.9
Delete the Device Restrictions Policy
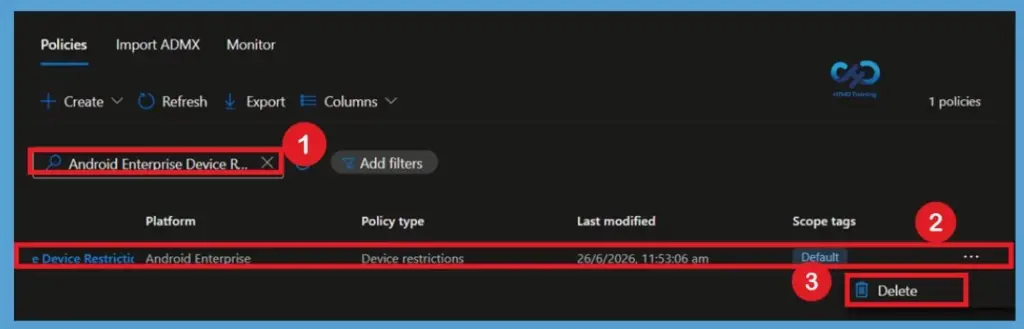
If the Device Restrictions policy is no longer required, you can permanently delete it from Microsoft Intune. Go to Devices > Configuration, locate the Android Enterprise Device Restrictions policy, and select it.
Click the 3-dot (More) menu or Delete option from the command bar, and then confirm the deletion when prompted. Once deleted, the policy is permanently removed from Intune and will no longer be applied to managed Android Enterprise devices.
Configure Password Policies for Android Enterprise Work Profile using Intune – Fig.10
Remove Assigned Groups from the Device Restrictions Policy
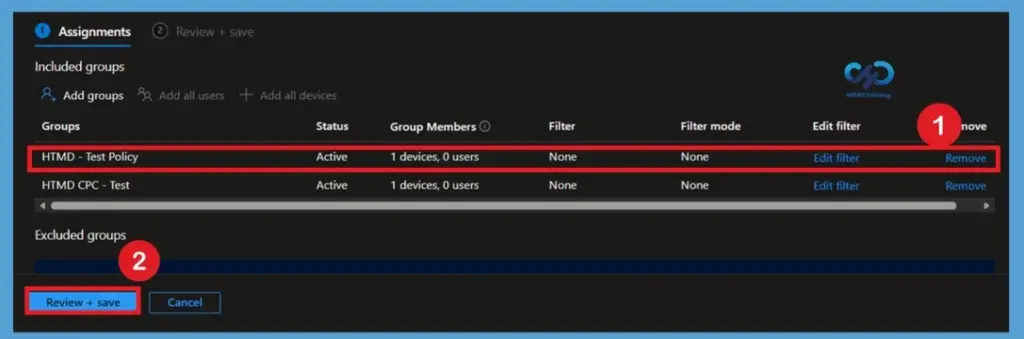
If you no longer want the Device Restrictions policy to apply to specific users or devices, you can remove the assigned groups from the policy. Open the policy, select Properties, and click Edit next to Assignments.
Under Included groups, remove the Microsoft Entra ID groups that are currently assigned to the policy. Review the updated assignments and click Review + save, After the policy is updated, it will no longer be deployed to the removed groups.
Configure Password Policies for Android Enterprise Work Profile using Intune – Fig.11
User Experience of Security Policy for Android Devices
The user experience of Android for Work devices can vary depending on the manufacturer of the devices. As mentioned in the previous post, Samsung and Nexus are the best-experienced devices I have tested.
But I would admit the user experience of Android for Work is far better than that of an Android device! As Android devices have different variants, it’s better to ensure that all the security policies for the Android device experience are excellent for all manufacturers.
Configure Password Policies for Android Enterprise Work Profile using Intune – Video 1
Need Further Assistance or Have Technical Questions?
Anoop C Nair has been Microsoft MVP from 2015 onwards for 10 consecutive years! He is a Workplace Solution Architect with more than 22+ years of experience in Workplace technologies. He is also a Blogger, Speaker, and Local User Group Community leader. His primary focus is on Device Management technologies like SCCM and Intune. He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security, Career, etc.
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC. He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.
Let’s discuss the Intune Create Device Restriction Policy Profiles Deploy Security Policies to Windows 10 Devices. Intune configuration restriction policies are critical in modern device management strategy. Intune device restriction policy is the security settings applied on your Windows 10 CYOD device.
As part of your organization’s security policies, you may need to lock down mobile or Windows devices with corporate data and app access. Yes, Intune configuration restriction policies help you lock down Windows devices as per your organization’s security requirements.
In this post, you will learn everything you need to createdevice restriction policy profiles in Intune and deploy security policies to Windows 10 devices. We will guide you step-by-step through setting up these policies to ensure your devices are secure and comply with your organization’s requirements.
Whether you’re new to Intune or looking to enhance your device management skills, this guide will provide clear and straightforward instructions to help you effectively manage and protect your Windows 10 devices.
Intune Configuration Restriction Policy Deployment with Windows 10
In this video, you’ll learn all about deploying Intune Configuration Restriction Policies on Windows 10. We’ll show you each process step, making it easy to follow. Whether setting up new policies or adjusting existing ones, this video will help you understand how to use Intune to keep your Windows 10 devices secure and well-managed.
Intune Create Device Restriction Policy Profiles Deploy Security Policies to Windows 10 Devices – Video 1
Create Intune Device Restriction Policy for Windows 10 Devices
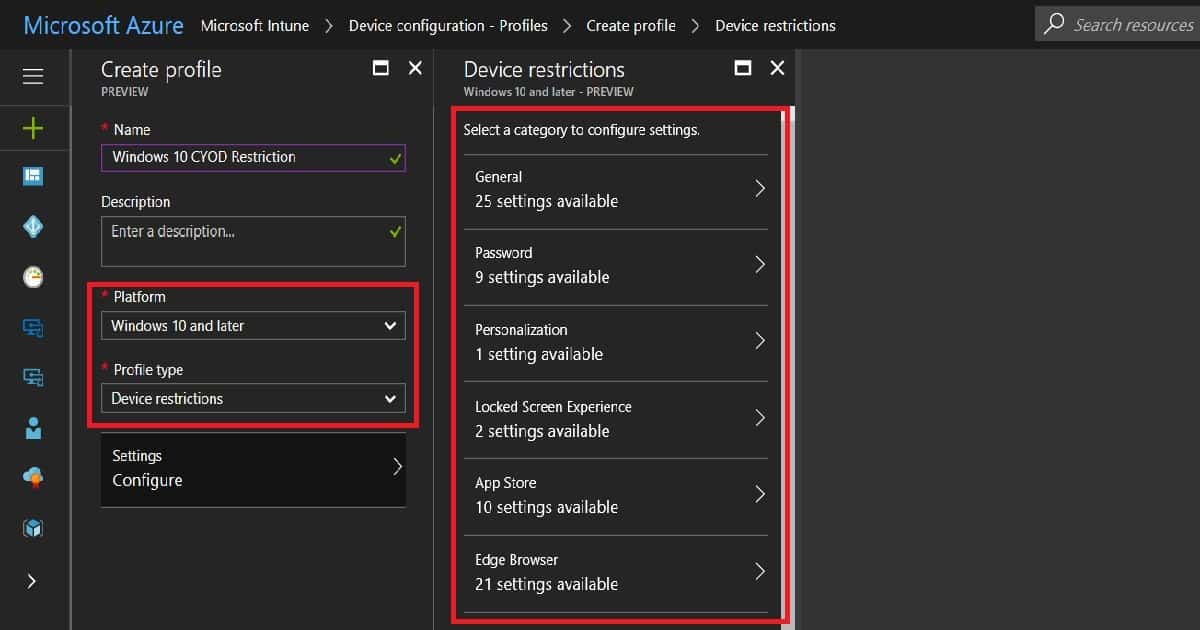
You can create an Intune device restriction policy for Windows 10 from Microsoft Intune—Device Configuration—Profiles—Create New Profile. I selected Windows 10 as the platform, and platform Selection is essential.
Also, it would be best to select the profile type while creating an Intune Configuration Restriction policy. In my scenario, the Device restriction policy is named “Windows 10 CYOD Restrictions.”
Platform
Profile Type
Windows 10 and Later
Device Restrictions
Intune Create Device Restriction Policy Profiles Deploy Security Policies to Windows 10 Devices – Table 1
Intune Create Device Restriction Policy Profiles Deploy Security Policies to Windows 10 Devices – Fig.1
As shown below, the Windows platform Intune device restriction policy for out-of-box settings is segregated into 16 sections. This list is comprehensive, and we can lock down Windows 10 machines as required.
Is this Intune device restriction policy a replacement for group policies? No, it’s still not a replacement for AD group policies.
General
Password
Personalization
Locked screen experience
App Store
Edge Browser
Search
Cloud and Storage
Cellular and Connectivity
Control Panel and Settings
Defender
Defender Exclusions
Network Proxy
Windows Spotlight
Display
Start
Deploy Windows 10 Intune Device Restriction Policy
You can deploy the Windows 10 Intune Device Restriction Policy to either Windows 10 CYOD dynamic devices or Windows 10 user groups. Dynamic device groups are still in preview, and the group typos are not always stable. So, at least for the next two months, I will prefer to deploy policies to user groups rather than dynamic device groups.
Windows 10 End-user Experience of Intune Device Restriction Policy
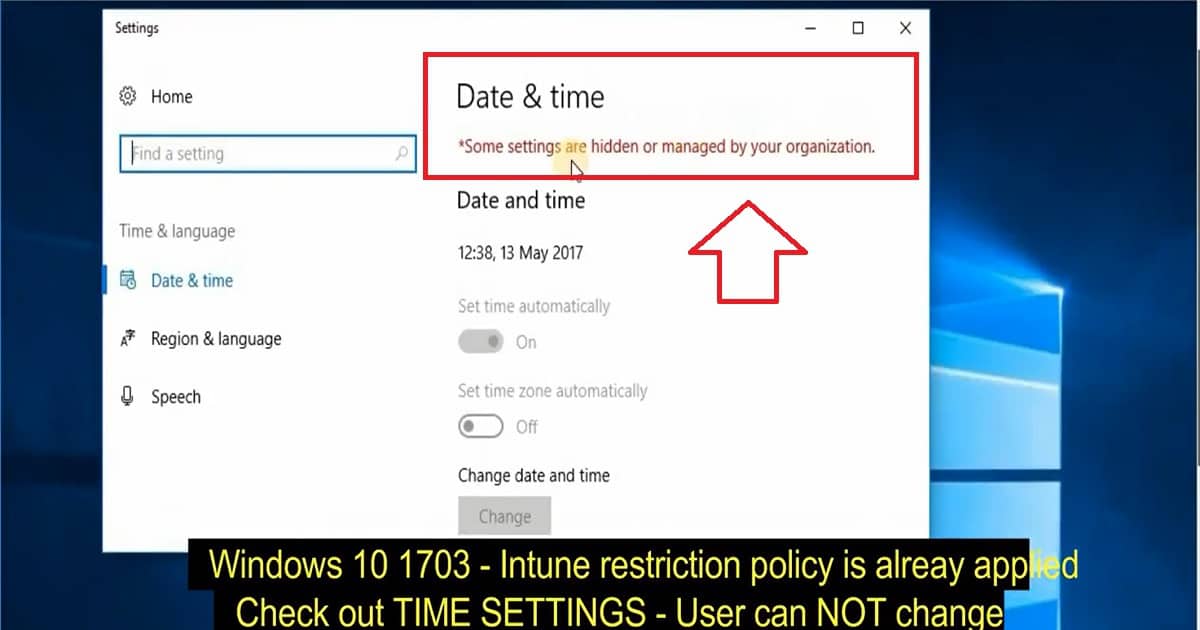
As you can see in the video tutorial at the top of this post, I’ve enabled the time settings to disable the option as part of the initial Windows 10 device restriction policy. The end-user logged in to the Windows 10 machine can’t change the time on the system.
After that, I changed the Windows time setting policy again, and after applying the new policy, the user can change the time on the Windows 10 system.
Intune Create Device Restriction Policy Profiles Deploy Security Policies to Windows 10 Devices – Fig.2
We are on WhatsApp now. To get the latest step-by-step guides, news, and updates, Join our Channel. Click here. HTMD WhatsApp.
Author
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC, He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC. He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.
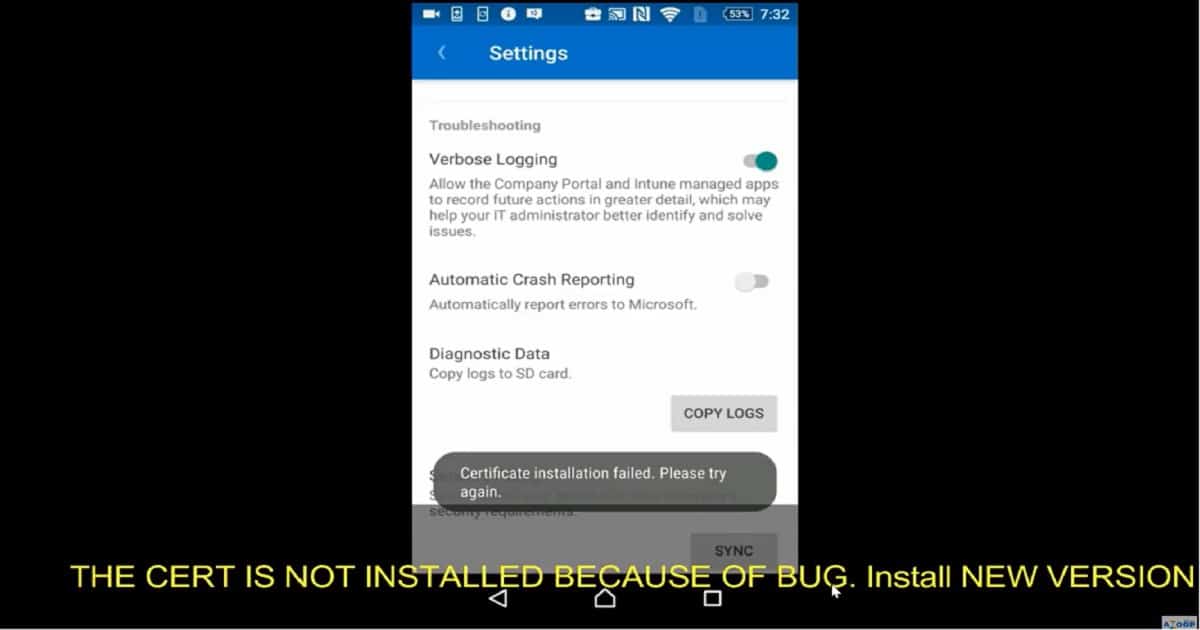
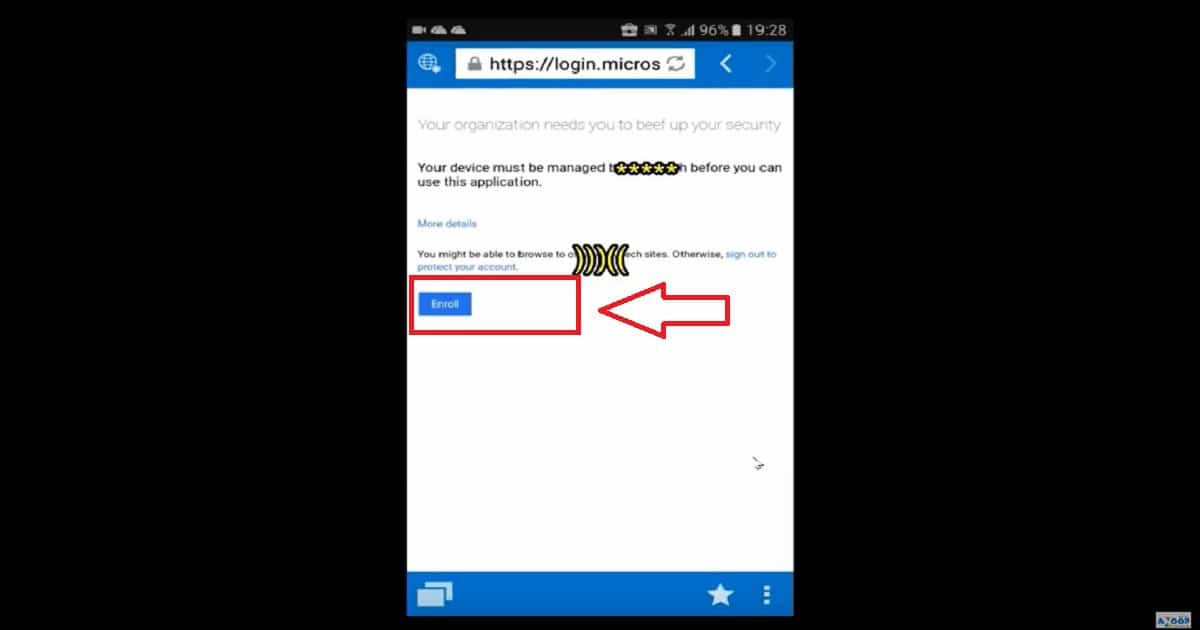
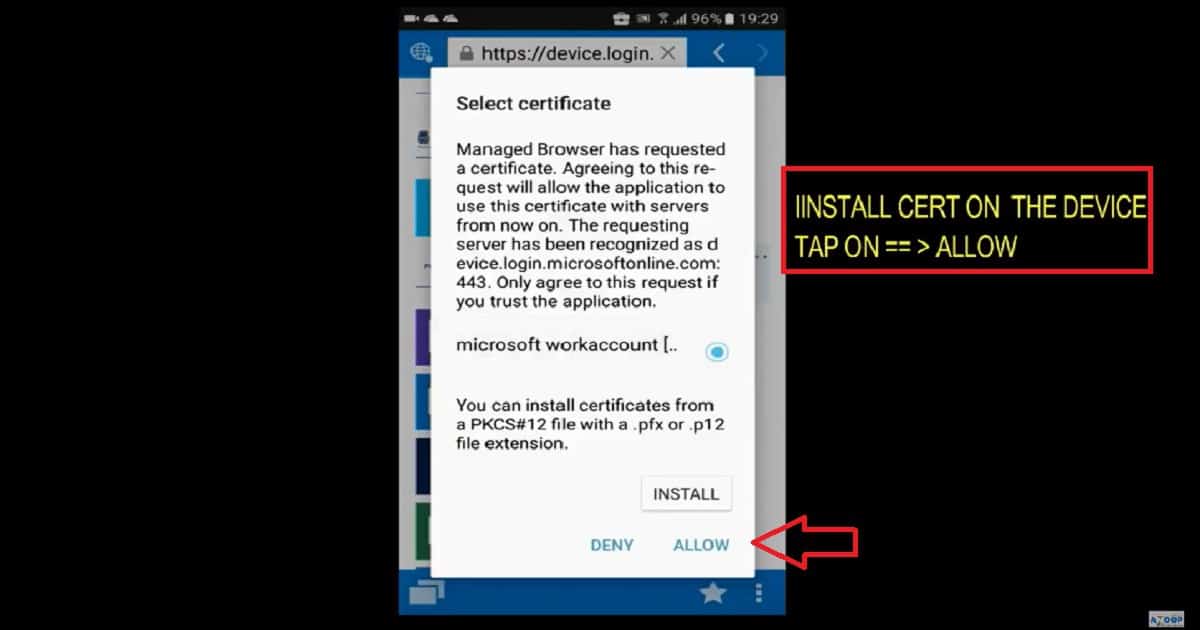
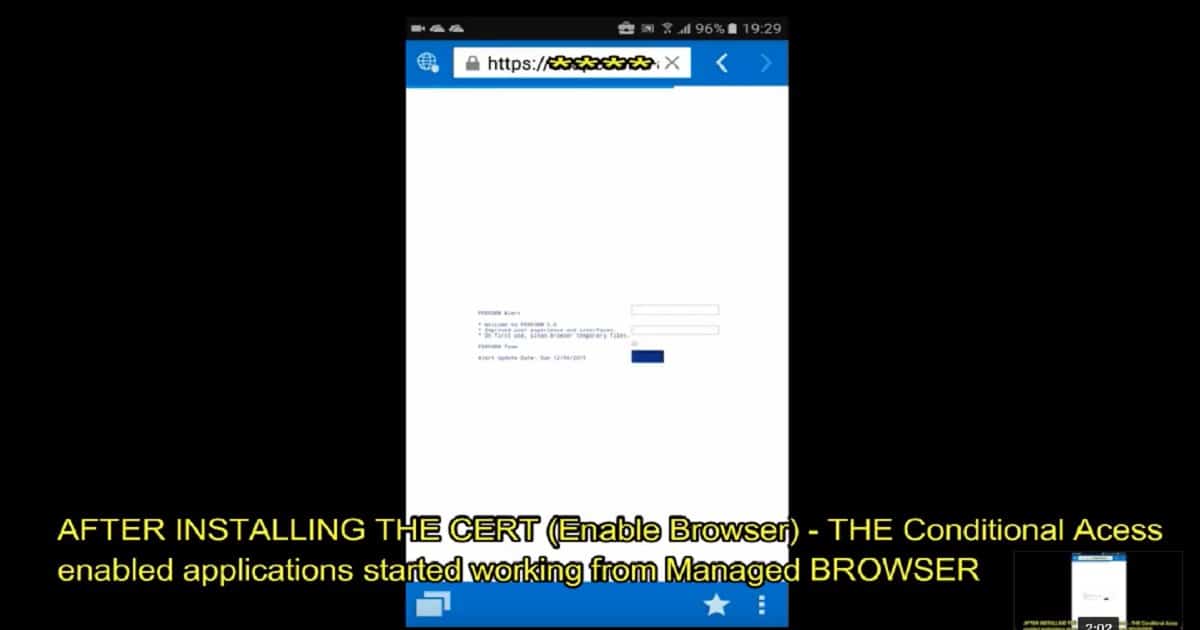
Let’s discuss how to Enable Intune Company Portal Browser Access for Conditional Access Enabled Web apps. I have been testing and developing a solution for Android device management with Intune. I have shared my Android for Work learning experiences in my previous posts – Android.
In this post, we will see and learn how to enable Intune Company Portal Browser Access for Android devices. What is the need for enabling company portal browser access?.
To put it in simple words, if your organization is using Azure AD Conditional Access (CA) enabled internal web applications, then we need to enable the Company portal browser access option.
This post will provide a comprehensive guide on enabling Intune Company Portal browser access for conditional access-enabled web apps. We will walk you through the necessary steps to configure your settings, ensuring easy access control and security compliance.
How to Enable Intune Company Portal Browser Access
The above video recording gives you the same user experience when you have CA access-enabled web applications and you have not enabled company portal browser access. As you can see in the video, the managed browser for Android devices gives an error stating that the device is not enrolled.
Yes, the managed browser application can’t understand whether the device is already enrolled. When you perform an action like “Intune Company Portal Browser Access, ” the app will try to install the Microsoft work account certificate on an Android device. There is a known issue with the previous version of the Company Portal application on Android devices.
How to Enable Intune Company Portal Browser Access
Open the Company Portal app.
Go to the Settings page from the ellipsis (…) or hardware menu button.
Press the Enable Browser Access button.
How to Enable Intune Company Portal Browser Access for Conditional Access Enabled Web Apps – Table 1
Microsoft Work Account Certificate Installation Error
Allow the Company portal and Intune-managed apps to record future actions in greater detail, which may help your IT administrator better identify and solve issues.
How to Enable Intune Company Portal Browser Access for Conditional Access Enabled Web Apps – Fig.1
End-User Experience of ENROLL Device Error
The solution to the Microsoft mentioned above “work account certificate installation” error is to update the company portal application for Android devices. Are you getting an ENROL error on your device (as you can see in the following screen capture)?
Does this error appear when you try to access Conditional Access-enabled web applications through the managed browser? The web apps without CA are working fine? If so, you must perform the following action from your Android device: “Intune Company Portal Browser Access.”
How to Enable Intune Company Portal Browser Access for Conditional Access Enabled Web Apps – Fig.2
Microsoft Work Account Certificate Installation
Now, it’s time to update the company portal application on Android for work-enabled devices. Once the device is updated with the latest version of the company portal app, then open up the company portal app and go to settings – tap on the button “Enable Browser Settings.”
This action opens a popup for installing a Microsoft Work Account certificate. The user must select the cert and tap on the ALLOW button. The video tutorial at the top of this post explains this process.
How to Enable Intune Company Portal Browser Access for Conditional Access Enabled Web Apps – Fig.3
End USER Experience of CA-enabled Web Application Access
Once the managed browser has a certificate, the web applications opened in the Managed browser can use the Microsoft Work account cert. This will allow the managed browser to securely open conditional access-enabled internal web applications. In my experience, the user doesn’t require a tap on the INSTALL button; rather, the user must tap on the ALLOW button to complete this configuration.
How to Enable Intune Company Portal Browser Access for Conditional Access Enabled Web Apps – Fig.4
We are on WhatsApp now. To get the latest step-by-step guides, news, and updates, Join our Channel. Click here. HTMD WhatsApp.
Author
Anoop C Nair is Microsoft MVP! He is a Device Management Admin with over 20 years of IT experience (calculation done in 2021). He is a Blogger, Speaker, and leader of the Local User Group HTMD Community. His main focus is on Device Management technologies like SCCM 2012, Current Branch, and Intune. He writes about ConfigMgr, Windows 11, Windows 10, Azure AD, Microsoft Intune, Windows 365, AVD, etc.
Anoop C Nair is Workplace Technology solution architect with 25+ years of experience in global enterprise organizations such as JP Morgan, Capgemini, etc. He is Microsoft Certified Trainer. Microsoft MVP from 2015 onwards for consecutive 11 years! He also conducts Intune and modern workplace tech training for enterprise organizations. He is Blogger, Speaker, and Founder of HTMD Community and HTMD Conference. His focus is on Device Management technologies such as Intune, Windows, Cloud PC. He writes about technologies like Intune, SCCM, Windows, Cloud PC, Windows, Entra, Microsoft Security.
Let’s discuss how to Deploy Microsoft Store for Business Apps using Intune. Microsoft Store for business apps is part of your organization’s private store apps.
Only one way to deploy Store apps using Intune is required deployment. Microsoft Store for business apps can be deployed as “Available,” “Required,” or “Uninstall” apps to Windows 10 or Windows 11 devices.
On September 15, 2023, Microsoft Store for Business and Education apps will be removed from the Intune admin center. Apps on the device will remain until intentionally removed.
How to Deploy Microsoft Store for Business Apps using Intune – Fig.1
The logic behind NOT having an “available” deployment option is very understandable. The user doesn’t need an available deployment via Intune because the user always has private store access to install the apps manually.
Let’s check how to deploy the WhatsApp application from the Microsoft store to Windows 10/11 devices, which Microsoft Intune manages.
Devices must be registered with Azure AD or joined to the same Azure AD tenant where you registered the MSfB for online app deployment.
Azure AD Global admin (or appropriate) access to create Applications to connect ConfigMgr site to Azure AD and MSfB
Decide Offline or Online Applicationsusing Intune
The MSfB supports two types of application licenses, and you should be very careful with the license type of application you want to add. You don’t need devices Hybrid Azure AD registered or joined for Offline apps.
Online: Windows 10 devices must be joined to Azure Active Directory (Azure AD) or hybrid Azure AD-joined.
Offline: Devices don’t need to connect to the store or have a connection to the internet.
Search Store Applications from MSfB for Intune App Deployment
Let’s log in to the Microsoft Store for Business and search for the apps you want to add to Configuration Manager. Try to add WhatsApp to the private store and deploy it to managed Intune Windows 10/11 devices.
NOTE! – Microsoft Store for Business will retire in the first quarter 2023.
How to Deploy Microsoft Store for Business Apps using Intune – Fig.2
Add Apps to Private Store
You have already found the required app (above section): WhatsApp. Now, let’s add it to the organization’s private store.
Click on any application – WhatsApp
Select License type: Offline
Click on Get the app
How to Deploy Microsoft Store for Business Apps using Intune – Fig.3
Once you click the Get the App button, the WhatsApp application will be purchased and added to your Microsoft private store.
You have successfully added the WhatsApp Beta app to the private store.
This app will be available in the admin console after the next MSfB sync with Intune.
Click Close to continue.
How to Deploy Microsoft Store for Business Apps using Intune – Fig.4
Initiate a Manual Sync between Intune Portal and Microsoft Store for Business
Let’s Initiate a Manual Sync between Intune Portal and Microsoft Store for Business. If I’m not mistaken, the schedule sync will happen every 24 hours.
Login to Endpoint.Microsoft.com
Navigate to Tenant Administration – Connectors and Tokens.
Enabling Microsoft Store for Business sync lets you access volume-purchased apps with Intune. Two options must always be enabled for this scenario.
First, you must sign up and associate your Microsoft Store for Business account with Intune. Open the business store
Choose the language in which apps from the Microsoft Store for Business will be displayed in the Intune console Language:
Enable
Disable
Sync the apps you’ve purchased from the store with Intune. To reflect the newly purchased application WhatsApp, click the SYNC button on the client and wait for the sync to complete.
How to Deploy Microsoft Store for Business Apps using Intune – Fig.5
Deploy Microsoft Store App to Windows 11/10 using Intune
Let’s check how to Deploy the Microsoft Store App to Windows 11/10 using Intune. Let’s head over to Apps and check for the WhatsApp Beta application.
Deploy Microsoft Store App to Windows 11/10 using Intune
Open Intune portal.
Navigate to All Apps and Search for WhatsApp.
How to Deploy Microsoft Store for Business Apps using Intune – Table 1
How to Deploy Microsoft Store for Business Apps using Intune – Fig.6
Click on the WhatsApp application to start the deployment process. This is the typical deployment process for the Intune application. The application is created automatically when you sync Intune and Microsoft Store for Business.
You can assign applications to at least one group. Click ‘Properties‘ and edit ‘Assignments‘ to start the assignment.
How to Deploy Microsoft Store for Business Apps using Intune – Fig.7
I have deployed this as an available application to an Azure AD group of USERS.
How to Deploy Microsoft Store for Business Apps using Intune – Fig.8
End-User Experience of App installation on Windows 10 device
How to Deploy Microsoft Store for Business Apps using Intune – Video 1
Enable and Configure Microsoft Store for Business
First, we must sign up and associate the Microsoft Store for Business (MSfB) account with Intune. Then, we must accept the agreement and consent for Windows Store for Business.
How to Deploy Microsoft Store for Business Apps using Intune – Fig.9
Intune and Microsoft Store for Business Connection
You must open the Intune portal (Azure) to enable and configure Microsoft Store for Business. Microsoft Intune – Mobile Apps- Windows Store for Business. Choose the language in which Windows Store for Business apps will be displayed in the Intune console.
Once you sign up for the Windows Store for Business, you need to connect Intune with the store. This is required to Deploy Windows Store Apps via Intune. Click on the Manage tab and select Store Settings.
Once you are in store settings, you can see three out-of-box connections configured to deploy Windows Store for business apps via MDM solutions. Airwatch, MobileIron Cloud, and Microsoft Intune were the three connections created. Click on the Intune activate button to set up the connection between the store and Intune.
How to Deploy Microsoft Store for Business Apps using Intune – Fig.10
Sync the Applications and Deploy Applications via Intune
Once the Intune connection is activated, we must shop the apps and add them to your organization’s private store. It could take 24 hours (it’s pretty fast nowadays. Within minutes, it will be available) to reflect the newly added apps appearing in the private store. You can sync Intune to get the newly added apps into Intune.
We need to save the settings after the app syncs successfully.
Updated NOTE! You can now log in to the Microsoft Endpoint Manager Admin center and head to Tenant Administration—Connectors and Tokens. Then, click the SYNC button to make the application available in Intune applications.
Login to Endpoint.Microsoft.com and Navigate to Tenant Administration – Connectors and Tokens.
How to Deploy Microsoft Store for Business Apps using Intune – Fig.11
After a successful connection, you can see the following settings in Microsoft Store for Business.
How to Deploy Microsoft Store for Business Apps using Intune – Fig.12
How to Deploy Microsoft Store for Business App from Intune
Learn How to Deploy Microsoft Store for Business Apps from Intune. It would help if you headed to Apps – Windows node in the MEM Admin center portal (Intune) to search for application availability there. After the successful sync between Intune and Microsoft Store for Business, the Firefox browser app will be available in the MEM Intune portal.
Select the Windows Store apps you want to deploy to AAD user groups. We only have two options when deploying the Windows Store app via Intune. And those are REQUIRED and UNINSTALL.
So, there is no option to deploy the Windows Store app as an available deployment via Intune because the users already have access to the Windows Private Store.
How to Deploy Microsoft Store for Business Apps using Intune – Fig.12
End-User Experience of App Installation on Windows 10 Device
The end-user experience for Windows 10 1703 users is flawless. The deployment of the Windows Store app via Intune happened in the background, and the user’s name came to know about the installation on their Windows 10 device.
How to Deploy Microsoft Store for Business Apps using Intune – Fig.13
We are on WhatsApp now. To get the latest step-by-step guides, news, and updates, Join our Channel. Click here. HTMD WhatsApp.
Author
Anoop C Nair is Microsoft MVP! He is a Device Management Admin with more than 20 years of experience (calculation done in 2021) in IT. He is a Blogger, Speaker, and Local User Group HTMD Community leader. His main focus is Device Management technologies like SCCM 2012, Current Branch, and Intune. He writes about ConfigMgr, Windows 11, Windows 10, Azure AD, Microsoft Intune, Windows 365, AVD, etc.